Phishing Emails Impersonate ChatGPT to Steal Account Credentials
Summary
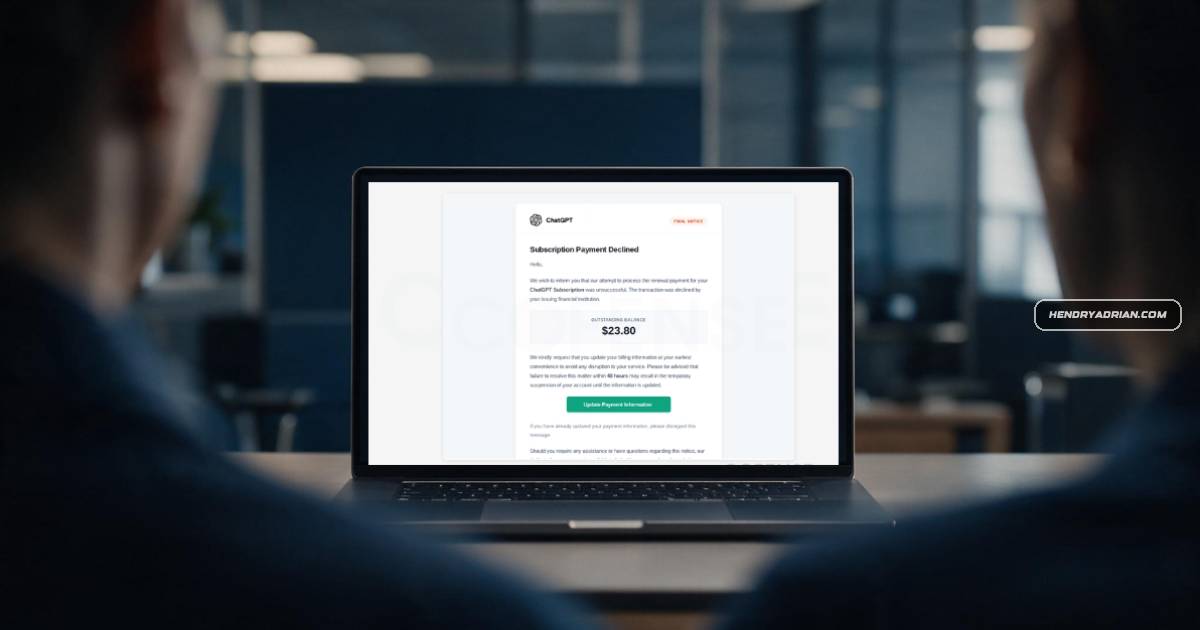
Cofense identified a fake ChatGPT subscription invoice that uses urgency and a Google API redirect to send users to a lookalike login page, where entered credentials are stolen.
Key points
- The phishing email claims a subscription payment needs updating and pressures recipients to act within 48 hours.
- It uses the real ChatGPT logo and OpenAI branding, but comes from a non-OpenAI address.
- The payment button uses a Google API redirect that leads to a lookalike ChatGPT login page hosted at e83cedb076[.]nxcli[.]io.
- Credentials entered on the fake page are sent to the attacker; the victim is then redirected to an error page.
- Check the sender address and confirm the login domain is auth[.]openai[.]com before entering credentials.
Article Details
- Event Type
- Phishing email impersonating a ChatGPT subscription payment notice
- Impact
- The phishing page was designed to steal OpenAI account credentials and payment information. Cofense reports that credentials entered on the page were sent to the attacker, but does not report a confirmed number of affected accounts.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
support@9527db6e1a[.]nxcli[.]io | Sender address used for the fraudulent subscription invoice email. | |
| URL | hxxps[:]//e83cedb076[.]nxcli[.]io/fertaq/app/key[.]php | Observed payload URL for the phishing attempt. |
| URL | hxxps[:]//e83cedb076[.]nxcli[.]io/fertaq/app/login[.]php | Observed payload URL for the phishing attempt. |