ReliaQuest Details GreyMatter Attack for Agentic Red-Team Validation
Summary
ReliaQuest describes GreyMatter Attack, a platform feature that runs approved attack campaigns against an organization's environment, scores detection and response, and helps teams address and revalidate security gaps.
Key points
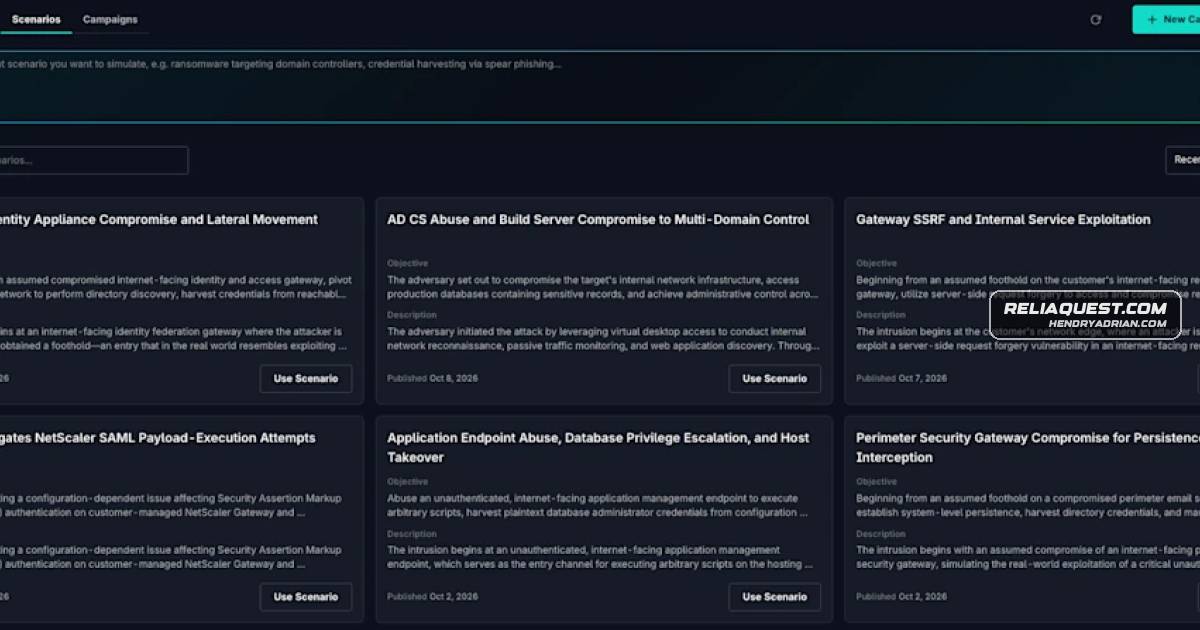
- Teams can build campaigns from threat advisories, plain-language descriptions, predefined scenarios, or uploaded penetration-test reports.
- The platform maps likely attack paths into a campaign plan that users can review and edit before execution.
- Two agents divide the work: the Marshal models the environment and scores results, while the Attacker operates from the approved plan without access to detections or incidents.
- New attack branches pause for human approval; code-enforced restrictions, rules of engagement, human gates, and audit logging are described as safety controls.
- Results include scores for attacker progress, defense performance, and coverage, with gaps ranked by technique severity and asset criticality.
- GreyMatter correlates authorized test activity and automatically closes test-generated findings with a security-control-testing audit note.
- Teams can rerun attack paths after remediation and compare results to check whether identified gaps were closed.
Article Details
- Event Type
- ReliaQuest introduced GreyMatter Attack, an agentic red-team testing capability built into its GreyMatter platform.
- Impact
- Enables organizations to run approved attack campaigns against their own environments, assess detection and response coverage, and remediate and revalidate identified gaps. The article describes product capabilities and does not report a specific incident or customer impact.
Vendors
Products
GreyMattervalidating their security with point-in-time tests and disconnected tools. That gap is why we built GreyMatter Attack.GreyMatter Attackvalidating their security with point-in-time tests and disconnected tools. That gap is why we built GreyMatter Attack.GreyMatter IntelTeams can build a campaign from threat advisories in GreyMatter Intel, a plain-language description, premade scenarios built by our red team, uploaded penetration test reports, and more. From there, Attack follows six