Black Hat and DEF CON 2026: 10 Cybersecurity Conference Highlights
Summary
A roundup of Black Hat and DEF CON 2026 highlights covers CloudShell security research, indirect prompt injection risks in AI agents, threat actor trial abuse, education-sector breaches, and hands-on security events.
Key points
- Researchers described CloudShell IAM weaknesses, including websocket sessions that can outlive API token revocation, and presented the CloudBasher toolkit.
- A DEF CON demonstration showed how indirect prompt injection through Sentry telemetry and MCP could lead an AI coding agent to act on attacker-controlled instructions.
- A Huntress presentation revisited a threat actor who installed the company's agent during a trial, exposing malicious activity and workflows.
- A discussion on education-sector security covered the 2024 PowerSchool intrusion and a 2026 Canvas/Instructure breach claim, along with advice including MFA and password managers.
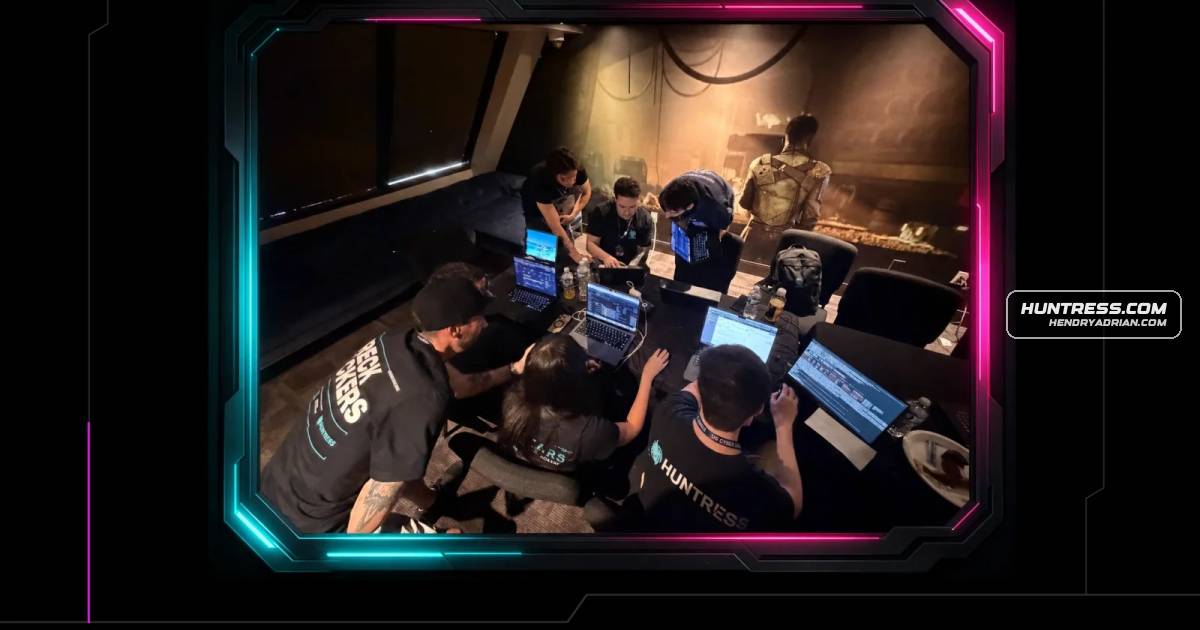
- Conference activities included a simulated SOC incident-response competition, hands-on security labs, and AI-assisted vishing demonstrations.
- The roundup also highlighted collaboration among government agencies, private-sector researchers, and the hacker community.
Article Details
- Event Type
- Cybersecurity conference and research highlights from Black Hat and DEF CON.
- Impact
- The article describes research into cloud terminal identity and access management weaknesses and indirect prompt injection through AI agents. It also reports that attackers claimed to have stolen 275 million records in the 2026 Canvas/Instructure breach; this figure is an attacker claim, not independently confirmed in the article. The 2024 PowerSchool intrusion exposed personal information for 62 million students and 9.5 million educators.
People
Adrian GarciaHuntress SOC analyst who represented a region in the HackTheBox SOC Showdown.Andrew BrandtPrincipal threat intelligence incident commander who helped at Malware Village.Austin WorlineSecurity operations analyst who helped at Malware Village.Caitlin SarianParticipated in a conversation about education-sector breaches; also identified in the article as Cybersecurity Girl.Chris RyanPrincipal Security Researcher who presented research into CloudShell and demonstrated CloudBasher.Christina ParryStaff software engineer who led a panel at Blue Team Village.Dani LopezHuntress SOC analyst who represented a region in the HackTheBox SOC Showdown.Jamie DumasHuntress SOC analyst who represented a region in the HackTheBox SOC Showdown.Jamie LevySenior director of Adversary Tactics who presented lessons from a threat actor trial abuse incident.Jen EasterlyFormer CISA Director who participated in a conversation about breaches in the education sector.Jenko HwongPrincipal Security Researcher who presented research into CloudShell and demonstrated CloudBasher.Logan MacLarenStaff offensive security engineer who led a command and conquer workshop at Red Team Village.Luke WilkinsonHuntress SOC analyst who represented a region in the HackTheBox SOC Showdown.Tanner FilipHuntress SOC analyst who represented a region in the HackTheBox SOC Showdown.
Threat Actors
Vendors
Amazon Web ServicesThe research involved reverse-engineering the private REST and websocket protocols behind AWS, Azure, and GCP CloudShell terminals, along with analyzing browser authentication flows connecting cookies to OAuth tokens.AzureThe research involved reverse-engineering the private REST and websocket protocols behind AWS, Azure, and GCP CloudShell terminals, along with analyzing browser authentication flows connecting cookies to OAuth tokens.GCPThe research involved reverse-engineering the private REST and websocket protocols behind AWS, Azure, and GCP CloudShell terminals, along with analyzing browser authentication flows connecting cookies to OAuth tokens.HuntressBehind it all, Huntress researchers were everywhere, and not just at our Black Hat booth: giving DEF CON talks, lending support to all the villages (Malware, Blue Team, Red Team, and more), and participating in theInstructureintrusion that exposed PII for 62 million students and 9.5 million educators, and the 2026 Canvas/Instructure ShinyHunters breach where the attackers claimed they stole 275 million records from nearly 9,000PowerSchoolCaitlin Sarian (aka Cybersecurity Girl) on major breaches in the education sector, including the 2024 PowerSchool intrusion that exposed PII for 62 million students and 9.5 million educators, and the 2026
Products
CanvasPowerSchool intrusion that exposed PII for 62 million students and 9.5 million educators, and the 2026 Canvas/Instructure ShinyHunters breach where the attackers claimed they stole 275 million records from nearlyCloudShellAt DEF CON, Principal Security Researchers Jenko Hwong and Chris Ryan detailed their research into CloudShell, a browser-based terminal that major cloud providers offer so users can manage their cloud resources withoutPowerSchoolCaitlin Sarian (aka Cybersecurity Girl) on major breaches in the education sector, including the 2024 PowerSchool intrusion that exposed PII for 62 million students and 9.5 million educators, and the 2026
Tools
CloudBashof distributed workloads with persistent storage and private networking. Jenko and Chris demonstrated CloudBash live during the session across a resilient, large-scale agent networkCloudBasher1. CloudBasher unleashedNmapstarting with basic reconnaissance and then following the breadcrumbs. The participants used tools like nmap, Wappalyzer, OWASP Amass to identify open ports, discover running processes, search for subdomains andOWASP Amassreconnaissance and then following the breadcrumbs. The participants used tools like nmap, Wappalyzer, OWASP Amass to identify open ports, discover running processes, search for subdomains and login pages and exploreWappalyzerwith basic reconnaissance and then following the breadcrumbs. The participants used tools like nmap, Wappalyzer, OWASP Amass to identify open ports, discover running processes, search for subdomains and login pages