Qakbot Affiliates Continue Phishing Campaign With Ransom Knight and Remcos
Summary
Talos links a campaign active since early August 2023 to Qakbot affiliates, who used phishing to deliver Ransom Knight ransomware and Remcos. The activity continued after the FBI seized Qakbot infrastructure, which Talos says may have affected C2 servers but not spam.
Key points
- Talos assesses with moderate confidence that Qakbot-affiliated actors continued operating after the FBI-led infrastructure seizure in late August 2023.
- The campaign, which began in early August, used phishing emails with ZIP archives containing LNK files and XLL files.
- LNK metadata matched a machine associated with earlier Qakbot campaigns, including the “AA” and “BB” campaigns.
- The LNK files used PowerShell and Explorer to access a remote WebDAV share and download the Ransom Knight payload.
- The XLL files delivered Remcos, giving the actors backdoor access alongside the ransomware.
- Talos says it has not observed Qakbot distribution in this campaign after the takedown, and suggests the operation may have seized C2 servers without disrupting phishing delivery.
Article Details
- Attack Vectors
- Phishing emails distribute ZIP archives containing LNK files and an XLL file.
- LNK files use PowerShell and Explorer to access a remote WebDAV network share over port 80 and download the Ransom Knight payload.
- The XLL file delivers the Remcos backdoor, which runs alongside Ransom Knight.
- Defensive Notes
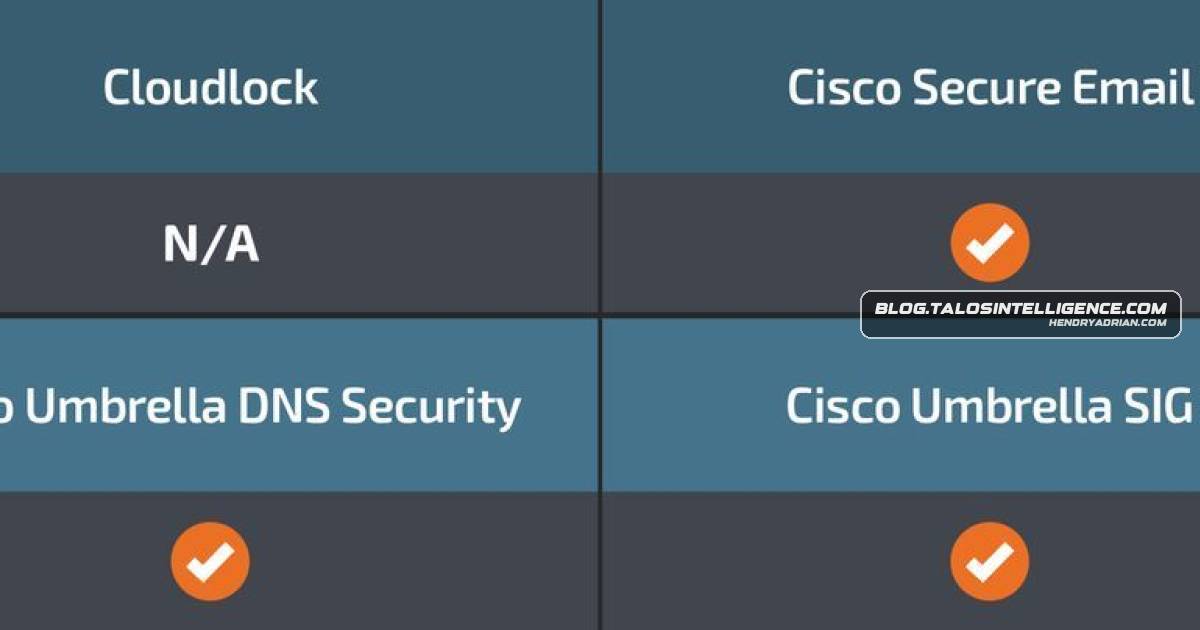
- Cisco Secure Email can block malicious campaign emails; Cisco Secure Web Appliance and Umbrella can prevent access to malicious websites, domains, IPs, and URLs.
- Cisco Secure Endpoint, Secure Firewall, Secure Malware Analytics, and ClamAV provide detections or protections for the reported malware.
- Cisco Duo provides multi-factor authentication to restrict network access to authorized users.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 89[.]23[.]96[.]203 | Remote WebDAV host used to deliver the Ransom Knight payload. |
MITRE ATT&CK
People
Malware
Cyclopsand have been conducting a new campaign that started just before the takedown, distributing a variant of Cyclops/Ransom Knight ransomware along with the Remcos backdoor. We tracked this new activity by connecting theQakbotQakbot-affiliated actors distribute Ransom Knight malware despite infrastructure takedownRansom KnightQakbot-affiliated actors distribute Ransom Knight malware despite infrastructure takedownRemcosThe threat actors behind the Qakbot malware have been conducting a campaign since early August 2023 in which they have been distributing Ransom Knight ransomware and the Remcos backdoor via phishing emails.
Vendors
Products
Adaptive Security ApplianceCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network.Cisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here.Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here.Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.Cisco Secure Web ApplianceCisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks.ClamAVClamAV detections are available for this threat:Firewall Management CenterAdditional protections with context to your specific environment and threat data are available from the Firewall Management Center.Meraki MXCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.SecureXSecureXThreat Defense VirtualCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Threat GridCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.UmbrellaUmbrella, Cisco's secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs, and URLs, whether users are on or off the corporate network. Sign up for a free trial of Umbrella here.