
Hunt.io Launches AttackCapture to Index Attacker Tools and Techniques
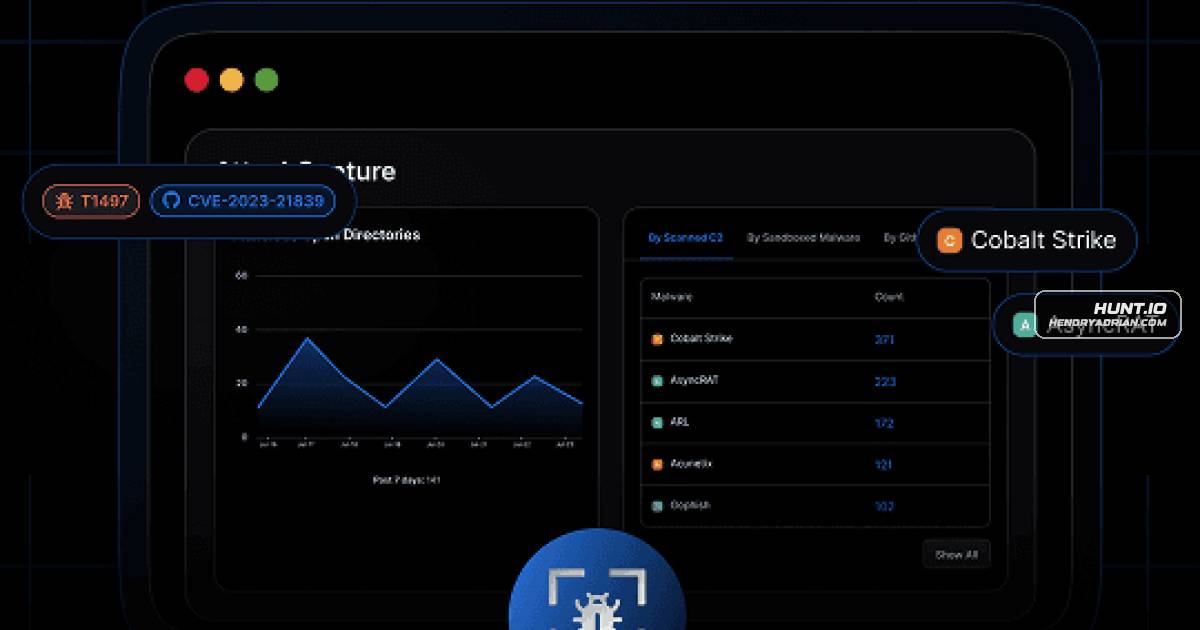
Summary
Hunt.io says AttackCapture indexes attacker infrastructure and tooling, including malware, exploits, and credentials, with features for searching files, mapping MITRE ATT&CK techniques, and supporting threat hunting and defense.
Key points
- AttackCapture identifies attacker burner instances and indexes and categorizes the tools and files found there.
- The platform maps sandboxed items to MITRE ATT&CK techniques across Enterprise, ICS, and Mobile.
- Full-text search spans archived code and text files to help find exploits, reverse shells, and other patterns.
- It can flag credentials and search directories associated with attributed IOCs, scanned C2 servers, and identified malware signatures.
- Hunt.io says it has expanded automatic sandboxing and added analyst-written observations of notable directories.
Article Details
- Event Type
- Product launch and feature update
- Impact
- AttackCapture provides defenders with indexed and categorized attacker tooling and sandboxed files, plus search, credential-flagging, malware-tagging, and MITRE ATT&CK technique labeling capabilities. The article describes product features and planned additions, not a specific attack or confirmed victim impact.