
2027 Cyber Compliance Guide Maps EU and UK Requirements
Summary
A 2027 compliance guide maps fixed and pending requirements under the EU Cyber Resilience Act, NIS2 and DORA, plus the UK Cyber Security and Resilience Bill, with reporting timelines, enforcement examples and planning steps.
Key points
- The article says the Cyber Resilience Act’s full requirements apply from Dec. 11, 2027; reporting of actively exploited product vulnerabilities and severe incidents has applied since Sept. 11, 2026.
- The article reports that CRA harmonised standards and notified bodies were not yet available for manufacturers to rely on, potentially making early preparation and assessment bookings important.
- NIS2 obligations are already in force in 24 member states, while amendments remain proposed and France, Ireland and Spain had not yet transposed the directive as of November 2026.
- DORA has applied since January 2025; its first threat-led penetration testing cycle runs through 2027 and closes in January 2028.
- The UK Cyber Security and Resilience Bill had not yet become law; the article says duties may be phased in after commencement, potentially through 2028.
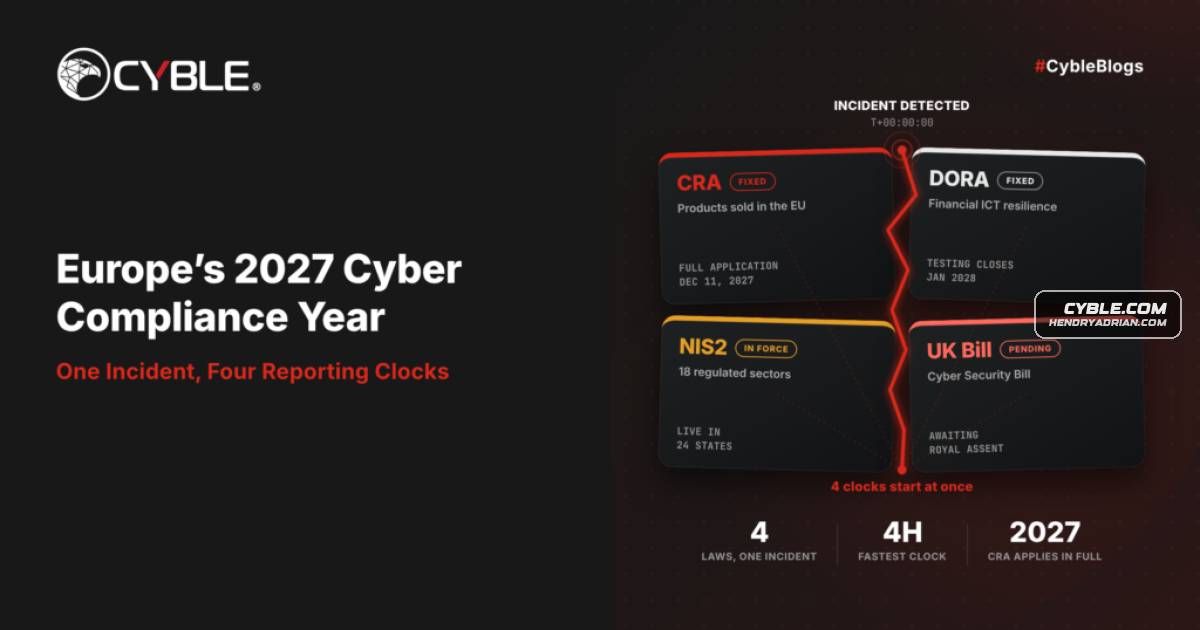
- A hypothetical incident illustrates overlapping DORA, NIS2, CRA and UK Bill reporting deadlines; the guide recommends a shared incident record, reporting matrix and supplier notification commitments measured in hours.
- The article identifies verified DORA and NIS2 fines for late reporting and registration, while saying a widely circulated German NIS2 fine could not be traced.
Article Details
- Topic
- 2027 cyber compliance deadlines and overlapping EU and UK cybersecurity regulations
Countries
AustriaAustria’s FMA fined Western Union International Bank €42,000 under DORA (July 14, 2026) Verified Repeatedly late incident reports under DORA’s reporting rulesFranceFrance, Ireland and Spain still had no national NIS2 law in force in November 2026, and the Commission referred late countries to the EU Court of Justice in July.IrelandFrance, Ireland and Spain still had no national NIS2 law in force in November 2026, and the Commission referred late countries to the EU Court of Justice in July.RomaniaRomania’s DNSC fined a public body 50,000 lei, about €10,000, under NIS2 (Sept. 29, 2026) Verified Missing the deadline to notify the authority that it was in scopeSpainFrance, Ireland and Spain still had no national NIS2 law in force in November 2026, and the Commission referred late countries to the EU Court of Justice in July.United KingdomThe UK’s Cyber Security and Resilience Bill is weeks or months from becoming law, with its duties phased in after that.