
ARTEX Adds an Autonomous Exploit Skill for PHP2Shell Vulnerabilities
Summary
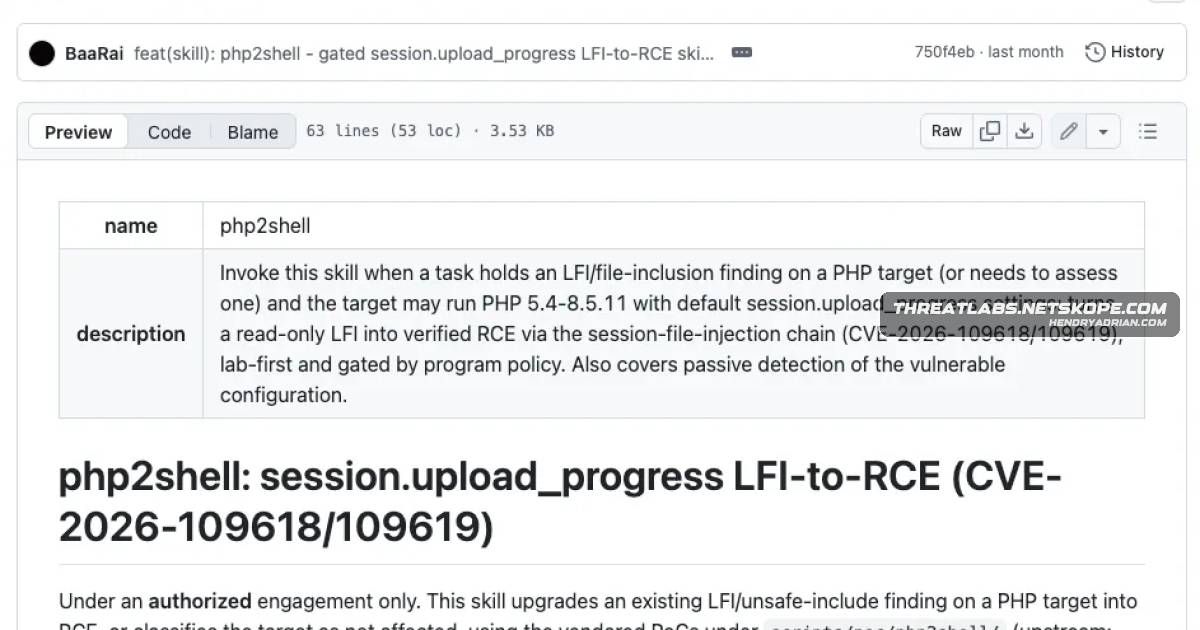
Netskope says it observed ARTEX downloads carrying a PHP2Shell skill and intense exploitation of two PHP RCE flaws. The skill automates an LFI-to-RCE chain; the article details affected versions, fixes, mitigations and ARTEX hunting indicators.
Key points
- Netskope reports observing ARTEX downloads that carried the PHP2Shell skill, alongside intense exploitation of the two vulnerabilities; it says this indicates threat actors are leveraging ARTEX’s autonomous capabilities.
- The skill targets CVE-2026-109618, a PHP memory-corruption flaw, and CVE-2026-109619, a stale-global-state flaw; both can lead to remote code execution and are listed in CISA’s Known Exploited Vulnerabilities catalog.
- The primary documented chain uses PHP’s default-enabled session.upload_progress feature to place code in a session file, then includes that file through a local file inclusion (LFI) flaw.
- The article says the skill was committed to the ARTEX successor on October 21, 2026, the day PHP released fixes, and that the successor had shipped four releases by November 18.
- Citing the Censys exposure tracker, the article reports about 27 million vulnerable PHP services, including roughly 22.8 million on branches that will not receive a fix.
- The recommended full remediation is to upgrade to PHP 8.2.35, 8.3.36, 8.4.27 or 8.5.12; disabling session.upload_progress.enabled is described as a temporary measure that blocks the demonstrated path but is not a full fix.
- Suggested ARTEX hunting indicators include the X-ARTX-KEY request header, user agents beginning with artex-enrich/ or artex-selfupdate, and ARTEX console pages.
Article Details
- Attack Vectors
- ARTEX's PHP2Shell skill uses a local file inclusion finding on a PHP target to achieve remote code execution.
- The documented chain places PHP code in a multipart upload filename, pins the session identifier, and includes the resulting PHP session file through the LFI while the upload is in progress.
- The skill automates finding an LFI and invoking the exploit chain; the article also reports two additional exploit chains marked lab-only in the skill text.
- Defensive Notes
- Upgrade PHP to 8.2.35, 8.3.36, 8.4.27, or 8.5.12, and plan migration from PHP 8.1 and older, which do not receive fixes.
- If immediate patching is not possible, disable session.upload_progress.enabled and reload or restart PHP-FPM. The article says this blocks the demonstrated path but is not a full fix.
- Treat file-inclusion findings on PHP targets as critical.
- Hunt for ARTEX traffic using the X-ARTX-KEY request header, user agents beginning with artex-enrich/ or artex-selfupdate, and ARTEX console pages.
MITRE ATT&CK
CVE
CVE-2026-109618PHP Group · PHP; Siemens · AMIS TS; +105 moreThe skill targets CVE-2026-109618 (CVSS 9.8, PHP memory corruption leading to RCE) and CVE-2026-109619 (CVSS 8.1, PHP stale global state leading to RCE).CVE-2026-109619PHP Group · PHP; Siemens · AMIS TS; +106 moreThe skill targets CVE-2026-109618 (CVSS 9.8, PHP memory corruption leading to RCE) and CVE-2026-109619 (CVSS 8.1, PHP stale global state leading to RCE).