
Rapid7 Shows Five ONLYOFFICE Docs Flaws Can Escalate View-Only Access to Container Root
Summary
Rapid7 demonstrated five ONLYOFFICE Docs vulnerabilities in 9.4.0-129, chaining view-only access to root command execution in the official container; a conditional WOPI route enabled unauthenticated entry. ONLYOFFICE says all five were fixed in Document Server 10.0.
Key points
- Rapid7 demonstrated the flaws on ONLYOFFICE Document Server 9.4.0-129; the broader affected-version range is unknown.
- CVE-2026-113627 lets a view-only token access DocBuilder file reads, including the Session JWT signing key, and supports forging credentials.
- CVE-2026-110385 and CVE-2026-97727 enable attacker-controlled file extraction or path traversal writes that can lead to code execution as ds.
- CVE-2026-113630 allows code running as ds to execute commands as root through an unsafe argument passed to a passwordless maintenance script.
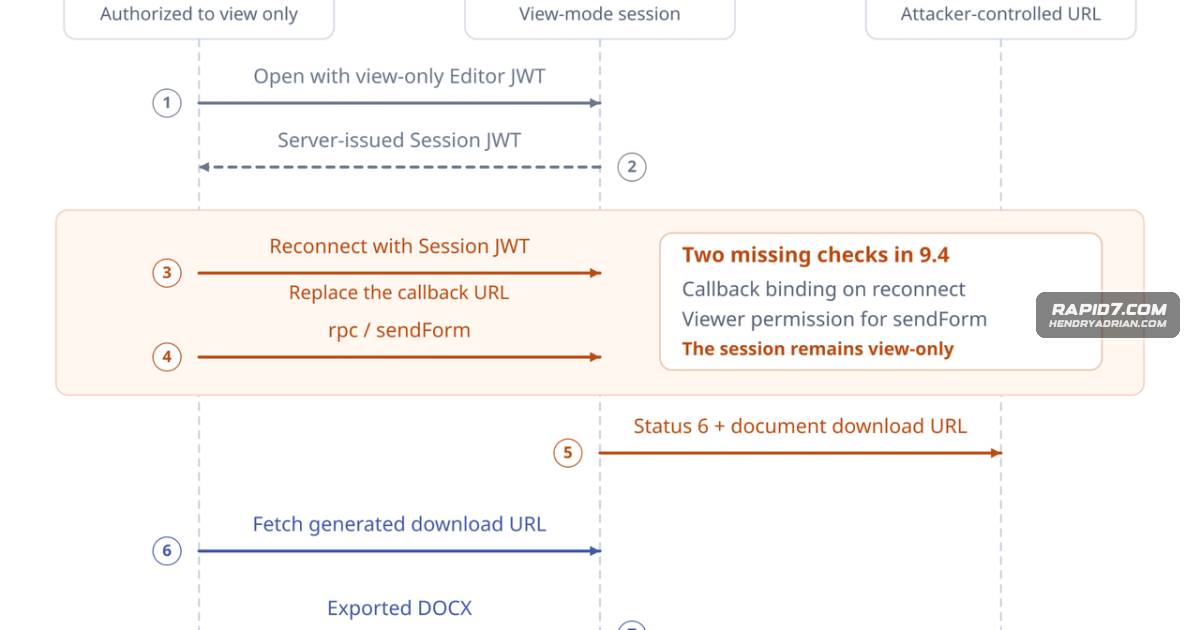
- CVE-2026-113631 lets a view-only user replace a reconnect callback and export a reconstructed DOCX containing data not shown in the viewer; the callback flaw also enables blind SSRF.
- A conditional WOPI route can provide unauthenticated entry when WOPI is enabled and the attacker-controlled source is reachable and allowed by the IP filter.
- ONLYOFFICE confirmed all five findings were fixed in Document Server 10.0; Rapid7 recommends upgrading to version 10.0 or later.
Article Details
- Attack Vectors
- A view-only Editor JWT can be reused at /docbuilder because Browser and Inbox tokens share an effective signing key and the request does not require a DocBuilder-specific token. The accepted script can read files accessible to ds, including the Session JWT signing key in the tested configuration.
- DocBuilder SaveFile conversion parameters are appended as raw XML. Duplicate task fields can override the source and destination paths and formats, letting an attacker extract an archive into a directory writable by ds and trigger execution through DocService's runtime logging configuration.
- On filesystem-storage installations, a valid Session JWT can be used with a complete-save request whose format contains traversal segments to write files writable by ds.
- The passwordless sudo policy lets ds run documentserver-flush-cache.sh with unrestricted arguments. The helper inserts the supplied hash into a sed expression without validation, enabling command execution as root.
- A view-only session can reconnect with a replacement callback URL and invoke sendForm through RPC, causing DocumentServer to send a reconstructed DOCX to the replacement callback. The callback behavior also permits blind HTTP POST requests to reachable private or loopback destinations under the tested defaults.
- With WOPI enabled, an attacker-controlled source that is reachable and allowed by the configured WOPI IP filter can provide metadata through the public launch endpoint. An empty access token and trailing-slash source URL can produce a Browser JWT accepted by /docbuilder, enabling the described chains without a pre-existing account or token.
- Defensive Notes
- Upgrade to Document Server 10.0 or later; ONLYOFFICE confirmed that version 10.0 fixes all five findings. Rapid7 tested package 10.0.0-169.
- The tested 10.0.0-169 fixes add DocBuilder-specific JWT validation, restrict native file reads to paths in the font map, filter unsafe X2T conversion parameters, and reject storage paths that escape the storage root.
- The tested 10.0.0-169 cache-flush helper validates the hash argument against an allowlist before inserting it into the sed expression.
- The tested 10.0.0-169 changes require a non-view user for sendForm and restore the stored callback URL when a Session JWT reconnects.
- The unauthenticated WOPI entry requires WOPI to be enabled and the attacker-controlled source to be reachable and permitted by the configured IP filter; WOPI is disabled by default.
MITRE ATT&CK
T1005 · Data from Local SystemGetFontBinary() was used through /docbuilder to read server-local files accessible to ds, including /etc/passwd and the Session JWT signing key configuration.T1059.004 · Unix ShellThe root-helper exploit used GNU sed's execution flag to run shell commands, including id, as root; the appender also invoked /bin/sh.T1059.007 · JavaScriptThe extracted JavaScript appender was loaded by DocService through log4js configuration and executed attacker-controlled code.T1068 · Exploitation for Privilege EscalationCommand injection through the maintenance helper elevated execution from ds to root inside the DocumentServer container.T1105 · Ingress Tool TransferThe DocBuilder proof of concept submitted a base64-encoded ZIP containing an appender, command script, and runtime configuration, then extracted those files into the Data directory.T1190 · Exploit Public-Facing ApplicationThe article demonstrates exploitation of Document Server endpoints, including /docbuilder and the WOPI public launch path, to obtain unauthorized file access, code execution, and document export.T1548.003 · Sudo and Sudo CachingThe attacker abused the sudoers permission allowing ds to run documentserver-flush-cache.sh as root without a password.T1550.001 · Application Access TokenThe stolen signing key was used to forge a Session JWT with attacker-chosen document permissions, which Document Server accepted for a save operation.T1552.001 · Credentials In FilesIn the tested configuration, the attacker read local.json and recovered the Session JWT signing key stored in its session secret.
CVE
CVE-2026-110385ONLYOFFICE · Document ServerDocBuilder conversion parameter injection enables code execution (CVE-2026-110385)CVE-2026-113627Vendor / Product unavailableEditor JWT authorizes native file reads and session JWT forgery (CVE-2026-113627)CVE-2026-113630ONLYOFFICE · Docs (Document Server)Passwordless maintenance command elevates ds to root (CVE-2026-113630)CVE-2026-113631ONLYOFFICE · Docs (Document Server)View-only sendForm exports non-rendered document data (CVE-2026-113631)CVE-2026-97727Vendor / Product unavailableComplete-save format traversal enables arbitrary file write (CVE-2026-97727)
People
Jonah BurgessRapid7 Senior Security Researcher credited with conducting the assessment and exploit-chain research.Ssani4Previously reported the GetFontBinary() and ZipFileAsString() native file-read behavior in DocumentBuilder issue #147; the article says ONLYOFFICE closed the issue as fixed in DocumentBuilder 9.2.0.
Vendors
Products
Document ServerONLYOFFICE confirmed on October 23, 2026 that all five findings were fixed in Document Server 10.0. The changelog describes the release's security changes.ONLYOFFICE DocsAs part of our research into Zimbra Collaboration Suite, Rapid7 reported five findings in ONLYOFFICE Docs. An attacker with view-only access to a document can chain vulnerabilities in ONLYOFFICE Docs to execute