
How AI Agents Can Investigate Phishing—and Where Human Review Still Matters
Summary
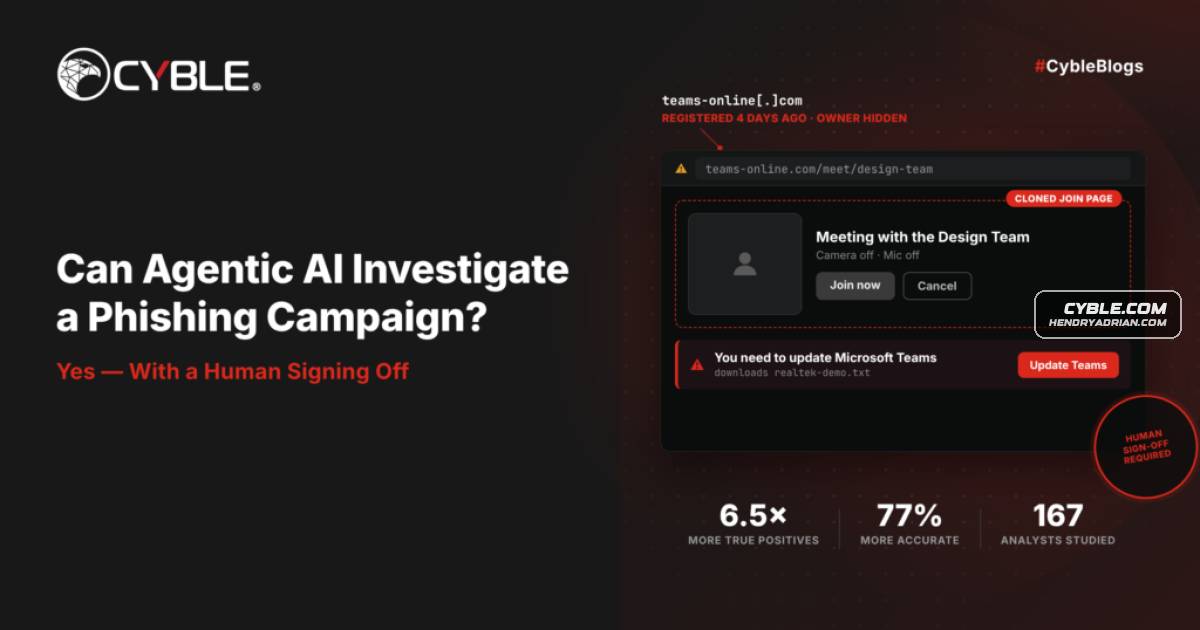
A walkthrough shows how agents could investigate lookalike Teams portals, while warning that phishing content can target AI systems with hidden instructions. The article recommends evidence trails and human approval for consequential actions.
Key points
- In a randomized trial with 167 analysts, Microsoft reported that those using its phishing triage agent were up to 77% more accurate and found up to 6.5 times as many true positives per minute. The test was limited to triage, and the agent was 100% accurate on that test corpus.
- Steven Lim’s public posts described three lookalike Teams domains, cloned join pages and delivery through search results or ads. The article presents a proposed evidence walkthrough, not results from a specific agent run.
- A page on teams-cloud[.]live displayed a fake Teams update prompt that downloaded realtek-demo.txt; the article characterizes this as a staged lure, with no executable observed.
- The proposed investigation treats a missing reputation verdict as missing data, not proof a domain is safe, and cautions that a shared registrar alone is weak evidence of a relationship.
- The article attributes reports of hidden AI-targeting instructions in phishing content to Barracuda, Sublime Security and StrongestLayer; Sublime’s researchers estimated the hidden-text technique appeared in under 1% of phishing traffic.
- Recommended safeguards include linking verdict claims to evidence, logging tool calls, separating read permissions from action permissions, and requiring human approval for blocks and takedown requests.
Article Details
- Topic
- Using agentic AI to investigate phishing campaigns, with human review to guard against prompt injection and unsupported conclusions.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | teams-cloud[.]live | Lookalike Teams portal that displayed a fake update prompt and staged a file download. |
| DOMAIN | teams-livemeeting[.]com | Lookalike Teams domain associated with sponsored-search delivery and identified as a possible campaign sibling. |
| DOMAIN | teams-online[.]com | Lookalike Microsoft Teams portal identified as part of the phishing campaign. |
MITRE ATT&CK
People
Vendors
CybleBlaze AI is Cyble’s agentic engine, and it runs across the company’s threat intelligence and digital risk protection products, where this kind of outside-in evidence lives.MicrosoftMicrosoft’s randomized trial of 167 security analysts found that its phishing triage agent made them faster and more accurate.
Products
Blaze AIBlaze AI is Cyble’s agentic engine, and it runs across the company’s threat intelligence and digital risk protection products, where this kind of outside-in evidence lives.Microsoft Defender Antimalware Platform4, 2026, through a privacy service attached to the registrar Global Domain Group, and no active verdict in Microsoft Defender threat intelligence.Microsoft TeamsThis post walks through what an agentic investigation of a real phishing campaign looks like, evidence item by evidence item, using the lookalike Microsoft Teams domains that researcher Steven Lim exposed in October.Security Copilot Phishing Triage AgentIn November 2025, Microsoft economist James Bono published a randomized controlled trial of the Security Copilot Phishing Triage Agent.