
Malicious PyPI SDK Delivers RCMD Remote Access Trojan on First Payment Request
Summary
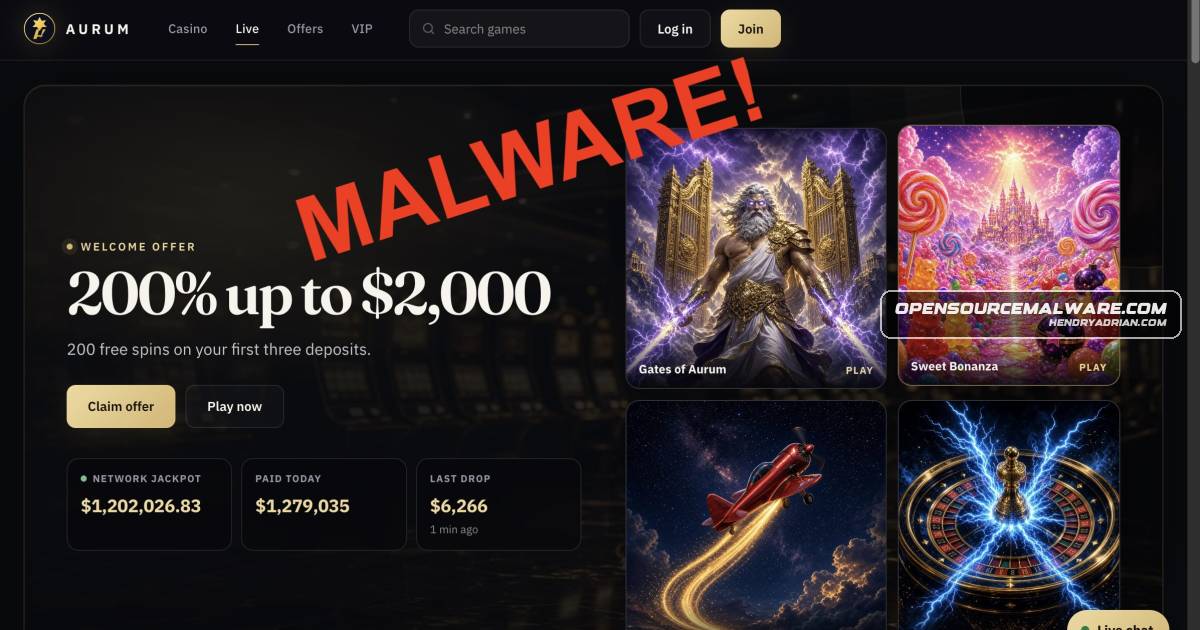
Researchers found PyPI package aurum-pay 1.2.0 runs a server-supplied command on its first payment API request, delivering the RCMD Remote Agent. The implant enables persistent shell access, file transfer, reconnaissance and screenshots.
Key points
- The malicious code is triggered by the SDK’s first real API request, not by installation or import; it fetches and executes a response from aurum-casino[.]com/sdk/ping.
- The recovered Linux command downloads and runs the implant from www[.]dropbox[.]com.
- The RCMD Remote Agent connects to 209.99.184.80:443 over TLS and supports shell access, file transfer, reconnaissance and screenshots.
- The implant persists as a fake Chromium systemd service at system or user level.
- The SDK’s default API host is also the command-delivery domain; applications may send it bearer keys, payment details and customer identifiers.
- The researchers recommend isolating affected hosts, preserving evidence, revoking accessible credentials and rebuilding from a trusted image. They reported the package and user account were still live at publication.
Article Details
- Attack Vectors
- The malicious PyPI package [email protected] activates on the first API request made through the SDK, rather than during installation or import.
- The package sends a request to https://aurum-casino.com/sdk/ping and executes the response through PowerShell on Windows or Bash on Linux and macOS.
- The recovered Linux command downloads and runs an ELF implant from a specific Dropbox URL.
- RCMD Remote Agent establishes persistence by installing a Chromium-named systemd service at the system or user level.
- The implant connects to a hard-coded controller over TLS and supports remote shell commands, file transfer, reconnaissance, and screenshot capture.
- Defensive Notes
- If aurum-pay was used in an environment, isolate affected hosts, preserve endpoint and network evidence, revoke credentials accessible to the Python process, and rebuild from a trusted image.
- Search network telemetry for connections to aurum-casino.com, especially requests to /sdk/ping, TLS sessions to 209.99.184.80:443, and access to the listed Dropbox object.
- On Linux, check for chromium.service in system and user systemd directories, /tmp/.c, /tmp/.rcmd-ss.jpg, $HOME/.local/bin/chromium, and enabled linger.
- Review process telemetry for Python spawning Bash followed by curl, /tmp/.c, systemctl, scrot, or Python screenshot commands.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | aurum-casino[.]com | First-stage command host used by the malicious SDK; the article assesses it as brand cover and threat infrastructure. |
| IPV4 | 209[.]99[.]184[.]80 | Hard-coded C2 address used by RCMD Remote Agent over port 443. |
| SHA256 | 36df147e96e7a4de151feaa2259a4e31ce0bd91b83b418c02f41735948bf5b64 | SHA-256 of the recovered /sdk/ping response used to deliver the command. |
| SHA256 | c119af2c72f0e68556fc0c7ca0c858845a04b5f46ebb31b614414a5bf470e414 | SHA-256 of the RCMD Linux ELF implant. |
| SHA256 | d6e250af80317e26d850f41d5c15e61fad4f678074a4f70695069fb6f7cab206 | SHA-256 of aurum_pay/__init__.py, identified as part of the malicious package. |
| URL | hxxps[:]//aurum-casino[.]com/sdk/ping | First-stage endpoint that returns a command executed by the SDK. |
| URL | hxxps[:]//www[.]dropbox[.]com/scl/fi/ovn8wxlle1eev6fapq8kv/rcmd-agent?rlkey=mzlx4zi0peodkv8vwdv4tr0v7&st=vv80smtk&dl=1 | Specific Dropbox-hosted URL used to download the RCMD Linux implant. |
MITRE ATT&CK
T1005 · Data from Local SystemThe operator can direct the implant to list directories, read files, and upload victim files.T1027 · Obfuscated Files or InformationThe ELF contains four obfuscated configuration blocks whose XOR transformation was reconstructed during analysis.T1036.004 · Masquerade Task or ServiceThe implant copies itself under a Chromium-themed name and uses that name for its persistence service.T1057 · Process DiscoveryThe implant searches /proc/<pid>/environ to locate graphical-session environment information.T1059.001 · PowerShellOn Windows, the package executes the server response in a hidden PowerShell job.T1059.004 · Unix ShellOn Linux and macOS, the package executes the server response through Bash; the implant also launches /bin/sh for operator commands.T1082 · System Information DiscoveryThe implant reads /etc/os-release, /proc/cpuinfo, and /proc/meminfo to collect host and system information.T1105 · Ingress Tool TransferA Bash command downloads the RCMD ELF from Dropbox, saves it as /tmp/.c, and runs it.T1113 · Screen CaptureThe implant captures screenshots using scrot, X11, or a Python Pillow fallback.T1195.002 · Compromise Software Supply ChainThe malicious aurum-pay package was distributed through PyPI and executed code when applications used its payment SDK.T1543.002 · Systemd ServiceThe implant creates a system or user systemd service named chromium.service for persistence.T1567.002 · Exfiltration to Cloud StorageThe implant supports cloud transfers, including uploading victim files through operator-supplied R2-style transfer URLs.T1573 · Encrypted ChannelRCMD Remote Agent communicates with its controller over TLS using an embedded token.