
Earth Sirrush IOC Analysis Finds 283 Email-Linked Domains and 95 Potential Victim IPs
Summary
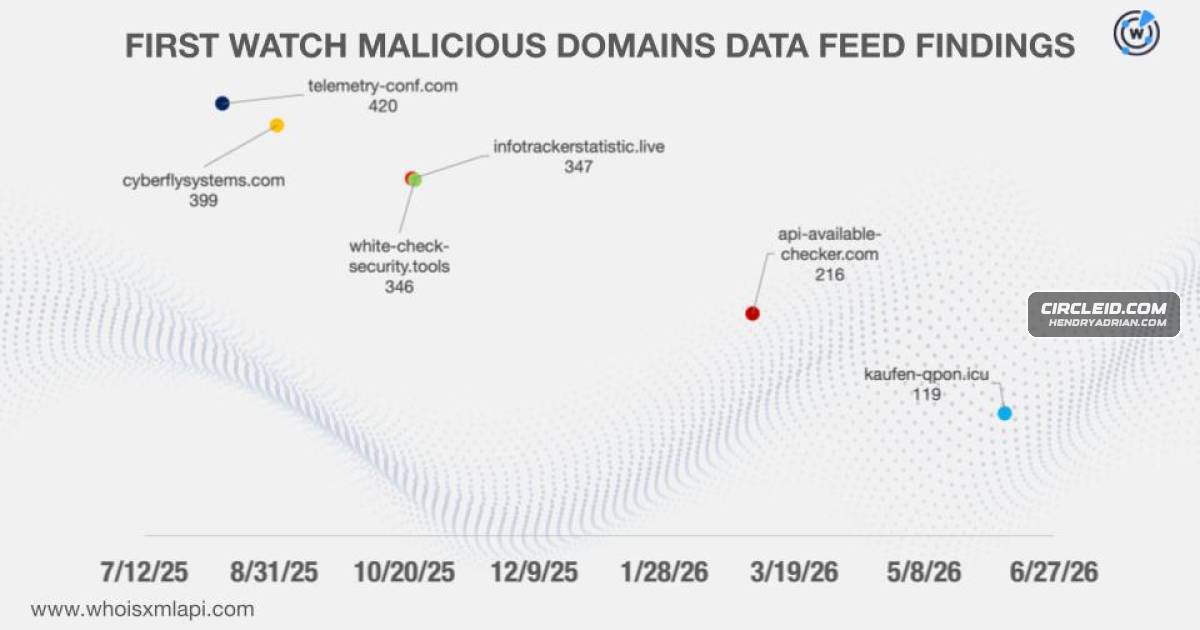
An analysis of Earth Sirrush indicators found 283 email-connected domains, six domains likely registered maliciously, and 95 potential victim IPs communicating with 11 IP indicators. The article cautions that some flagged entities may prove harmless.
Key points
- TrendAI Research tracks the Russia-aligned intrusion set as Earth Sirrush, formerly SHADOW-EARTH-065; it overlaps with CERT-UA's UAC-0099 designation.
- A TrendAI report traced the group's spearphishing operations against Ukrainian government, defense, border guard, and logistics targets from 2022 to July 2026.
- The analysis examined 49 network indicators after excluding three domains from an original set of 52.
- Six domain indicators were assessed as likely registered with malicious intent; sample network data showed 95 potential victim IPs communicating with 11 IP indicators.
- Reverse WHOIS analysis of public email indicators identified 283 unique email-connected domains; 12 had recorded visits since January 1, 2026.
- The subdomain order[.]cyberflysystems[.]com may be typosquatting the cyberfly brand; three historical IPs associated with its apex domain had links to malware distribution and phishing.
Article Details
- Attack Vectors
- Earth Sirrush reportedly launched a sustained spearphishing campaign against Ukrainian government agencies, defense organizations, border guard units, and logistics operators.
- Three historical IP addresses associated with the cyberflysystems.com apex domain were linked to malware distribution and phishing between 2023 and 2026.
- Defensive Notes
- The article recommends supplementary investigation to corroborate entities identified as threats or malicious, as assessments may change with further evidence or context.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | activation-planner[.]pro | Listed as a domain IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| DOMAIN | rutech[.]tech | Listed as a domain IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| DOMAIN | startdeeplearning[.]com | Listed as a domain IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| DOMAIN | uztickets[.]com | Listed as a domain IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| DOMAIN | virtualdailyplanner[.]pro | Listed as a domain IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| HOSTNAME | order[.]cyberflysystems[.]com | Identified as the sole subdomain IoC in the Earth Sirrush analysis; its individual malicious use is not detailed. |
| IPV4 | 135[.]181[.]41[.]169 | Historical IP associated with malware distribution and phishing between 2023 and 2026. |
| IPV4 | 185[.]53[.]46[.]190 | Listed as an IP IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| IPV4 | 35[.]187[.]82[.]108 | Historical IP associated with malware distribution and phishing between 2023 and 2026. |
| IPV4 | 62[.]210[.]204[.]94 | Listed as an IP IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| IPV4 | 64[.]95[.]13[.]21 | Listed as an IP IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| IPV4 | 65[.]108[.]39[.]53 | Historical IP associated with malware distribution and phishing between 2023 and 2026. |
| IPV4 | 85[.]209[.]195[.]161 | Listed as an IP IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
| IPV4 | 95[.]111[.]249[.]30 | Listed as an IP IoC in the Earth Sirrush analysis; the article does not specify its individual malicious activity. |
MITRE ATT&CK
Threat Actors
SHADOW-EARTH-065The article says Earth Sirrush was formerly tracked under this designation and attributes the reported spearphishing campaign to the intrusion set.UAC-0099A Russia-aligned intrusion set that TrendAI Research reports launched a sustained spearphishing campaign against Ukrainian organizations.
Countries
Russiagovernment agencies, defense organizations, border guard units, and logistics operators launched by the Russia-aligned intrusion set they track as Earth Sirrush, formerly SHADOW-EARTH-065 that overlaps with theUkraineSHADOW-EARTH-065 that overlaps with the UAC-0099 designation by the Computer Emergency Response Team of Ukraine (CERT-UA).
Industries
DefenseTrendAI Research uncovered a sustained spearphishing campaign targeting Ukrainian government agencies, defense organizations, border guard units, and logistics operators launched by the Russia-aligned intrusion set theyGovernmentTrendAI Research uncovered a sustained spearphishing campaign targeting Ukrainian government agencies, defense organizations, border guard units, and logistics operators launched by the Russia-aligned intrusion set theylogisticscampaign targeting Ukrainian government agencies, defense organizations, border guard units, and logistics operators launched by the Russia-aligned intrusion set they track as Earth Sirrush, formerly