
AccessPay DMARC Misconfiguration Could Have Exposed Email Infrastructure Data
Summary
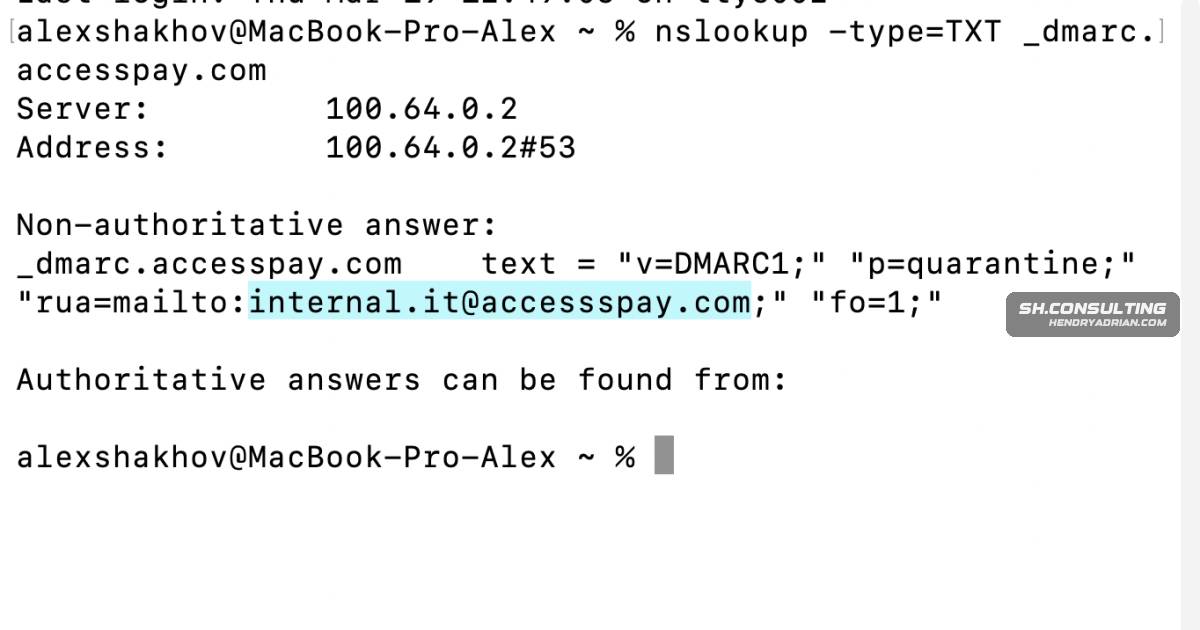
A researcher says AccessPay’s DMARC reports went to an exposed reporting domain. They registered accessspay[.]com but enabled no mailboxes. AccessPay later removed the endpoint from its DMARC policy, which the researcher says leaves it without those reports.
Key points
- The article says AccessPay’s DMARC RUA tag directed reports to a potentially registrable domain, risking exposure of infrastructure, recipient, communication-pattern, and traffic-volume data.
- After months of unsuccessful reporting, the researcher says they registered accessspay[.]com to prevent potential exposure. They enabled no mailboxes; receipt of customer communications was described as only highly likely.
- The researcher says AccessPay later removed the reporting endpoint from its DMARC policy, leaving the organization without those reports.
- The article says the last DMARC update appeared to be in early 2024.
Article Details
- Event Type
- DMARC reporting misconfiguration exposing email infrastructure data
- Impact
- AccessPay directed DMARC reports to the registerable domain accessspay[.]com, creating a risk that whoever registered it could map infrastructure, communication patterns, recipient data, and traffic volumes. The article says the researchers registered the domain to prevent potential exposure, did not enable mailboxes, and reports of customer communications being received are unconfirmed. AccessPay later removed the reporting endpoint from its DMARC policy, which the article says leaves the organization without those reports for monitoring email security incidents.