
DMARC p=reject Reduces Spoofing but Cannot Guarantee Protection
Summary
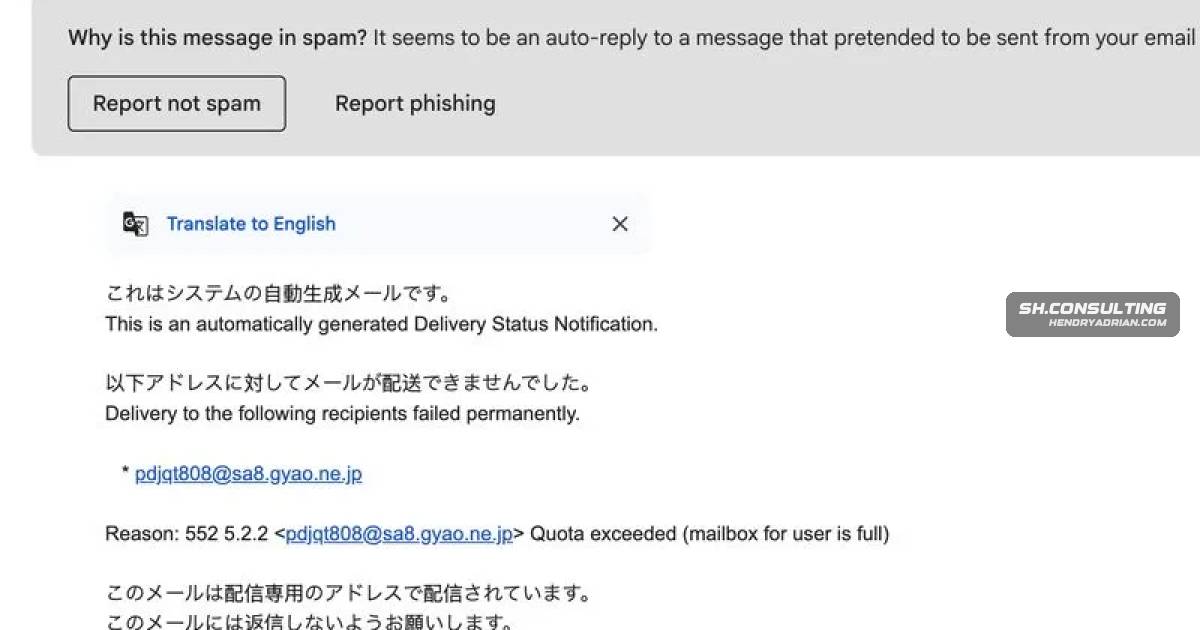
DMARC p=reject can reduce spoofing, but recipient servers decide how to handle failing messages. The article reports that So-Net accepted spoofed messages despite failed SPF and DKIM checks, with related rejections attributed to full inboxes.
Key points
- DMARC p=reject tells receiving servers how the domain owner wants messages that fail authentication handled, but does not compel recipient servers to reject them.
- The article reports that So-Net accepted spoofed emails despite failed SPF and DKIM checks, illustrating that recipient-side handling can vary.
- The author's analysis involved spoofed messages targeting a three-character .com domain resembling YKK.
- The article says some rejections were due to 552 5.2.2 / quota exceeded rather than authentication failure.
- Strict DMARC can reduce spoofing risk, but the article cautions that it does not guarantee protection across all recipient providers.
Article Details
- Topic
- DMARC p=reject reduces email spoofing but cannot guarantee protection when receiving mail servers do not enforce the policy.