
Suspicious Google Calendar Invites Trigger DMARC Failures
Summary
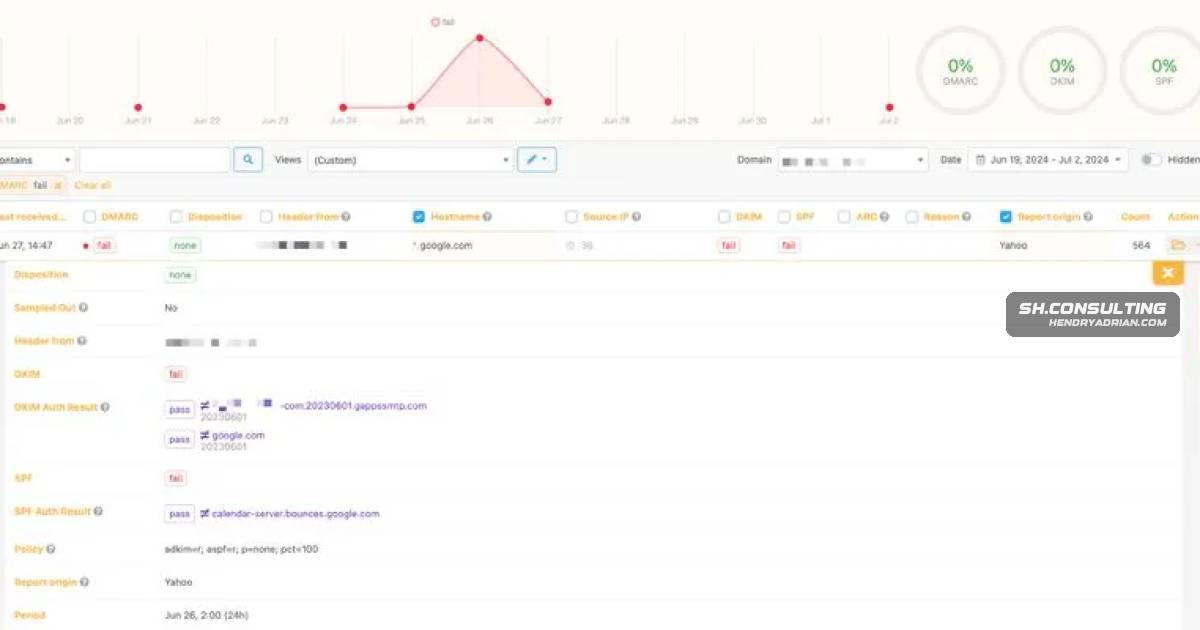
A security consultant says DMARC reports showed suspicious Google Calendar invites routed to Yahoo users, including 561 in one day. The affected company confirmed the invites were illegitimate; the post provides no technical evidence for the suspected exploit.
Key points
- URIports reports showed an increase in DMARC failures for a monitored domain.
- The observed traffic came from Google servers, passed through Google Calendar servers, and was directed to Yahoo users.
- The author counted 561 Google Calendar invites on June 26; the affected company confirmed they were not legitimate.
- The author says the domain's DMARC policy was not yet enforced because it had been monitored for only two weeks.
- The post suggests attackers may still be abusing Google Calendar to send phishing emails, but does not explain or independently establish the suspected exploit.
Article Details
- Event Type
- Phishing campaign using illegitimate Google Calendar invites, which caused messages to fail DMARC validation.
- Impact
- The article reports 561 invites sent on June 26 to Yahoo users through Google Calendar servers. The affected company confirmed the invites were not legitimate. The author suggests that vulnerabilities may still allow this activity despite a reported patch, and says other users could potentially be affected.