
Email Authentication Supports Deliverability but Requires Ongoing Maintenance
Summary
The article explains how DKIM, SPF and DMARC support email authentication, notes bypass tactics such as replay and SubdoMailing, and recommends rotating DKIM keys, monitoring SPF and enforcing a strict DMARC policy.
Key points
- The article describes DKIM as verifying sender identity, SPF as authorizing sending servers, and DMARC as aligning DKIM and SPF with the sender’s domain.
- It names DKIM replay, SPF replay and SubdoMailing as tactics that can bypass DMARC protections.
- It recommends regularly rotating DKIM keys, maintaining and monitoring SPF records, and enforcing and monitoring a strict DMARC policy.
- The article argues that domain authentication should be configured for security, not solely to improve email deliverability.
Article Details
- Defense Focus
- Improve email security through domain authentication, rather than relying on basic authentication settings solely to improve deliverability.
- Detection Methods
- Monitor SPF configuration and the servers authorized to send email for the domain.
- Continuously monitor DMARC compliance.
- Data Sources
- Domain SPF, DKIM, and DMARC records
- Email-sending server configuration
- Defensive Actions
- Rotate DKIM keys regularly.
- Configure SPF for the root domain and monitor authorized sending servers.
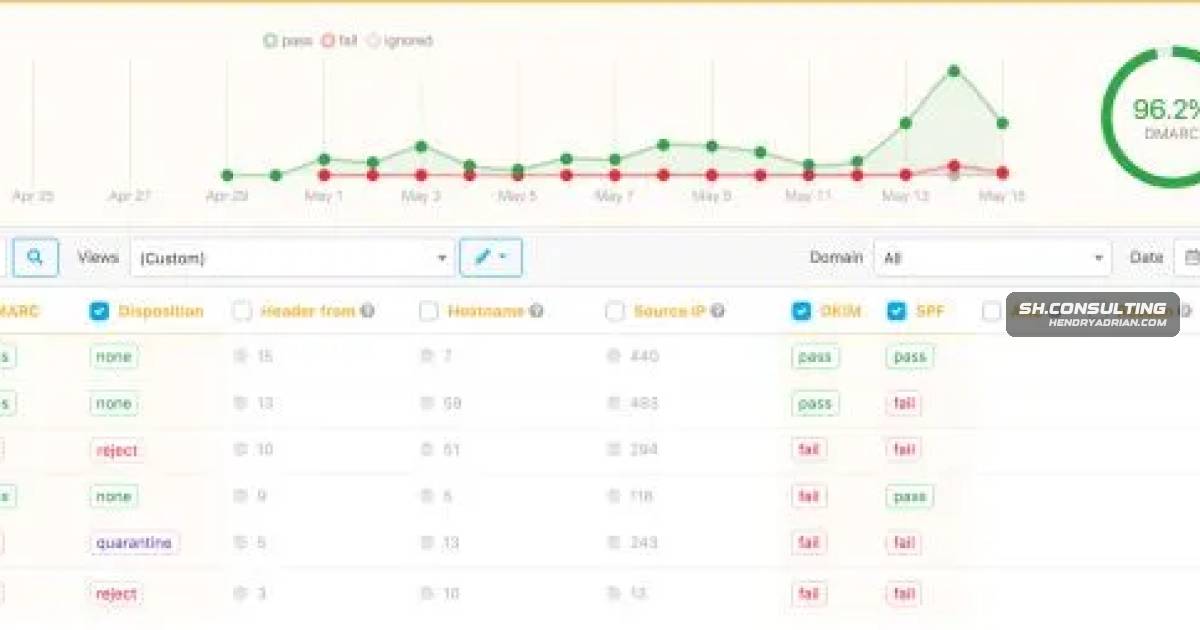
- Set DMARC to a strict compliance framework and monitor it continuously; do not treat p=none as a lasting security solution.
- Account for the article's warning that DKIM replay, SPF replay, and SubdoMailing can bypass DMARC p=reject.