
RFC 9989 Updates DMARC With a New Subdomain Policy and DNS Tree Walk
Summary
RFC 9989 replaces prior DMARC specifications without breaking existing records. It adds the np tag for nonexistent subdomains, replaces PSL-based discovery with a DNS tree walk, and replaces pct with test-mode t; the article recommends record updates.
Key points
- RFC 9989, published as a Proposed Standard in May 2026, obsoletes RFC 7489 and RFC 9091; existing DMARC records continue to work.
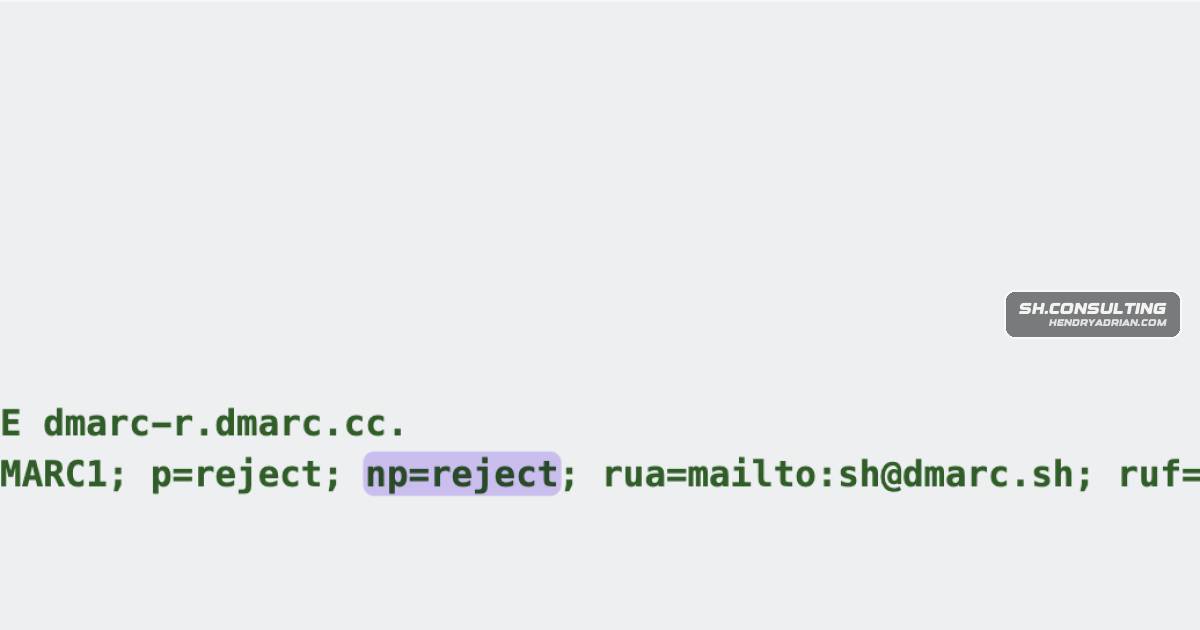
- The new np tag sets policy for nonexistent subdomains. If absent, receivers fall back to sp, then p; the article recommends np=reject.
- A DNS Tree Walk replaces the Public Suffix List for finding the Organizational Domain, with the process capped at eight DNS queries.
- RFC 9989 removes pct, rf, and ri. The t tag provides a test mode that lowers enforcement for failing messages; it does not change aggregate report generation.
- Mailing lists and forwarders can disrupt SPF or DKIM alignment. The RFC documents the tradeoffs but does not provide a protocol-level fix.
- The article advises removing obsolete tags, adding np=reject, and considering p=quarantine for organizations whose employees send mail to mailing lists.
Article Details
- Event Type
- Publication of RFC 9989, a Proposed Standard updating the DMARC specification.
- Impact
- RFC 9989 replaces RFC 7489 and RFC 9091 without breaking existing DMARC records. It adds the np tag for policies on non-existent subdomains, replaces Public Suffix List lookup with a DNS Tree Walk, replaces pct with the t test-mode tag, and removes pct, rf, and ri. The article recommends adding np=reject and removing obsolete tags. It also notes that receiver-side policy discretion remains, and that strict DMARC enforcement can affect mailing-list delivery when intermediaries break SPF or DKIM alignment.