
Study Finds 43 U.S. Government Domains With Dangling DNS Dependencies
Summary
SH Consulting scanned 25,964 U.S. government-related domains and found 43 with expired, mistyped or repurposed DNS dependencies. The flaws could enable email spoofing, mail interception, DNS control or exposure of DMARC reports; researchers registered 17 domains andแจ?
Key points
- SH Consulting scanned 25,964 government-related domains twice in 2026: 16,984 .gov domains and 8,980 on other top-level domains.
- Researchers found 43 government domains still referencing DNS dependencies outside their control; they defensively registered 17 dependencies and reported findings to CISA and MS-ISAC.
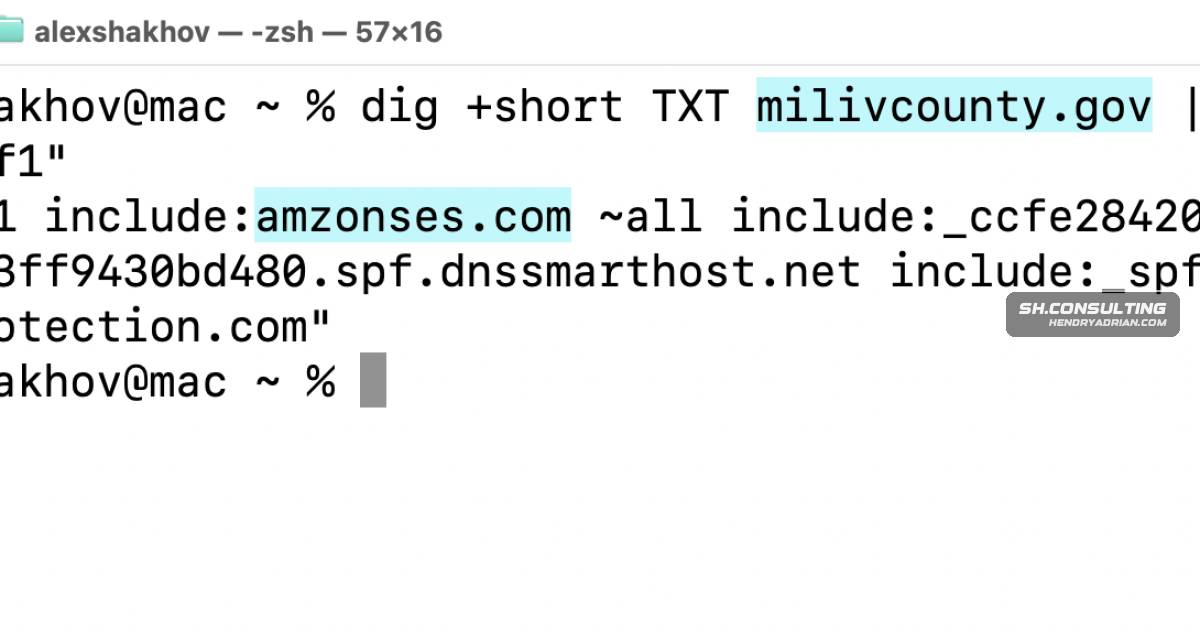
- A Livingston County, Michigan SPF typo authorized at least 32,066 unique IPv4 addresses, and the saved DNS responses showed SPF and DMARC passing. That count does not establish how many senders had access or whether they used it.
- The study found eight unregistered DMARC reporting endpoints set to receive reports for 11 government institutions, potentially exposing email infrastructure and communication patterns.
- Researchers found MX records pointing to typo domains; they could not confirm that any were intercepting mail, though some were configured to accept incoming messages.
- The former City of Heyburn domain now serves a casino page and uses attacker-controlled nameservers; the article says it is also configured to send and receive email for the former government domain.
- More than 12,000 of the scanned domains had no DMARC policy, leaving them without that protection against spoofing.
Article Details
- Publisher
- SH Consulting
- Report Period
- DNS scans conducted in June and October 2026; report dated 2026-11-05
- Scope
- US government-related domains and their external DNS and email dependencies
- Sample Size
- 25,964 government-related domains: 16,984 ending in .gov and 8,980 on other TLDs
- Key Statistics
- 43 government domains still referenced domains outside their control at the time of reporting.
- The Livingston County SPF dependency was reported to authorize at least 32,066 unique IPv4 addresses to send mail on its behalf; this is not a count of senders or actual abuse.
- SH Consulting defensively registered 17 domains: three SPF dependencies, six MX domains, and eight DMARC reporting domains.
- 12,252 of the 25,964 scanned domains had no DMARC policy; this included 7,223 of the 16,984 .gov domains.
- About 27% of the 25,964 government domains pointed to self-hosted mail servers for inbound mail.
- Recommendations
- Conduct regular infrastructure audits to identify invalid or typoed MX records and other external DNS dependencies.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | amasonses[.]com | Misspelled SPF dependency in Pikeville's record; the article links it to an investigation of SubdoMailing and reports that associated IPs are listed by blocklist operators, while noting the operator's current involvement is unconfirmed. |
| DOMAIN | ambertrail[.]fightingfit[.]uk[.]com | Current SPF include destination reported for the suspicious amzonses.com infrastructure as of November 3, 2026. |
| DOMAIN | amzonses[.]com | Misspelled SPF dependency in Livingston County's record; the article reports rotating SPF infrastructure and identifies it as the source of a snowshoe sending operation. |
| DOMAIN | brainydns[.]com | Nameserver domain used during a one-week period for oldhamcounty.net and associated in cited Infoblox research with a portfolio operator that rotates nameservers and sells visitor traffic to malicious advertisers. |
| DOMAIN | coremalware[.]com | The article identifies this as an attacker-controlled nameserver domain used for the former City of Heyburn domain, which attackers also configured to send and receive email. |
| DOMAIN | hastydns[.]com | Nameserver domain associated in cited Infoblox research with a portfolio operator that rotates nameservers and sells visitor traffic to malicious advertisers. |
| DOMAIN | heyburnidaho[.]org | Former City of Heyburn domain no longer owned by the city; the article reports it is controlled by attackers, serves a casino login and deposit page, and is configured to send and receive email as the domain. |
| DOMAIN | koaladns[.]com | Nameserver domain associated in cited Infoblox research with a portfolio operator that rotates nameservers and sells visitor traffic to malicious advertisers. |
| DOMAIN | magpiedns[.]com | Nameserver domain used during a one-week period for oldhamcounty.net and associated in cited Infoblox research with a portfolio operator that rotates nameservers and sells visitor traffic to malicious advertisers. |
People
Renée BurtonQuoted as Infoblox Threat Intel's VP describing the traffic distribution, cloaking, and malicious-advertising risks associated with the domain portfolio operator.Steve FreegardQuoted as Abusix Intelligence's Senior Product Owner discussing the group Abusix says has taken over dangling CNAMEs, including on a Connecticut state government website.
Vendors
AbusixAlmost all of the IP addresses tied to the typo domain amzonses.com are listed by reputable blocklist operators such as Spamhaus, URIBL, Abusix, and others.Infobloxpoints to koaladns.com, and newburgh.org still points to hastydns.com. All of these NS domains appear in Infoblox’s research on parking and abuse infrastructure, where they’re tied to a single portfolio operator that