
Researchers Analyze Trellix QakBot IoCs and Identify Malicious Artifacts
Summary
Researchers analyzed 125 domains and 19 subdomains from Trellix’s QakBot IoCs, using DNS, WHOIS and network data to identify malicious artifacts and related domains. They flagged one subdomain for malware distribution.
Key points
- Researchers extracted 929 domains from Trellix’s IoC list, filtered them to 492 and focused on 125; with 19 subdomains, the analysis covered 144 IoCs.
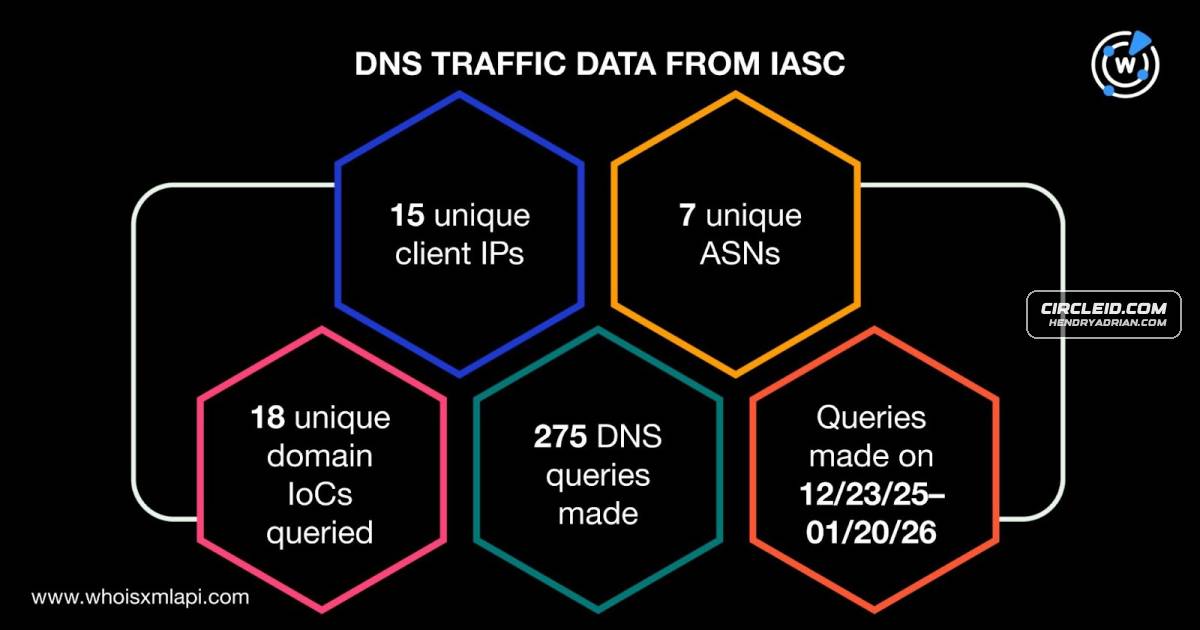
- Network telemetry showed 15 client IPs across seven ASNs made 275 DNS queries to 18 analyzed domains between 23 December 2025 and 20 January 2026.
- The researchers reported that eight analyzed domains were registered with malicious intent; they said many older domains may be legitimate sites compromised for attacks.
- Of 19 subdomains reviewed, 18 were assessed as benign; books[.]ttc[.]edu[.]sg was flagged for malware distribution and pointed to 200.69.23.93.
- WHOIS-history pivots found 360 unique email addresses, 105 of them public; analysis of connected domains identified 11,325 domains, nine of which threat-intelligence queries flagged as malicious.
- The analysis also identified 108 IP addresses, 60 assessed as malicious, plus 1,595 IP-connected domains and 1,404 string-connected domains, with one malicious domain in each set.
- The article offers a sample of additional artifacts and cautions that entities labeled malicious may later prove harmless, recommending further investigation.
Article Details
- Attack Vectors
- QakBot is described as commonly distributed through phishing emails.
- The article says QakBot harvests credentials, maintains command-and-control access, delivers additional payloads, and moves laterally.
- A malicious subdomain on a legitimate domain was identified as pointing to a malicious IP address.
- Defensive Notes
- Investigate the flagged subdomain books[.]ttc[.]edu[.]sg and the associated IP address 200[.]69[.]23[.]93.
- Use the reported malicious email-connected domains as hunting leads, and corroborate detections with further investigation; the article cautions that threat classifications may change with context.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | alltopposts[.]com | Email-connected domain flagged in threat-intelligence results for malware distribution. |
| DOMAIN | boogadelic[.]com | Email-connected domain flagged in threat-intelligence results for phishing. |
| DOMAIN | books[.]ttc[.]edu[.]sg | Subdomain flagged for malware distribution; the article says it points to 200[.]69[.]23[.]93. |
| DOMAIN | extremetowingservice[.]com | Email-connected domain flagged in threat-intelligence results for phishing. |
| DOMAIN | garagedoorrepairchicopeema[.]com | Email-connected domain flagged in threat-intelligence results for phishing. |
| IPV4 | 200[.]69[.]23[.]93 | IP address identified by the article as malicious and associated with the malware-distribution subdomain. |
MITRE ATT&CK
Malware
Tools
DNS Chronicle APIDNS Chronicle API queries for the 125 domains identified as IoCs revealed that they had 25,867 historical domain-to-IP resolutions since 5 February 2017.First Watch Malicious Domains Data FeedAccording to our First Watch Malicious Domains Data Feed query results, eight of the domains identified as IoCs were registered with malicious intent from the get-go.Jake AIWe first looked into the 19 subdomains identified as IoCs using Jake AI.Reverse WHOIS APIBased on the results of our Reverse WHOIS API queries for the 105 public email addresses, none of them were present in current WHOIS records.Threat Intelligence APIThreat Intelligence API queries for the 11,325 email-connected domains showed that nine have already been weaponized for various attacks.WHOIS History APIWe started our search for connected artifacts by querying the 125 domains identified as IoCs on WHOIS History API.WhoisXML API MCP ServerAided by the WhoisXML API MCP Server, we weeded out the legitimate domains, which may have been compromised for various attacks, from the domain list.