
Malicious Go Module Steals Passwords and Deploys Rekoobe Linux Backdoor
Summary
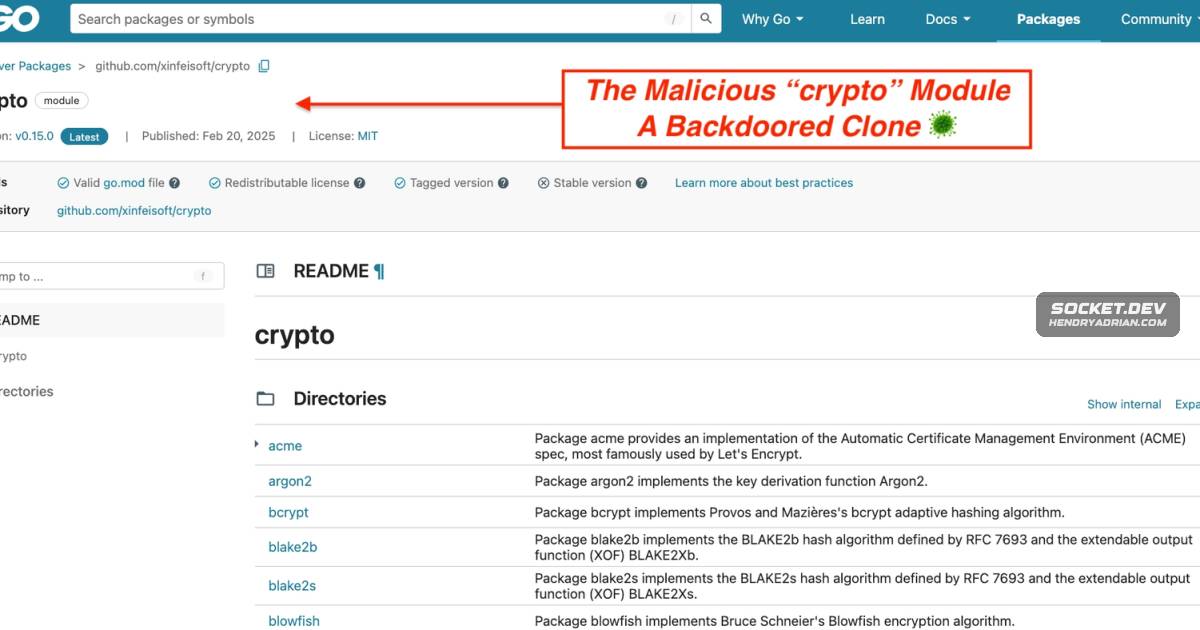
Socket researchers traced a backdoored Go module that captures ReadPassword input, fetches shell commands through a GitHub-hosted pointer, and deploys a Rekoobe Linux backdoor. The Go module proxy now blocks it after a report.
Key points
- The module github[.]com/xinfeisoft/crypto imitates golang.org/x/crypto and adds credential-stealing code to ssh/terminal.ReadPassword.
- Captured passwords are written locally and sent to an attacker-supplied endpoint; the backdoor then fetches and executes shell commands.
- The Linux stager adds an SSH key to authorized_keys, sets iptables policies to ACCEPT, and downloads two .mp5-disguised payloads from img[.]spoolsv[.]cc.
- Socket researchers identified sss.mp5 as a campaign stage and confirmed 555.mp5 as a Rekoobe Linux backdoor; observed communications included 154.84.63.184:443.
- The investigation describes GitHub Raw as a staging pointer that can redirect infected systems without republishing the module.
- After Socket reported the package, the Go security team blocked it through the public module proxy; the article says it remained listed on pkg.go.dev and accessible through public mirrors for a time.
Article Details
- Attack Vectors
- A malicious Go module, github.com/xinfeisoft/crypto, impersonated golang.org/x/crypto and backdoored ssh/terminal.ReadPassword to capture entered passwords.
- The backdoor wrote captured passwords to /usr/share/nano/.lock, sent them to an attacker-supplied endpoint, and fetched shell commands through a GitHub-hosted staging pointer.
- A downloaded shell stager added an SSH key to /home/ubuntu/.ssh/authorized_keys, changed iptables default policies to ACCEPT, and downloaded and executed two payloads disguised with .mp5 extensions.
- The article identifies sss.mp5 as a campaign stage or loader and 555.mp5 as a confirmed Rekoobe Linux backdoor.
- Defensive Notes
- Review go.mod and go.sum changes as security-sensitive and scrutinize suspicious dependencies that enable network access or shell execution.
- Monitor for writes to /usr/share/nano/.lock, GitHub Raw fetches followed by dynamic POST destinations, curl | sh execution, authorized_keys modifications, and iptables default-policy changes.
- The article reports that the public Go module proxy blocks the malicious module, but that it remained listed on pkg.go.dev and was accessible through public mirrors for a time.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | img[.]spoolsv[.]cc | Attacker-used host for staging and payload delivery. |
| DOMAIN | img[.]spoolsv[.]net | Historical attacker-used staging domain identified in the article. |
| IPV4 | 154[.]84[.]63[.]184 | Observed destination for repeated communications from the staged payloads over TCP 443. |
| SHA256 | 4afdb3f5914beb0ebe3b086db5a83cef1d3c3c4312d18eff672dd0f6be2146bc | SHA-256 hash reported for the staged sss.mp5 component. |
| SHA256 | 8b0ec8d0318347874e117f1aed1b619892a7547308e437a20e02090e5f3d2da6 | SHA-256 hash reported for the 555.mp5 Rekoobe Linux backdoor. |
| URL | hxxp[:]//img[.]spoolsv[.]cc/snn50.txt | Stager script downloaded by the delivery chain to prepare the host and deliver payloads. |
| URL | hxxps[:]//img[.]spoolsv[.]cc/555.mp5 | Specific payload-delivery URL for the 555.mp5 Rekoobe backdoor. |
| URL | hxxps[:]//img[.]spoolsv[.]cc/seed.php | Attacker-used staging endpoint identified as the next hop in the payload delivery chain. |
| URL | hxxps[:]//img[.]spoolsv[.]cc/sss.mp5 | Specific payload-delivery URL for the staged sss.mp5 component. |
| URL | hxxps[:]//img[.]spoolsv[.]net/seed.php | Historical staging endpoint that the article says was replaced by the .cc endpoint. |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/xinfeisoft/vue-element-admin/refs/heads/main/public/update[.]html | GitHub-hosted staging pointer fetched by the backdoor to obtain the next delivery endpoint. |
MITRE ATT&CK
T1036 · MasqueradingThe malicious module copied the structure and package layout of the legitimate Go cryptography repository to appear routine.T1036.008 · Masquerade File TypeThe Linux payloads used the .mp5 extension to disguise executable files as media.T1056 · Input CaptureThe backdoored ReadPassword function captured interactive password input before the application could process it.T1059.004 · Unix ShellThe backdoor executed retrieved shell content using /bin/sh.T1070.004 · File DeletionThe stager deleted the dropped payload files after executing them.T1071.001 · Web ProtocolsThe backdoor fetched a GitHub-hosted pointer and used HTTP POST to exfiltrate captured passwords.T1098.004 · SSH Authorized KeysThe stager appended an attacker SSH key to /home/ubuntu/.ssh/authorized_keys.T1102.001 · Dead Drop ResolverA GitHub Raw file acted as a staging pointer that supplied the next endpoint in the delivery chain.T1105 · Ingress Tool TransferThe shell stager used curl to download additional payloads from img.spoolsv[.]cc.T1195.002 · Compromise Software Supply ChainThe attacker published a lookalike Go module that impersonated golang.org/x/crypto and introduced backdoored code.T1204.005 · Malicious LibraryApplications importing the malicious library trigger its backdoor when they invoke the modified ReadPassword function.T1562.004 · Disable or Modify System FirewallThe stager set iptables INPUT and OUTPUT default policies to ACCEPT.T1656 · ImpersonationThe module impersonated the legitimate golang.org/x/crypto project and abused trust in its repository and mirror structure.