
StegaBin Uses 26 Typosquatted npm Packages to Target Developer Secrets
Summary
Socket analyzed 26 typosquatted npm packages that use Pastebin steganography and Vercel routing to install a RAT and nine data-stealing modules targeting developer secrets. The activity is consistent with FAMOUS CHOLLIMA, but attribution is not confirmed.
Key points
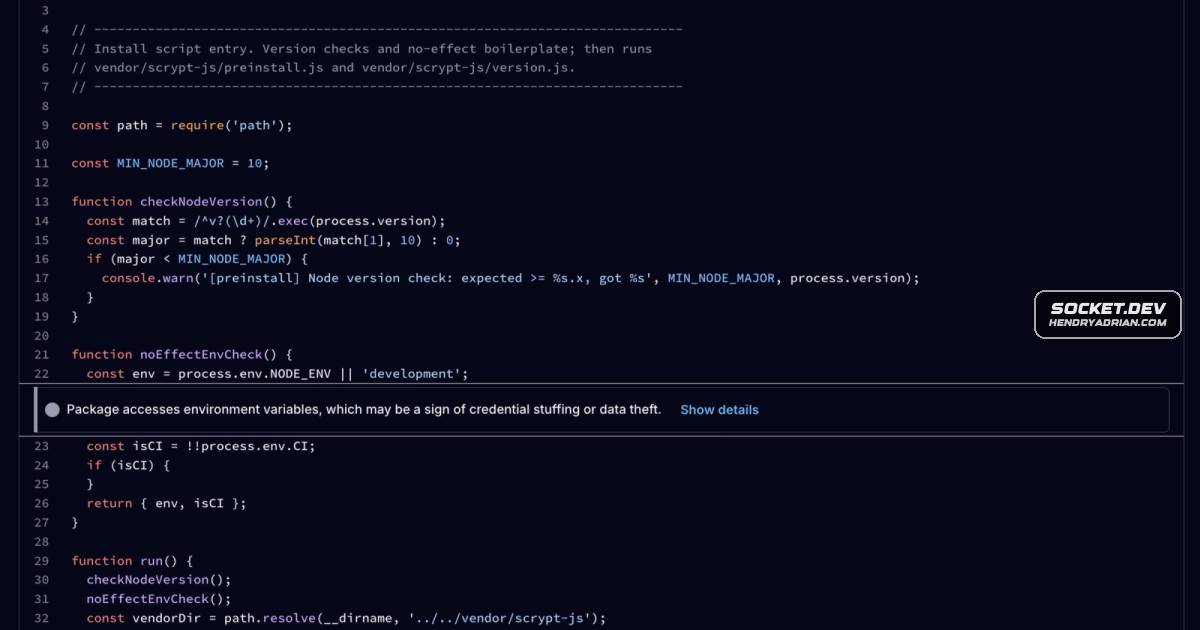
- The 26 packages, published February 25–26, 2026, typosquatted popular npm libraries and shared a malicious loader at vendor/scrypt-js/version.js.
- An npm install hook launches the loader, which decodes C2 domains hidden by character-level steganography in Pastebin essays and retrieves platform-specific shell payloads.
- The researchers decoded 31 Vercel-hosted C2 domains; only one was returning live payloads at the time of analysis.
- A simulated client connection let Socket capture the C2-delivered toolkit, whose nine modules target browser and wallet credentials, clipboard data, SSH keys, Git credentials, and developer secrets.
- A module writes a VSCode tasks.json configured to run hidden commands when a folder opens, enabling recurring execution across VSCode sessions.
- Socket says the TTPs, infrastructure patterns, and overlap with prior campaigns are consistent with FAMOUS CHOLLIMA / Contagious Interview; this is an attribution assessment, not confirmation.
Article Details
- Attack Vectors
- Typosquatted npm packages execute an install hook that loads a shared, obfuscated JavaScript payload.
- The loader decodes C2 domains concealed in Pastebin essays using character-level steganography, then retrieves platform-specific shell payloads from Vercel-hosted infrastructure.
- A token-gated bootstrapper downloads and runs a RAT that automatically deploys nine information-stealing modules.
- A malicious VSCode tasks.json uses hidden commands configured to run whenever a folder is opened, enabling reinfection during VSCode sessions.
- The modules collect developer secrets, browser and cryptocurrency-wallet data, clipboard and keystroke input, Git credentials, SSH files, and other local files, then send data to C2 or operator-supplied FTP infrastructure.
- Defensive Notes
- The article advises developers to review dependencies carefully and avoid blindly installing untrusted packages.
- Review VSCode User tasks.json files for concealed commands configured to run on folderOpen.
- Socket reports that its threat detection flagged the packages for obfuscated code and abnormal install-script behavior.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | atlasnode-app204[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | atlasnode-ext957[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | brightlaunch-app615[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | brightlaunch-ext742[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | cleverstack-app998[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | cleverstack-ext301[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | cloudharbor-app239[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | cloudharbor-ext664[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | ext-checkdin[.]vercel[.]app | Campaign C2 domain used to serve platform-specific payloads; it was the only one of the listed Vercel domains returning a live response during analysis. |
| DOMAIN | logicfield-app681[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | logicfield-ext432[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | primevector-app920[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | primevector-ext483[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | sparkforge-app790[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | sparkforge-ext518[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | zenithflow-app877[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| DOMAIN | zenithflow-ext156[.]vercel[.]app | Listed among the campaign's Vercel-hosted C2 domains decoded from Pastebin dead drops. |
| IPV4 | 103[.]106[.]67[.]63 | Campaign C2 IP used by the RAT and for data uploads; the article identifies ports 1244 and 1247 for the RAT and WebSocket control channels. |
| SHA256 | 1b15f73054350c6ab42f6e1d2ce4d84d7c56821db699e4ec484541263dfcb636 | SHA-256 of the campaign's obfuscated stealer module. |
| SHA256 | 4e6a7bf3964fc0e3a655f062330c76b4876dcfac47d213e4c1f0ec3fe6ef9e12 | SHA-256 of the TruffleHog secret-scanning module delivered by the campaign. |
| SHA256 | 714f890308d2cfebb2ed3ae873697408372639260bb682ea4cfbfffec98b8add | SHA-256 of the campaign's Python browser-stealer module. |
| SHA256 | 78c8b9044f6029280d28a1f62a4414a22e870fc27e3cc4894bd077d17f2ad8b4 | SHA-256 of the campaign's FTP-exfiltration RAT module. |
| SHA256 | 978e8f161da04e00117a695aa59452dce89b5247db93ab7cedcaea3c1f26b8c8 | SHA-256 of the campaign's Git repository and SSH theft module. |
| SHA256 | ba3e520b9727e893cf07b0c1a6e6ce1a62e8e9bf28b5c771af4fdf01f9bd9ed4 | SHA-256 of the campaign's crypto and exfiltration module. |
| SHA256 | ce80100a383730822221f3ce769ea5ccda0c583654cc7c119ecc50bfbb4203b9 | SHA-256 of the campaign's keylogger and clipboard-stealing module. |
| SHA256 | da1775d0fbe99fbc35b6f0b4a3a3cb84da3ca1b2c1bbac0842317f6f804e30a4 | SHA-256 of the malicious loader found in the npm packages and redeployed as a persistence module. |
| SHA256 | ddbb527be0f40cd13eab08e3e418e36e86e4f1f1458cf84cfee29490beacf3a6 | SHA-256 of the campaign's VSCode persistence module. |
| URL | hxxps[:]//pastebin[.]com/0ec7i68M | Pastebin dead-drop URL containing text used to conceal campaign C2 domains. |
| URL | hxxps[:]//pastebin[.]com/CJ5PrtNk | Pastebin dead-drop URL containing text used to conceal campaign C2 domains. |
| URL | hxxps[:]//pastebin[.]com/DjDCxcsT | Pastebin dead-drop URL containing text used to conceal campaign C2 domains. |
MITRE ATT&CK
T1005 · Data from Local SystemModules search local filesystems for developer secrets, credentials, SSH files, Git data, and other sensitive files for collection.T1027.003 · SteganographyThe loader extracts C2 domains from Pastebin essays using evenly spaced character positions and character substitutions.T1036.005 · Match Legitimate Resource Name or LocationTyposquat package names and the loader path vendor/scrypt-js/version.js were chosen to resemble legitimate packages or files.T1041 · Exfiltration Over C2 ChannelCollected clipboard data and files are uploaded to C2 endpoints, including /clipup and /uploads.T1056.001 · KeyloggingThe keylogger captures keyboard input using Windows low-level hooks, Linux X input events, and macOS CGEventTap.T1059 · Command and Scripting InterpreterThe npm install hook runs a Node.js script, and downloaded platform payloads execute shell commands or Windows commands.T1071.001 · Web ProtocolsThe RAT and modules communicate with C2 and upload data over HTTP; an interactive module also uses a WebSocket control channel.T1083 · File and Directory DiscoveryModules recursively scan directories and drives to locate Git repositories, SSH files, and files matching secret and credential patterns.T1105 · Ingress Tool TransferThe loader retrieves platform-specific shell payloads and the bootstrapper downloads parser.js and additional modules from campaign infrastructure.T1115 · Clipboard DataA module polls clipboard contents and uploads captured clipboard data to the campaign's C2.T1195.001 · Compromise Software Dependencies and Development ToolsThe campaign distributed malicious typosquat npm packages that ran an install hook and declared the legitimate package they impersonated as a dependency.T1547 · Boot or Logon Autostart ExecutionThe malware writes a VSCode tasks.json configured to run concealed commands whenever a folder is opened, causing reinfection during VSCode sessions.T1555.003 · Credentials from Web BrowsersThe stealer targets browser-stored credentials, cookies, and browser extension data, including cryptocurrency wallet extension stores.T1562.001 · Disable or Modify ToolsThe interactive RAT includes a command to kill security-related processes on the compromised machine.
People
Threat Actors
Lazarus GroupThe article describes Lazarus Group as closely associated with FAMOUS CHOLLIMA and links the campaign to Lazarus-associated Contagious Interview operations; the specific campaign attribution is presented as consistent with, not confirmed as, that activity.Void DokkaebiThe article assesses that the campaign's infrastructure and tradecraft are consistent with activity attributed to this North Korean-aligned cluster; it does not present the attribution as confirmed.
Vendors
Pastebincoordinated typosquatting npm campaign dubbed “StegaBin” that published 26 malicious packages which use Pastebin-based character-level steganography to hide Vercel C2 infrastructure and deliver a multi-stage installerReliableSite.Net LLCto 103[.]106[.]67[.]63:1247) (‘parser.js … connects to 103[.]106[.]67[.]63:1244, hosted on ReliableSite.Net LLC …’).Vercelthat published 26 malicious packages which use Pastebin-based character-level steganography to hide Vercel C2 infrastructure and deliver a multi-stage installer that ultimately deploys a RAT and a nine-module
Products
npmSocket detected a coordinated typosquatting npm campaign dubbed “StegaBin” that published 26 malicious packages which use Pastebin-based character-level steganography to hide Vercel C2 infrastructure and deliver aVSCodeThe deployed RAT automatically fetches and installs nine infostealer modules that target VSCode persistence, keylogging/clipboard capture, browser and crypto wallet secrets, TruffleHog scanning, Git/SSH theft, FTP