
DNS Analysis Links Q4 2025 Malware IoCs to 359 Domains
Summary
An analysis of 46 IoCs tied to seven malware families reported 145 client IPs contacting eight IoC domains and 359 email-connected domains, 25 of which threat-intelligence checks found had been weaponized.
Key points
- The analysis examined 46 IoCs associated with SocGholish, CoinMiner, Agent Tesla, Calendaromatic, ZPHP, VenomRAT, and ACR Stealer.
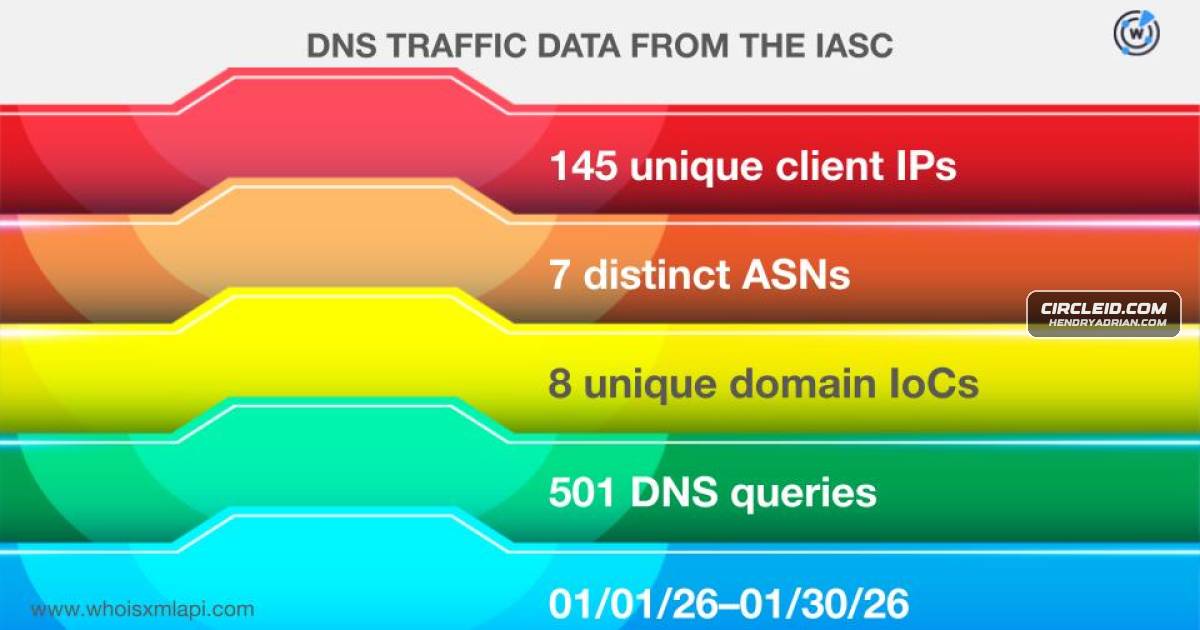
- Network data showed 145 client IPs made 501 DNS queries to eight IoC domains between January 1 and 30, 2026.
- Historical WHOIS records linked 32 IoC domains to 43 email addresses; reverse WHOIS queries identified 359 email-connected domains.
- Threat-intelligence checks found 25 of the 359 email-connected domains had been used for malicious activity.
- Of 29 IP addresses associated with the analyzed domains, 19 had previously appeared in malicious campaigns, according to the analysis.
- The researchers reported akilay[.]kingx[.]info as a confirmed malicious subdomain; 11 of the 14 checked subdomains were unresponsive.
Article Details
- Attack Vectors
- SocGholish and ZPHP JavaScript downloaders were described as distributed through malicious or compromised sites disguised as fake browser updates.
- Calendaromatic was described as a backdoor disguised as a legitimate calendar download and spread through malvertisements and SEO poisoning.
- VenomRAT was described as spread through malspam or dropped by other malware.
- CoinMiner was described as typically using WMI to spread across networks.
- The article says social-engineering lures, including fake browser updates and calendar-download disguises, entice users to execute payloads.
- Defensive Notes
- The article recommends supplementary investigation to corroborate entities identified as threats, noting that some may later be deemed harmless or their context may change.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 1sou[.]top | Email-connected domain identified as used for malware distribution. |
| DOMAIN | akilay[.]kingx[.]info | Subdomain confirmed malicious by the analysis. |
| DOMAIN | apposx[.]com | Listed as an ACR Stealer domain IoC in the analysis. |
| DOMAIN | as5yo[.]top | Email-connected domain identified as used for malware distribution. |
| DOMAIN | chinapark[.]top | Email-connected domain identified as used for malware distribution. |
| DOMAIN | downloadfreak[.]top | Email-connected domain identified as used for malware distribution. |
| DOMAIN | gcsho[.]com | Listed as an Agent Tesla domain IoC in the analysis. |
| DOMAIN | haidao10[.]top | Email-connected domain identified as used for malware distribution. |
| DOMAIN | ijels[.]com | Listed as a ZPHP domain IoC in the analysis. |
| DOMAIN | karbowanec[.]com | Listed as a CoinMiner domain IoC in the analysis. |
| DOMAIN | kingx[.]info | Listed as an Agent Tesla domain IoC and reported as likely to have turned malicious 517 days before the CIS report. |
| DOMAIN | krestinaful[.]com | Listed as a Calendaromatic domain IoC in the analysis. |
| DOMAIN | ovementxview[.]com | Listed as a Calendaromatic domain IoC and reported as likely to have turned malicious 138 days before the CIS report. |
| DOMAIN | paquetesparaorlando[.]com | Listed as a SocGholish domain IoC in the analysis. |
| DOMAIN | sou[.]top | Named in the article as an email-connected domain confirmed weaponized. |
| DOMAIN | theriygrt[.]com | Listed as a VenomRAT domain IoC in the analysis. |
| DOMAIN | umnsrx[.]net | Listed as a CoinMiner domain IoC and reported as likely to have turned malicious 127 days before the CIS report. |
MITRE ATT&CK
T1047 · Windows Management InstrumentationThe article says CoinMiner typically uses WMI to spread across networks.T1189 · Drive-by CompromiseThe article describes JavaScript downloaders delivered through malicious or compromised sites as fake browser updates.T1204.002 · Malicious FileThe article describes fake browser updates and disguised calendar downloads as lures that prompt users to execute payloads.T1566 · PhishingThe article says VenomRAT may be spread through malspam.
Threat Actors
Malware
ACR (AcridRain) StealerCIS ranked the top 10 malware of Q4 2025 and seven of those (SocGholish, CoinMiner, Agent Tesla, Calendaromatic, ZPHP, VenomRAT, ACR Stealer) had network IoCs identified and analyzed.Agent TeslaCIS ranked the top 10 malware of Q4 2025 and seven of those (SocGholish, CoinMiner, Agent Tesla, Calendaromatic, ZPHP, VenomRAT, ACR Stealer) had network IoCs identified and analyzed.CalendaromaticCIS ranked the top 10 malware of Q4 2025 and seven of those (SocGholish, CoinMiner, Agent Tesla, Calendaromatic, ZPHP, VenomRAT, ACR Stealer) had network IoCs identified and analyzed.CoinMinerCIS ranked the top 10 malware of Q4 2025 and seven of those (SocGholish, CoinMiner, Agent Tesla, Calendaromatic, ZPHP, VenomRAT, ACR Stealer) had network IoCs identified and analyzed.SocGholish#SocGholish #AgentTeslaVenomRATCIS ranked the top 10 malware of Q4 2025 and seven of those (SocGholish, CoinMiner, Agent Tesla, Calendaromatic, ZPHP, VenomRAT, ACR Stealer) had network IoCs identified and analyzed.ZPHPCIS ranked the top 10 malware of Q4 2025 and seven of those (SocGholish, CoinMiner, Agent Tesla, Calendaromatic, ZPHP, VenomRAT, ACR Stealer) had network IoCs identified and analyzed.
Tools
First Watch Malicious Domains Data FeedThe results of our First Watch Malicious Domains Data Feed queries also revealed that seven domains classified as IoCs were deemed likely to turn malicious 20—517 days before they were reported as such on 29 JanuaryIASCSample network traffic data from the IASC revealed that 145 unique client IP addresses under seven distinct ASNs communicated with eight of the domains tagged as IoCs via 501 DNS queries between 1 and 30 January 2026.Jake AIWe gathered more information on the 14 subdomains identified as IoCs using Jake AI.WhoisXML API MCP ServerNote that we excluded domains originally identified as IoCs that were owned by legitimate entities from our list for further analysis aided by the WhoisXML API MCP Server.