
Phishing Emails Impersonate LastPass Support to Steal Vault Passwords
Summary
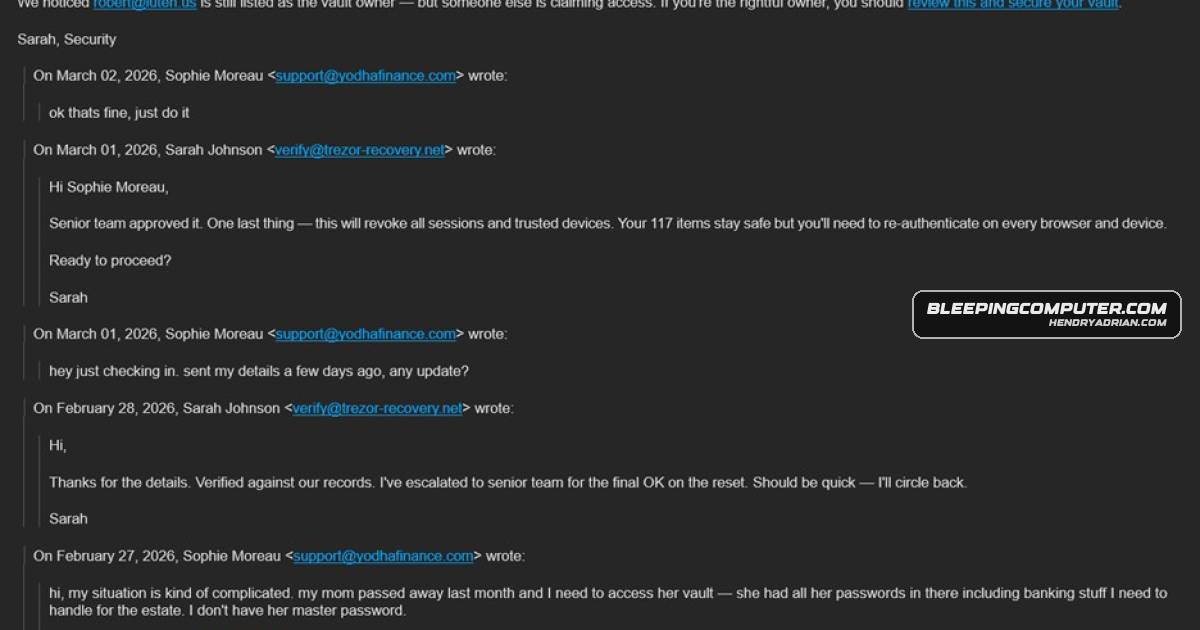
LastPass warns that phishing emails spoof its support team and use fake forwarded threads to lure users to credential-stealing pages. The company says its systems were not compromised and is working to take down the sites.
Key points
- Emails spoof the “LastPass Support” display name and mimic forwarded internal conversations to create urgency.
- Links labeled with account-protection actions lead to a fake login page at verify-lastpass[.]com or redirecting lookalike URLs that collect credentials.
- The campaign uses multiple sender addresses and subject lines; some sender addresses are tied to compromised websites or abandoned domains.
- LastPass says its infrastructure was not compromised and there was no impact on its systems.
- LastPass says support agents will never ask users for their master password and is working with partners to take down the fake sites.
Article Details
- Event Type
- Phishing campaign impersonating LastPass Support
- Impact
- The campaign directs LastPass users to credential-stealing pages. LastPass says its infrastructure was not compromised and there was no impact on its systems.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | verify-lastpass[.]com | Domain hosting a fake LastPass login page used to harvest user credentials. |