
Default ForgeRock Password Let Researchers Access Two Automakers’ Accounts and Control Test Cars
Summary
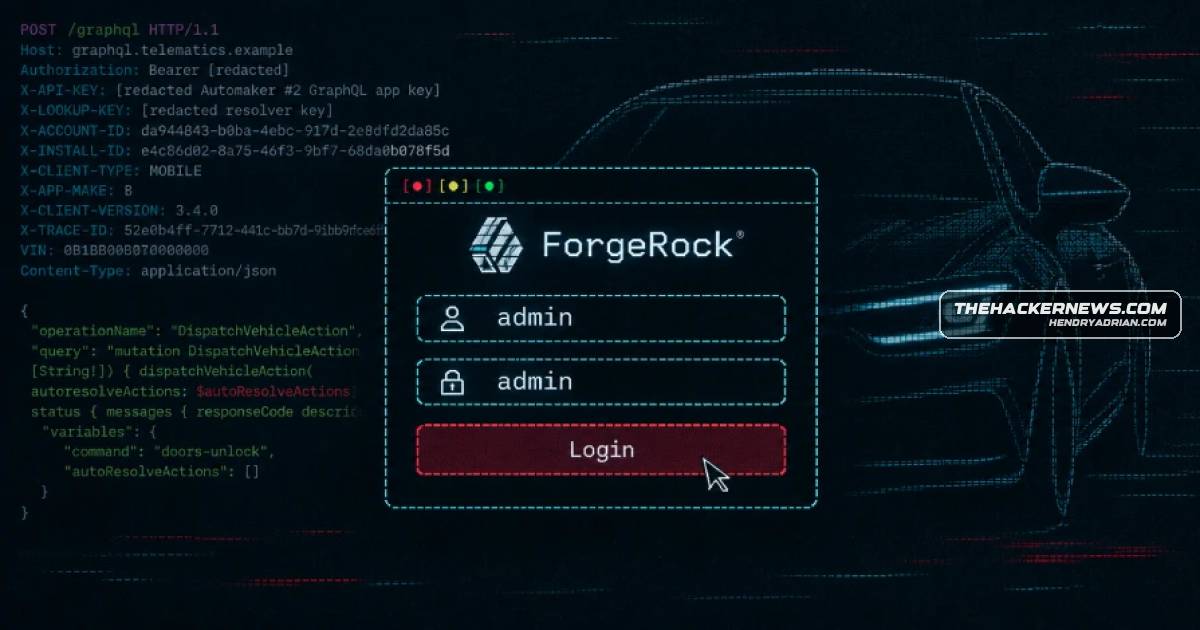
Researchers say a path-parsing flaw and default ForgeRock admin credentials let them access customer accounts at two automakers and unlock and start authorized test cars. The U.S. systems were fixed about two hours after disclosure.
Key points
- The researchers found an exposed OpenIDM administrator console protected by the default admin:admin credentials.
- Encoded slashes and extra characters made an edge system and the Java server interpret the same request path differently, exposing the console.
- They used its scheduler to run code on the identity server, change a test account’s credentials, and obtain the app’s access tokens.
- Using those tokens, they unlocked and started a test car with its owner present, then locked it and stopped the engine.
- They said they tested vehicle commands only on cars they owned or had permission to use; the U.S. systems were fixed about two hours after they reported the issue.
- A separate attack on the brands’ Australian systems used admin credentials left in app code; the article gives no fix date for those systems.
- The researchers said the combined attacks could send commands to the brands’ cars in Australia, the United States, and Canada. They reported no evidence about whether others had used the paths.
Article Details
- Attack Vectors
- Researchers bypassed an edge filter’s path handling by adding encoded slashes and extra characters, reaching a blocked OpenIDM administrator console.
- The administrator console still accepted its documented default credentials, admin:admin.
- A built-in scheduler ran scripts that executed code on the identity server, which held customer records.
- Researchers changed a target account’s email address and password, then signed in through the normal app and received that account’s access tokens.
- For the Australian systems, Shubham Shah reported that administrator credentials had been left in the app’s code for a test setup.
- Using the affected accounts’ vehicle commands, researchers unlocked doors and started a test car’s engine.
- Defensive Notes
- ForgeRock’s production hardening guidance says to remove the OpenIDM administrator console or protect it before deployment.
- The console’s separately stored password should not be left at its documented default.
MITRE ATT&CK
T1059 · Command and Scripting InterpreterResearchers used the built-in scheduler to run scripts that executed code on the identity server.T1078 · Valid AccountsThe console accepted the documented default administrator username and password, admin:admin.T1098 · Account ManipulationAfter reaching customer records, researchers changed a target account’s email address and password.T1190 · Exploit Public-Facing ApplicationResearchers bypassed edge path handling to reach the identity servers’ administrator console.
People
Vendors
Products
Apache FelixOpenIDM comes with a built-in administrator console powered by the Apache Felix tool. ForgeRock's own hardening guide tells operators to remove this console or protect it before going live because it stores its ownForgeRockBoth apps signed customers in through ForgeRock, an identity platform now part of Ping Identity, and on those servers the researchers reached an administrator console that still used its default password.OpenIDMsigned customers in through the same platform, which runs in two parts: one for login and one, called OpenIDM, that holds customer records.PingIDMFor teams running the same identity software, now sold as PingIDM, two checks matter:
Countries
Australiafor the identity server had been left in the app's code, intended for a test setup. He set out the full Australia chain in a separate post.Canadathey could send unlock and engine-start commands to the brands' cars in Australia, the United States, and Canada. That second post does not give a date for when the Australian systems were fixed.United StatesThey tested the full attack only on their own and consenting owners' cars in the United States, in February 2026, and both systems were fixed about two hours after they reported the problem.