
Researchers Report Qatar-Targeting PlugX and Cobalt Strike Campaigns
Summary
Researchers report a PlugX campaign attributed to Camaro Dragon targeting Qatar after regional escalations, plus a separate likely Qatar-focused Rust-loader campaign delivering Cobalt Strike; attribution of the latter to China-aligned actors is low confidence.
Key points
- Researchers report increased Chinese-nexus APT activity targeting Qatar after regional escalations.
- Camaro Dragon reportedly deployed a PlugX variant one day after Operation Epic Fury began, using lures about attacks on U.S. bases in Bahrain.
- The PlugX infection chain starts with a ZIP archive containing a malicious LNK, which downloads a payload and uses DLL hijacking of a legitimate Baidu NetDisk binary.
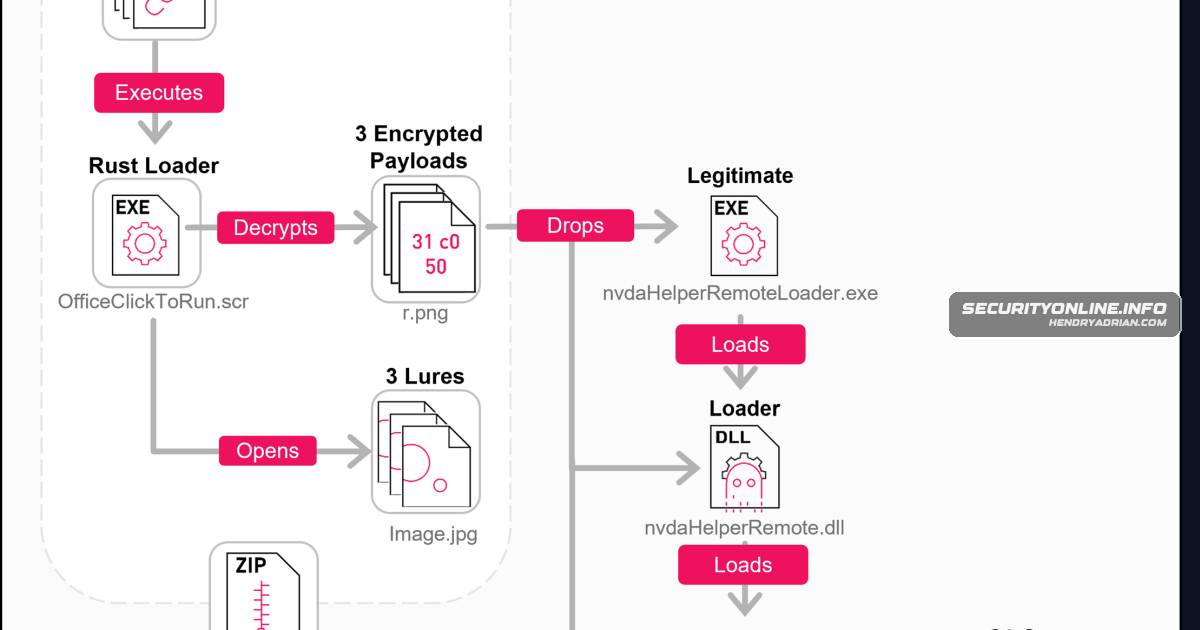
- A separate campaign, likely targeting Qatar, used lures about strikes on Gulf oil and gas facilities and a Rust-based loader that hijacks nvdaHelperRemote.dll to deliver Cobalt Strike.
- Attribution of the second campaign to China-aligned actors is assessed with low confidence; the article cites its TTPs and C2 infrastructure as resembling Chinese-nexus activity.
Article Details
- Event Type
- Reported cyber campaigns targeting Qatar amid regional escalations
- Impact
- Researchers reported that Camaro Dragon deployed a PlugX variant against Qatari targets, while a separate campaign likely targeting Qatar used a Rust-based loader to deliver Cobalt Strike. PlugX can support file exfiltration, screen capture, and remote command execution, but the article does not report confirmed data theft or other specific victim impact.
MITRE ATT&CK
T1105 · Ingress Tool TransferThe PlugX infection chain used a malicious LNK file to contact a compromised server and download a next-stage payload.T1574.001 · DLLThe reported campaigns used DLL hijacking, including abuse of a Baidu NetDisk binary to deploy PlugX and a Rust-based loader exploiting nvdaHelperRemote.dll.
Threat Actors
Malware
Products
Tools
Countries
BahrainBy using lures disguised as “photos of attacks on American bases in Bahrain,” the attackers created highly engaging content designed to blend into fast-moving regional communications.ChinaTTPs and C2 infrastructure indicate China-aligned patterns and a broader, sustained focus on Middle East targets.QatarResearchers have observed a sharp increase in Chinese-nexus APT operations rapidly pivoting to exploit regional instability, with a clear near-immediate focus on Qatar following recent escalations.