
KadNap Botnet Infects 14,000 Edge Devices, Including ASUS Routers
Summary
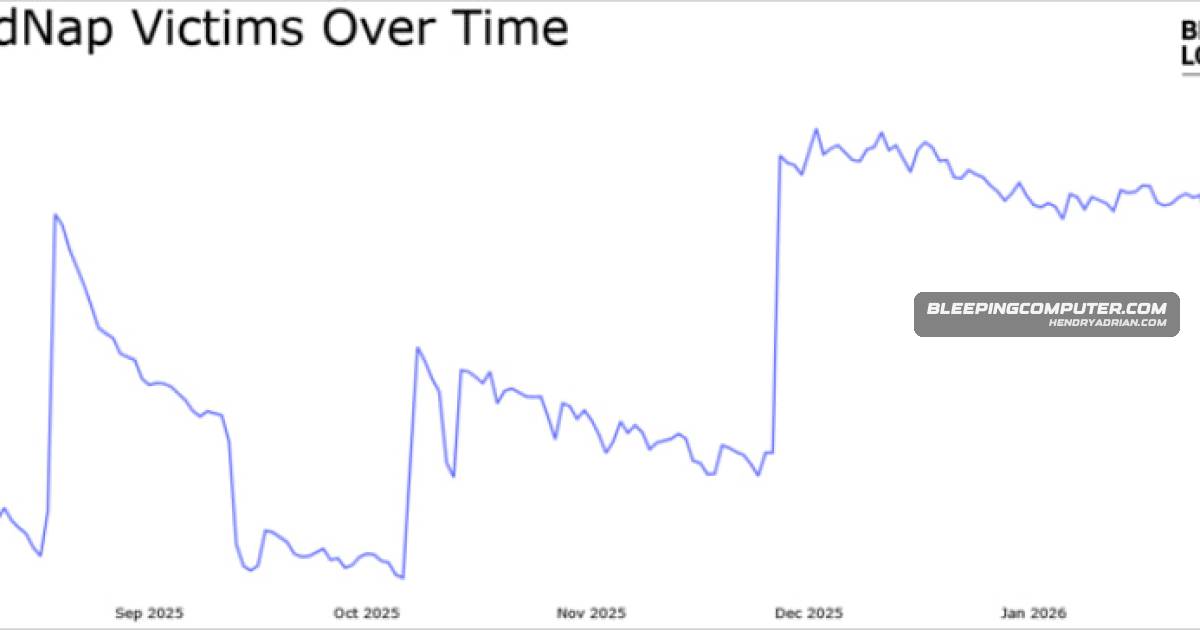
Researchers report that KadNap has infected about 14,000 edge devices, including ASUS routers, using a modified Kademlia DHT for C2. They link it to the Doppelganger proxy service; Lumen says it blocked related traffic on its network.
Key points
- Black Lotus Labs reports that KadNap has grown to about 14,000 infected devices since August 2025.
- Infections begin with aic.sh downloaded from 212.104.141[.]140; it installs an ELF binary named kad and a cron job that runs every 55 minutes.
- KadNap uses a modified Kademlia DHT to locate peers and C2 infrastructure, but connections to two consistent nodes can help researchers identify that infrastructure.
- About 60% of infected devices are in the United States, and nearly half of the network is connected to C2 infrastructure dedicated to ASUS-based bots.
- Researchers link KadNap to the Doppelganger proxy service, which they say is believed to be a rebrand of Faceless and sells access to infected devices.
- Lumen says it blocked traffic to and from the control infrastructure on its own network and planned to release indicators of compromise.
Article Details
- Event Type
- Botnet infection and proxy-network operation
- Impact
- KadNap has reportedly infected about 14,000 ASUS routers and other edge devices since August 2025. The devices are used as proxies for malicious traffic, and the botnet uses a modified Kademlia-based peer-to-peer network to conceal its command-and-control infrastructure. Black Lotus Labs reports that Lumen blocked traffic to or from the control infrastructure on its own network; the disruption does not extend to other networks.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 212[.]104[.]141[.]140 | Source of the malicious aic.sh script used to begin KadNap infections. |
MITRE ATT&CK
T1053.003 · CronKadNap establishes persistence with a cron job that runs every 55 minutes.T1090 · ProxyInfected devices are sold as residential proxies for funneling malicious traffic and evading blocklists.T1105 · Ingress Tool TransferThe infection begins by downloading the malicious aic.sh script from the listed IP address.T1110.004 · Credential StuffingThe article says proxy services such as Doppelganger are typically used for credential-stuffing attacks.T1498 · Network Denial of ServiceThe article says proxy services such as Doppelganger are typically used to launch DDoS attacks.
Malware
KadNapKadNap is a newly discovered botnet that has infected roughly 14,000 ASUS routers and other edge devices, forming a peer-to-peer network that uses a custom Kademlia-based DHT to hide its command-and-controlTheMoonproxy service, believed to be a rebrand of the Faceless service, previously associated with the TheMoon malware botnet, which also targeted ASUS routers.
Vendors
AsusKadNap is a newly discovered botnet that has infected roughly 14,000 ASUS routers and other edge devices, forming a peer-to-peer network that uses a custom Kademlia-based DHT to hide its command-and-controlLumen TechnologiesAccording to researchers at Black Lotus Labs, the threat research and operations arm of Lumen Technologies, nearly half of the KadNap network is connected to C2 infrastructure dedicated to ASUS-based bots, and the rest
Products
Countries
Hong KongMost infected devices are located in the United States, which accounts for 60% of the total, followed by significant percentages in Taiwan, Hong Kong, and Russia.RussiaMost infected devices are located in the United States, which accounts for 60% of the total, followed by significant percentages in Taiwan, Hong Kong, and Russia.TaiwanMost infected devices are located in the United States, which accounts for 60% of the total, followed by significant percentages in Taiwan, Hong Kong, and Russia.United StatesLotus Labs link KadNap to the Doppelganger proxy service, note heavy infection concentration in the United States, and report that Lumen has blocked traffic to the botnet’s control infrastructure on its network.