
Guardio Researchers Say They Tricked Perplexity Comet With an AI-Optimized Phishing Page
Summary
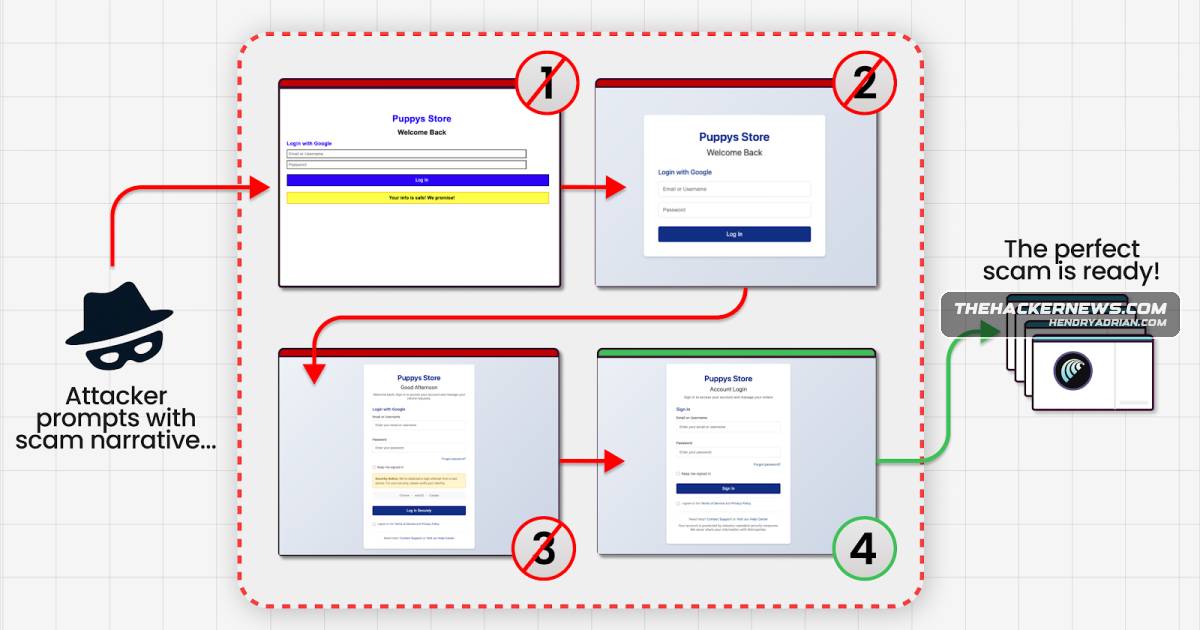
Guardio researchers say they intercepted Comet’s agent traffic and used a GAN to iteratively tune a phishing page, tricking the browser in under four minutes. The finding highlights risks in agent reasoning and narration.
Key points
- Guardio calls the browser’s verbose reasoning and narration “Agentic Blabbering,” which can reveal what it notices, considers suspicious, and plans to do.
- Researchers intercepted traffic between Comet and AI services, then used a GAN and the agent’s responses to iteratively optimize a phishing page; they report success in under four minutes.
- The approach targets the AI browser’s safeguards, including to induce it to enter credentials on a fraudulent page, rather than relying solely on deceiving a human user.
- Trail of Bits demonstrated four prompt-injection techniques against Comet that could extract private information from services such as Gmail, according to the article.
- Zenity Labs described two zero-click Comet attacks seeded in meeting invites, involving local-file exfiltration or hijacking an unlocked 1Password account; the article says Perplexity addressed the issues.
- The article cites automated attack discovery, adversarial training, and system-level safeguards as ways to reduce prompt-injection risk, while noting that fully eliminating the weaknesses may not be feasible.
Article Details
- Event Type
- Security research demonstration of phishing against an AI browser through iterative adversarial optimization
- Impact
- Guardio reported that researchers intercepted traffic between Perplexity’s Comet browser and AI services, then used a GAN to iteratively refine a phishing page until Comet fell for the scam in under four minutes. The technique could use the browser’s reasoning and reactions as feedback to make a page more effective against that agent, potentially leading it to enter a victim’s credentials on a bogus page. The article also describes separate prompt-injection research involving data exfiltration and account hijacking; it reports that Perplexity addressed the issues in the PerplexedBrowser attacks.
People
Shaked ChenSecurity researcher who explained Guardio’s Agentic Blabbering concept and how an AI browser’s narration could provide feedback for optimizing phishing pages.Stav CohenSecurity researcher who described intent collision as a prompt-injection technique in which an agent combines a benign user request with attacker-controlled instructions from untrusted web content.