
Stryker Confirms Global Microsoft Disruption as Handala Claims Device Wipes
Summary
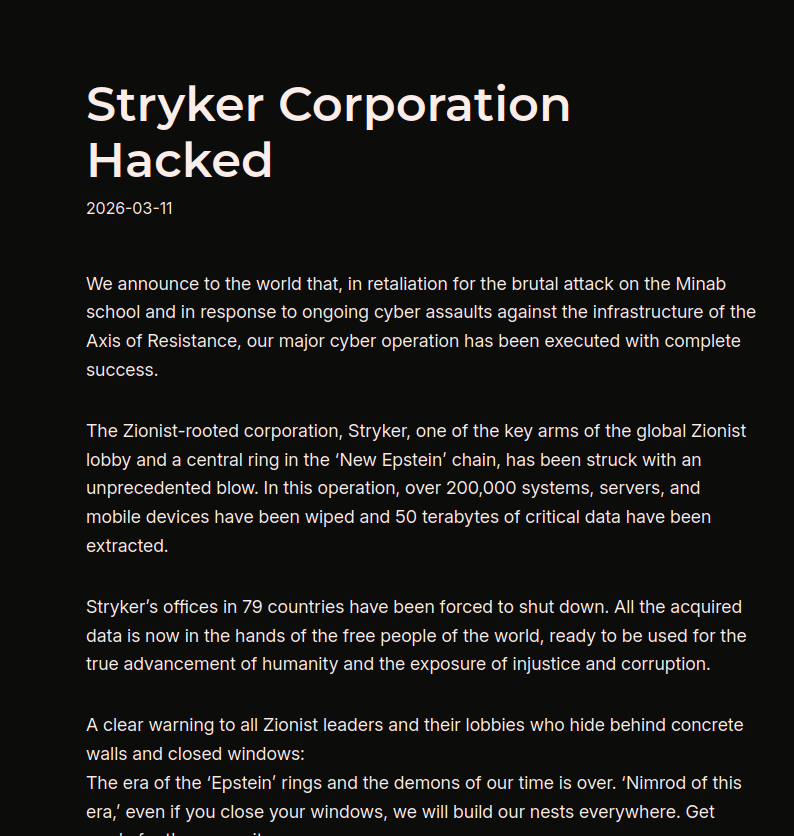
Stryker confirmed a global disruption to its Microsoft environment. Employees reported managed devices wiped, while Handala claimed responsibility and said it wiped over 200,000 systems and stole 50 TB; those claims are not independently confirmed.
Key points
- Stryker confirmed a global disruption to its Microsoft environment and said it had no indication of malware or ransomware.
- Employees in several countries reported that managed Windows devices and mobile phones had been remotely wiped.
- Handala claimed it wiped more than 200,000 systems and exfiltrated 50 TB; the article provides no independent confirmation of those figures.
- The article says the attack appears to have involved admin-level access to Microsoft Intune, which can remotely manage enrolled devices.
- Stryker said the disruption was contained to its internal Microsoft environment and that it was working to restore systems and electronic ordering.
- Threat intelligence firms link the Handala persona to Void Manticore and Iran’s Ministry of Intelligence and Security; these are attributed assessments.
Article Details
- Victim Organization
- Stryker Corporation
- Incident Type
- Destructive cyberattack involving abuse of Microsoft Intune to remotely wipe managed devices
- Affected Records
- Handala claimed more than 200,000 systems, servers, and mobile devices were wiped. This is a claimed device count, not a confirmed number of affected records.
- Affected Data Size
- Handala claimed that 50 terabytes of data were exfiltrated; this was not confirmed in the article.
- Operational Impact
- Stryker confirmed a global disruption to its Microsoft environment. Employees reported managed devices being wiped, and the article says operations across 79 countries were affected, disrupting ordering, device management, and communications. Stryker said it was working on restoration and believed the incident was contained to its internal Microsoft environment.
- Ransom Or Extortion
- No ransomware or ransom demand was reported. The incident was described as destructive rather than extortion-based; Handala claimed data exfiltration.
- Claim Status
- confirmed
MITRE ATT&CK
T1053.005 · Scheduled TaskThe article describes scheduled-task use in Void Manticore's attack playbook, not specifically in the Stryker incident.T1059.001 · PowerShellThe article describes PowerShell use in Void Manticore's attack playbook, not specifically in the Stryker incident.T1566 · PhishingThe article says Handala used phishing lures impersonating F5 software updates and Israel’s National Cyber Directorate in previous campaigns.
Threat Actors
HamsaThe article identifies Hamsa as another name for Handala. It also says Cyble observed use of a Hamsa data wiper in previous campaigns.HandalaThe article attributes the Stryker attack to Handala, which claimed to wipe more than 200,000 systems and exfiltrate 50 terabytes of data. The article says threat intelligence links the Handala persona to Void Manticore; the scale of the claimed impact and exfiltration is not independently confirmed in the article.Handala Hack TeamThe article identifies Handala Hack Team as another name for Handala, which it attributes with the Stryker attack.HatefThe article identifies Hatef as another name for Handala. It also says Cyble observed use of a Hatef data wiper in previous campaigns.MuddyWaterThe article describes MuddyWater as a MOIS-affiliated group and reports that Check Point Research found repeated overlaps and shared criminal tooling between it and Void Manticore.Void ManticoreThreat intelligence firms cited in the article assess Handala as one of the online personas maintained by Void Manticore, described as a MOIS-affiliated actor involved in system intrusions and hack-and-leak activity.
Malware
HamsaHandala — also known as Handala Hack Team, Hatef, and Hamsa — first surfaced in December 2023 as a hacktivist operation linked to Iran’s Ministry of Intelligence and Security (MOIS), initially targeting IsraeliHatefHandala — also known as Handala Hack Team, Hatef, and Hamsa — first surfaced in December 2023 as a hacktivist operation linked to Iran’s Ministry of Intelligence and Security (MOIS), initially targeting IsraeliRhadamanthysHandala has used Rhadamanthys, a commercial infostealer sold on dark web forums, pairing it with custom data wipers in phishing lures that impersonated F5 software updates and even Israel’s own National Cyber
Vendors
Products
EntraTheir Entra login page was defaced with the Handala logo,” a Reddit user said.Microsoft IntuneThe attack leveraged admin access to Microsoft Intune, causing outages across 79 countries, alleged exfiltration of 50 TB and claims of over 200,000 wiped endpoints, and has been attributed to Handala/Void Manticore
Tools
Countries
AustraliaEmployees in the United States, Ireland, Costa Rica, and Australia reported that managed Windows laptops and mobile devices had been remotely wiped.Costa RicaEmployees in the United States, Ireland, Costa Rica, and Australia reported that managed Windows laptops and mobile devices had been remotely wiped.IranTB and claims of over 200,000 wiped endpoints, and has been attributed to Handala/Void Manticore linked to Iran’s MOIS.IrelandEmployees in the United States, Ireland, Costa Rica, and Australia reported that managed Windows laptops and mobile devices had been remotely wiped.Israelpairing it with custom data wipers in phishing lures that impersonated F5 software updates and even Israel’s own National Cyber Directorate.United Statesglobally — ranks as one of the most operationally destructive cyberattacks ever executed against a U.S.