
Researchers Link Suspected AI-Assisted Slopoly Backdoor to Hive0163 Attack
Summary
IBM X-Force reported that Hive0163 used suspected AI-assisted PowerShell backdoor Slopoly to maintain access during a 2026 ransomware attack. Slopoly creates a scheduled task, beacons system information and polls its C2 for commands.
Key points
- Researchers observed Slopoly deployed during post-exploitation in a Hive0163 ransomware attack in early 2026, maintaining access to a compromised server for more than a week.
- The PowerShell backdoor establishes persistence through a scheduled task named “Runtime Broker.”
- Slopoly sends system information to a C2 every 30 seconds and polls for commands every 50 seconds; the commands used in the incident are unknown.
- Extensive comments, logging, error handling and descriptive variable names suggest LLM assistance, but researchers said the script lacks advanced techniques and is not truly polymorphic.
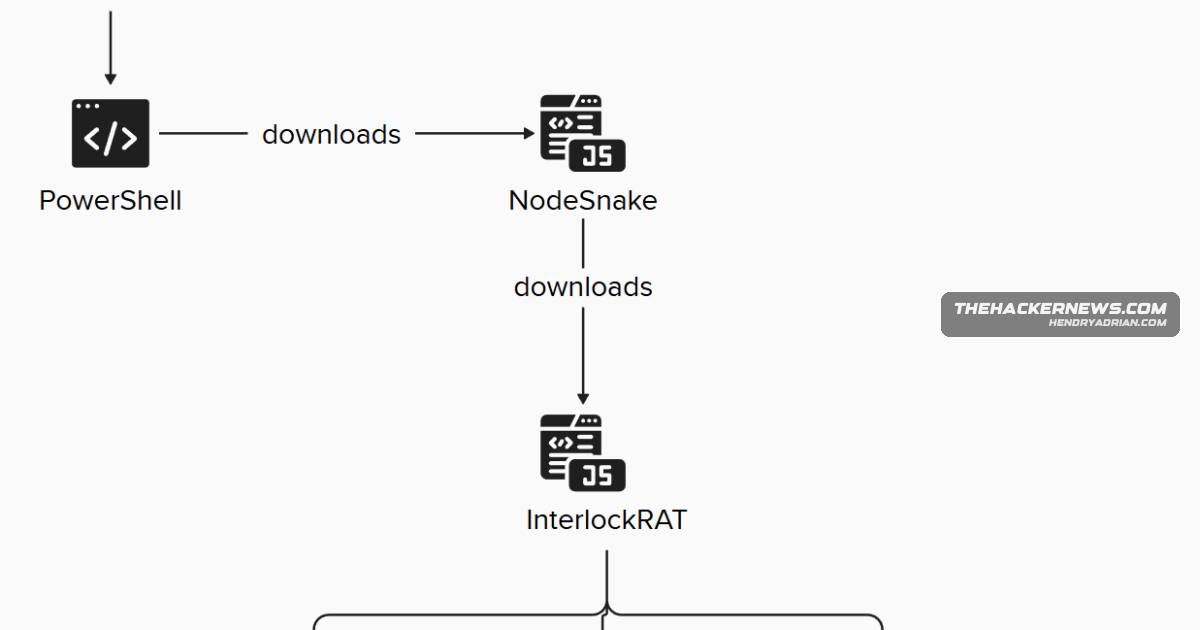
- The reported attack used ClickFix to trick a victim into running a PowerShell command that downloaded NodeSnake, which can establish persistence and launch Interlock RAT.
- Hive0163 has also used malvertising and initial access brokers TA569 and TAG-124, according to the article.
Article Details
- Event Type
- Disclosure of a suspected AI-generated PowerShell backdoor used in ransomware operations
- Impact
- In an attack observed in early 2026, Hive0163 used Slopoly to maintain access to a compromised server for more than a week. The backdoor sent system information to a command-and-control server, polled for commands, executed them, and returned results. Hive0163 operations involve data exfiltration and ransomware, but the specific commands run on the compromised network are unknown. AI assistance in Slopoly’s development is suspected, not confirmed.
MITRE ATT&CK
T1053.005 · Scheduled TaskSlopoly established persistence through a scheduled task named “Runtime Broker.”T1059.001 · PowerShellThe attack used a PowerShell command to download NodeSnake, and Slopoly is a PowerShell backdoor.T1059.003 · Windows Command ShellSlopoly executed polled commands via cmd.exe.T1082 · System Information DiscoverySlopoly beaconed system information to its C2 server.T1105 · Ingress Tool TransferThe attack’s PowerShell command downloaded NodeSnake; the framework could also retrieve and launch additional payloads.
People
Threat Actors
Hive0163The financially motivated threat actor was observed deploying Slopoly to maintain access during a ransomware attack and is reported to use ClickFix and malvertising for initial access.LandUpdate808Identified as another name for TAG-124, an initial access broker Hive0163 relies on.SocGholishIdentified as another name for TA569, an initial access broker Hive0163 relies on.TA569Identified as an initial access broker Hive0163 relies on; the article states TA569 is also known as SocGholish.TAG-124Identified as an initial access broker Hive0163 relies on; the article states TAG-124 is also known as KongTuke and LandUpdate808.WoodgnatIdentified as another name for TAG-124, an initial access broker Hive0163 relies on.
Malware
InterlockThe e-crime group is primarily associated with a wide range of malicious tools, including NodeSnake, Interlock RAT, JunkFiction loader, and Interlock ransomware.Interlock RATHive0163 leverages NodeSnake, Interlock RAT, ClickFix social engineering, malvertising, and initial access brokers like TA569 and TAG-124 for operations.JunkFiction loaderThe e-crime group is primarily associated with a wide range of malicious tools, including NodeSnake, Interlock RAT, JunkFiction loader, and Interlock ransomware.NodeSnake#SlopolySlopolyResearchers disclosed Slopoly, a suspected AI-generated PowerShell backdoor used by financially motivated threat actor Hive0163 to maintain persistent access during post-exploitation.