
AI-Assisted Slopoly Backdoor Used in Interlock Ransomware Attack
Summary
IBM X-Force says the Slopoly PowerShell backdoor, likely generated with an LLM, was used by Hive0163 in an Interlock ransomware attack to maintain persistence and exfiltrate data. Researchers found it is not truly polymorphic.
Key points
- IBM X-Force attributed the attack to the financially motivated group Hive0163.
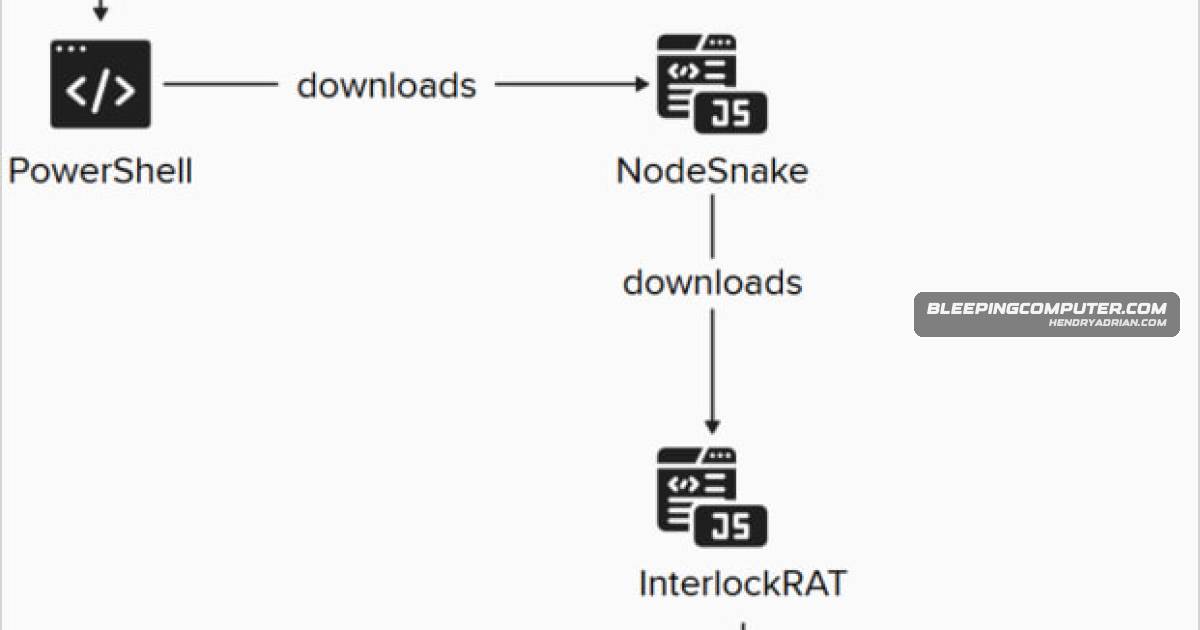
- The attack began with a ClickFix social engineering flow and included NodeSnake, InterlockRAT, and Interlock ransomware.
- Slopoly is a PowerShell C2 client that collects system information, polls for commands, executes them, and can download and run payloads.
- It persists through a scheduled task named “Runtime Broker” and was deployed under C:\ProgramData\Microsoft\Windows\Runtime.
- Researchers found signs of LLM-assisted development but could not identify which model was used.
- Despite comments describing it as polymorphic, Slopoly cannot modify its own code during execution; its builder may generate clients with varied configurations and function names.
Article Details
- Event Type
- Interlock ransomware campaign involving the Slopoly PowerShell backdoor, attributed by IBM X-Force to Hive0163.
- Impact
- The attack reportedly kept an actor on a compromised server for more than a week and involved data theft. Slopoly could collect system information, execute commands, download payloads, and send command output to its C2 server; the Interlock ransomware encrypted files.
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelSlopoly sends command output back to its C2 server; the attack was also reported to involve data theft.T1053.005 · Scheduled TaskSlopoly established persistence through a scheduled task named “Runtime Broker.”T1059.001 · PowerShellSlopoly is a PowerShell script used as a backdoor.T1059.003 · Windows Command ShellSlopoly executes received commands via cmd.exe.T1105 · Ingress Tool TransferSlopoly supports downloading payloads, including EXE, DLL, and JavaScript files.
Threat Actors
Malware
BroomstickIBM reports that Hive0163 may also have associations with the developers behind Broomstick, SocksShell, PortStarter, SystemBC, and the Rhysida ransomware operators.InterlockIBM X-Force analyzed a new PowerShell backdoor called Slopoly, likely generated with a large language model, which was used in an Interlock ransomware campaign to maintain persistence and exfiltrate data.InterlockRATThe attack chain began with a ClickFix social engineering ruse and included other components like NodeSnake, InterlockRAT, and the Interlock ransomware delivered via JunkFiction.JunkFictionThe attack chain began with a ClickFix social engineering ruse and included other components like NodeSnake, InterlockRAT, and the Interlock ransomware delivered via JunkFiction.NodeSnakeThe attack chain began with a ClickFix social engineering ruse and included other components like NodeSnake, InterlockRAT, and the Interlock ransomware delivered via JunkFiction.PortStarterIBM reports that Hive0163 may also have associations with the developers behind Broomstick, SocksShell, PortStarter, SystemBC, and the Rhysida ransomware operators.SlopolyIBM X-Force analyzed a new PowerShell backdoor called Slopoly, likely generated with a large language model, which was used in an Interlock ransomware campaign to maintain persistence and exfiltrate data.SocksShellIBM reports that Hive0163 may also have associations with the developers behind Broomstick, SocksShell, PortStarter, SystemBC, and the Rhysida ransomware operators.SystemBCIBM reports that Hive0163 may also have associations with the developers behind Broomstick, SocksShell, PortStarter, SystemBC, and the Rhysida ransomware operators.
Products
Microsoft WindowsThe Interlock ransomware payload observed in the attacks reported by IBM is a 64-bit Windows executable delivered via the JunkFiction loader.PowerShellIBM X-Force analyzed a new PowerShell backdoor called Slopoly, likely generated with a large language model, which was used in an Interlock ransomware campaign to maintain persistence and exfiltrate data.