
CNCERT Warns OpenClaw Flaws Could Enable Prompt Injection and Data Theft
Summary
CNCERT warned that OpenClaw’s weak defaults and privileged access could expose systems to prompt injection. Researchers demonstrated link-preview data exfiltration, while Huntress reported malicious installers distributing stealers and GhostSocks.
Key points
- CNCERT warned that OpenClaw’s weak default security and privileged system access could let attackers take control of endpoints.
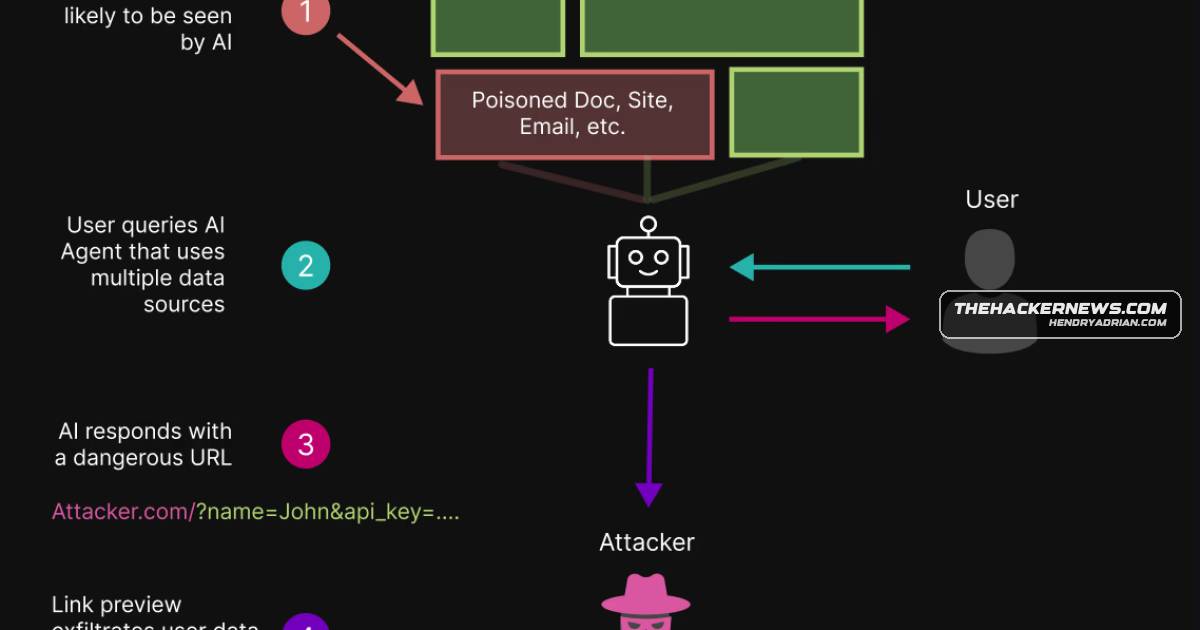
- Indirect prompt injection can manipulate an agent processing web content into leaking sensitive information.
- PromptArmor demonstrated that a messaging-app link preview could trigger data exfiltration without a user clicking the link.
- CNCERT also warned that malicious OpenClaw skills may run arbitrary commands or deploy malware, and that vulnerabilities could be exploited.
- Huntress reported malicious GitHub repositories posing as OpenClaw installers and distributing Atomic, Vidar Stealer, and GhostSocks through ClickFix-style instructions.
- CNCERT recommended isolating the service, closing exposed management ports, avoiding plaintext credentials, limiting skill sources, and keeping the agent updated.
Article Details
- Event Type
- CNCERT security warning about OpenClaw’s default security and privileged-access risks, alongside reported malicious installer repositories distributing malware.
- Impact
- Prompt injection could enable endpoint control or sensitive-data exfiltration; PromptArmor demonstrated link-preview-based exfiltration without a user click. CNCERT also warned of possible destructive actions and exploitation of OpenClaw vulnerabilities. Huntress reported malicious GitHub repositories posing as installers distributed Atomic, Vidar Stealer, and GhostSocks. CNCERT warned that breaches in finance and energy could expose sensitive business data or disrupt systems.
Malware
ATOMICResearchers demonstrated linkâpreview exfiltration and threat actors have used malicious GitHub installers to distribute Atomic and Vidar Stealer and GhostSocks, prompting restrictions and mitigation guidance.GhostSocksResearchers demonstrated linkâpreview exfiltration and threat actors have used malicious GitHub installers to distribute Atomic and Vidar Stealer and GhostSocks, prompting restrictions and mitigation guidance.VidarResearchers demonstrated linkâpreview exfiltration and threat actors have used malicious GitHub installers to distribute Atomic and Vidar Stealer and GhostSocks, prompting restrictions and mitigation guidance.
Products
ClawHubThreat actors can upload malicious skills to repositories like ClawHub that, when installed, run arbitrary commands or deploy malware.OpenClawChina’s CNCERT warned that OpenClaw, an open-source autonomous AI agent, has weak default security and privileged system access that can be abused via prompt injection to seize endpoints or leak sensitive data.
Countries
Industries
Energy“For critical sectors – such as finance and energy – such breaches could lead to the leakage of core business data, trade secrets, and code repositories, or even result in the complete paralysis of entire businessfinance“For critical sectors – such as finance and energy – such breaches could lead to the leakage of core business data, trade secrets, and code repositories, or even result in the complete paralysis of entire business