
Phishers Abuse LiveChat to Impersonate PayPal and Amazon and Harvest Sensitive Data
Summary
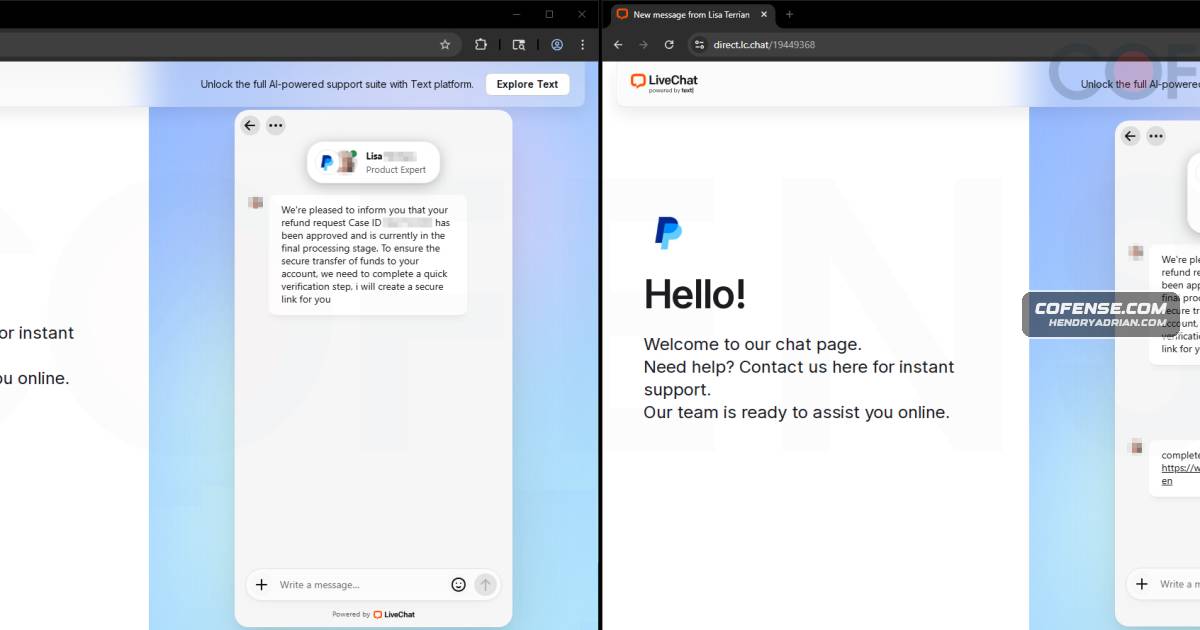
Cofense PDC describes phishing campaigns abusing LiveChat pages to impersonate PayPal and Amazon. Chat flows harvest credentials, MFA codes, card data and PII; the report details redirect and form stages but does not report confirmed victim compromise.
Key points
- Cofense PDC describes two phishing variants using emails with a purported PayPal refund or a pending-order lure.
- Email links lead to LiveChat-hosted pages at lc[.]chat, where attackers use real-time chats to make the scams resemble customer support.
- In the PayPal variant, the chat redirects victims to phishing pages that collect account credentials and MFA codes, followed by billing and payment details.
- In the Amazon-branded variant, the chat directly requests email, phone number, date of birth, address, and full card details.
- The report says the collected information is intended to enable account takeover and financial fraud; it does not establish that victims were compromised.
- Cofense lists phishing infrastructure and maps the observed activity to techniques including spearphishing links, input capture, and gathering victim identity information.
Article Details
- Attack Vectors
- Phishing emails use refund or pending-order lures to direct victims to LiveChat-hosted chat pages.
- LiveChat conversations impersonate PayPal or Amazon support and solicit credentials, MFA codes, payment-card details, and personal information.
- The PayPal flow redirects victims to phishing forms; the article says the collected credentials and MFA codes are intended to enable account access and financial fraud.
- Defensive Notes
- Cofense emphasizes human-driven analysis and user reports through its Phishing Defense Center to identify and stop evolving attacks.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | paypalrefund[.]workers[.]dev | PayPal-branded phishing host used to collect login and billing information. |
| IPV4 | 104[.]21[.]20[.]86 | Listed as an IP for the PayPal phishing payload stage. |
| IPV4 | 104[.]21[.]90[.]116 | Observed IP associated with the LiveChat phishing redirects. |
| IPV4 | 149[.]154[.]166[.]110 | Listed among the IPs for the PayPal phishing payload stage, which includes a Telegram bot API endpoint. |
| IPV4 | 162[.]159[.]140[.]229 | Observed IP associated with the Email 2 phishing URL. |
| IPV4 | 172[.]67[.]192[.]3 | Listed as an IP for the PayPal phishing payload stage. |
| IPV4 | 172[.]67[.]200[.]101 | Observed IP associated with the LiveChat phishing redirects. |
| IPV4 | 23[.]48[.]203[.]38 | Listed as an IP for the PayPal phishing payload stage. |
| IPV4 | 23[.]48[.]203[.]39 | Listed as an IP for the PayPal phishing payload stage. |
| IPV4 | 23[.]53[.]11[.]166 | Listed among IPs observed with the Amazon-variant phishing payload. |
| IPV4 | 23[.]53[.]11[.]168 | Listed among IPs observed with the Amazon-variant phishing payload. |
| IPV4 | 23[.]53[.]11[.]171 | Listed among IPs observed with the Amazon-variant phishing payload. |
| IPV4 | 23[.]53[.]11[.]176 | Listed among IPs observed with the Amazon-variant phishing payload. |
| URL | hxxps[:]//api[.]telegram[.]org/bot8584408242:AAGFK13zX70Zq_ezkA-BUAr-x6Jn308BlmI/sendMessage | Telegram bot API endpoint identified in the article as used for actor tooling or notifications. |
| URL | hxxps[:]//direct[.]lc[.]chat/19252309 | Specific LiveChat-hosted chat page used in the Amazon-impersonation phishing flow. |
| URL | hxxps[:]//direct[.]lc[.]chat/19449368 | Specific LiveChat-hosted chat page used as a stage in the PayPal phishing flow. |
| URL | hxxps[:]//t[.]co/56TlmnQA0M | Shortened URL used in the Email 2 phishing campaign. |
| URL | hxxps[:]//www[.]govnet[.]co[.]za/?redirect=hXXps%3A%2F%2Fdirect[.]lc[.]chat%2F19449368 | Initial phishing URL that redirects victims to a LiveChat-hosted phishing page. |
| URL | hxxps[:]//www[.]paypalrefund[.]workers[.]dev/en?utm_medium=chat&utm_campaign=link-shared-in-chat&utm_source=livechat[.]com&utm_content=direct[.]lc[.]chat | Specific PayPal-branded phishing page linked from the LiveChat chat. |
MITRE ATT&CK
T1056 · Input CapturePhishing chats and forms collect credentials, MFA codes, and credit-card details entered by victims.T1078 · Valid AccountsThe article says stolen PayPal credentials and captured MFA codes are intended to enable account access; successful account access is not confirmed.T1566.001 · Spearphishing AttachmentPhishing emails contain links that direct recipients to LiveChat-hosted pages.T1566.003 · Spearphishing via ServiceThe campaign uses LiveChat as a service to engage victims in real-time phishing conversations.T1589 · Gather Victim Identity InformationThe Amazon-impersonation chat requests victims' phone numbers, dates of birth, and addresses.
Products
AmazonPDC observed a phishing campaign that uses the LiveChat SaaS platform to impersonate brands (PayPal and Amazon) and engage victims in real-time chat to harvest credentials, credit card details, MFA codes, and PII.LiveChatCofense PDC observed a phishing campaign that uses the LiveChat SaaS platform to impersonate brands (PayPal and Amazon) and engage victims in real-time chat to harvest credentials, credit card details, MFA codes, andPaypalCofense PDC observed a phishing campaign that uses the LiveChat SaaS platform to impersonate brands (PayPal and Amazon) and engage victims in real-time chat to harvest credentials, credit card details, MFA codes, and