
Bitrefill Blames Lazarus-Linked BlueNoroff for Breach Exposing 18,500 Purchase Records
Summary
Bitrefill says attackers accessed production secrets and some cryptocurrency wallets after compromising an employee laptop. The breach exposed about 18,500 purchase records; the company attributes the attack to Lazarus-linked BlueNoroff.
Key points
- Bitrefill says the intrusion began with a compromised employee laptop and stolen legacy credentials, which were used to access production secrets and parts of its infrastructure.
- The company reports that attackers drained some hot wallets and exploited gift card inventory and supply lines; user balances were not affected.
- About 18,500 purchase records containing customer email, IP, and cryptocurrency payment addresses were exposed; around 1,000 also included names. Bitrefill says attackers may have obtained decryption keys.
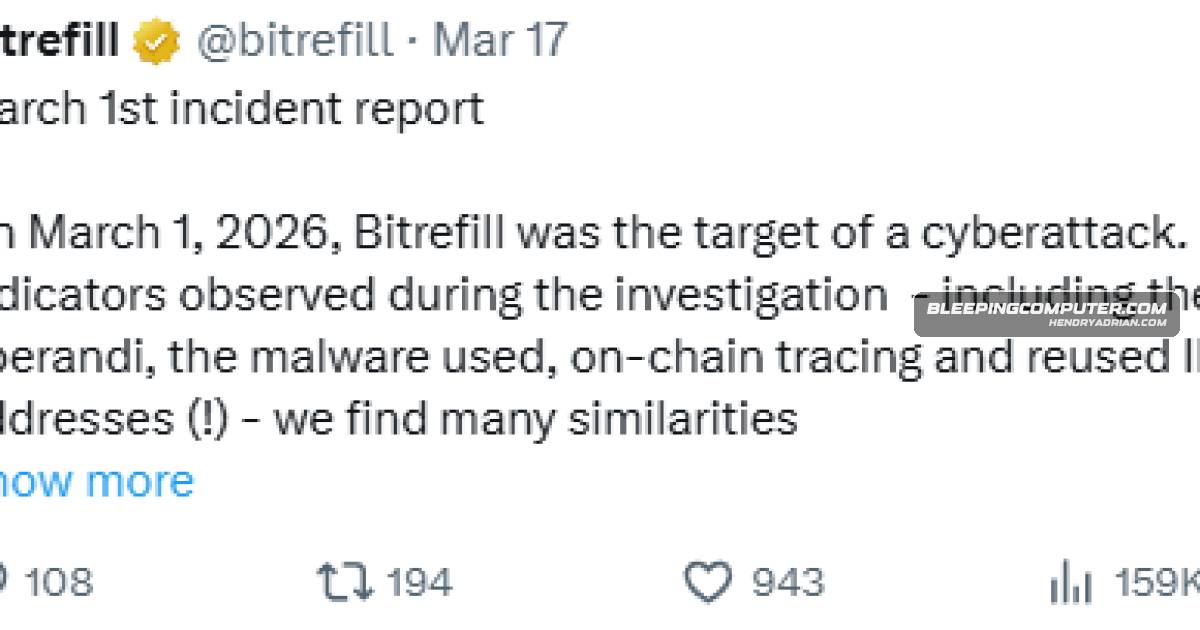
- Bitrefill assesses that the attack was likely carried out by Lazarus-linked BlueNoroff, citing similarities in tactics, malware, reused IP addresses and email addresses, and on-chain tracing.
- Bitrefill reports minimal losses, says most services have returned to normal, and is expanding security reviews, penetration testing, access controls, logging, monitoring, and automated shutdown mechanisms.
Article Details
- Victim Organization
- Bitrefill
- Incident Type
- Cyberattack and data breach involving a compromised employee laptop, stolen legacy credentials, access to production secrets and infrastructure, and theft from some cryptocurrency hot wallets and gift card inventory. Bitrefill said the attack was likely carried out by BlueNoroff/Lazarus.
- Data Types Exposed
- Customer email addresses
- IP addresses
- Cryptocurrency payment addresses
- Customer names
- Potentially decryption keys; Bitrefill said attackers may have obtained them
- Affected Records
- Approximately 18,500 purchase records were exposed; about 1,000 included customer names.
- Operational Impact
- Bitrefill took all services offline after identifying a security issue. Gradual restoration followed, and most services had returned to normal operational status by the report. Some hot wallets and gift card inventory were drained; Bitrefill reported minimal losses, to be covered from its capital.
- Ransom Or Extortion
- No ransom or extortion activity was reported. Bitrefill believed the attackers sought cryptocurrency and gift card inventory rather than customer data.
- Claim Status
- confirmed
MITRE ATT&CK
Threat Actors
APT38The article identifies APT38 as another name for BlueNoroff, which Bitrefill said likely carried out the attack.BlueNoroffBitrefill said the attack was likely carried out by BlueNoroff, citing similarities in tactics, malware, reused IP and email indicators, and on-chain tracing. The article identifies BlueNoroff as also known as APT38 and as a cluster of the Lazarus group.LazarusBitrefill said the attack was likely associated with the DPRK Lazarus group; the article describes BlueNoroff as a cluster of Lazarus.
Countries
Industries
CryptocurrencyAttackers compromised an employee laptop, stole legacy credentials, and accessed production snapshots, databases, and some cryptocurrency wallets.E-commerceBitrefill is a mid-sized e-commerce platform that enables people to pay in cryptocurrency for gift cards at stores in 150 countries.