
Speagle Malware Abuses Cobra DocGuard to Steal Data
Summary
Researchers report that Speagle abuses Cobra DocGuard’s client and compromised servers to collect and exfiltrate data from systems with the software installed. Delivery remains unknown, and attribution is unresolved.
Key points
- Speagle targets systems with Cobra DocGuard installed and uses the software’s client and compromised server infrastructure to disguise command-and-control and data exfiltration.
- The malware collects system details, browser history, autofill data, and files from specific folders in phases.
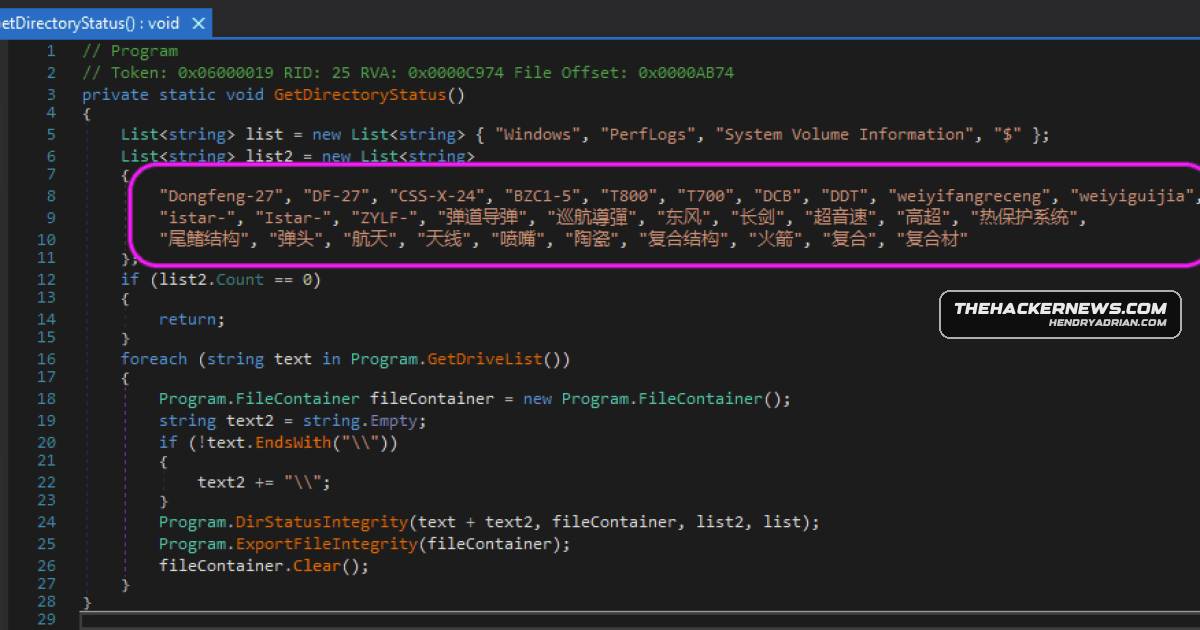
- A Speagle variant can enable or disable certain data-collection functions and search for files related to China’s Dongfeng-27 (DF-27) missile.
- Speagle invokes a Cobra DocGuard-associated driver to delete itself from compromised hosts.
- Researchers suspect supply-chain delivery based on earlier trojanized Cobra DocGuard updates, but the delivery method is unknown.
- Attribution remains unknown; researchers suggest a state-sponsored actor or hired private contractor as possibilities.
Article Details
- Event Type
- Malware campaign involving Speagle abuse of Cobra DocGuard and compromised servers
- Impact
- Speagle targets systems with Cobra DocGuard installed, collecting system details, browser history, autofill data, and files from specific folders, then exfiltrating them through a compromised Cobra DocGuard server. One variant can change which data it collects and search for files related to Dongfeng-27 missiles. Researchers suspect possible intelligence collection or industrial espionage, but the activity's attribution and delivery method remain unknown.
MITRE ATT&CK
T1005 · Data from Local SystemSpeagle collects browser history, autofill data, and files from specific folders on infected systems.T1041 · Exfiltration Over C2 ChannelSpeagle exfiltrates collected data through a compromised Cobra DocGuard server used for command-and-control.T1082 · System Information DiscoverySpeagle collects details about the infected system.