
MalwareINFO Pro Walkthrough Traces Obfuscated JSE and PowerShell Payloads
Summary
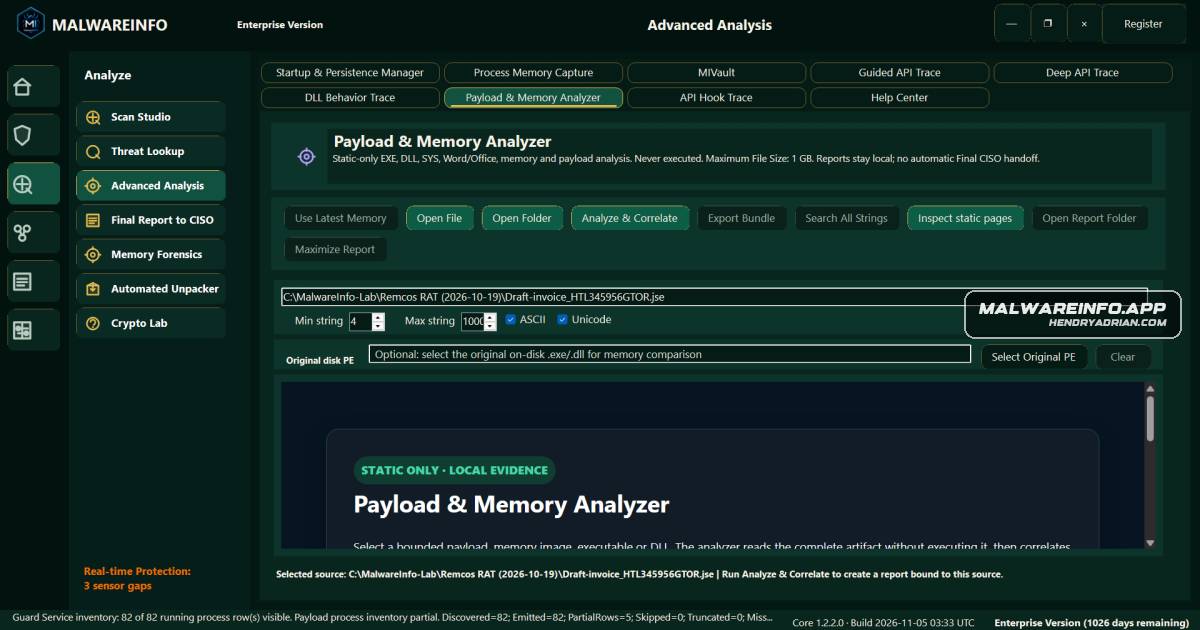
A MalwareINFO Pro walkthrough traces an obfuscated JSE and encrypted PowerShell wrapper through recovered source, embedded PE files, and configured endpoint candidates, while distinguishing recovered artifacts from unobserved runtime behavior.
Key points
- The Analyzer processes the files locally without running scripts, loading recovered binaries, or contacting infrastructure.
- For the JSE, it identifies a string-table lookup with custom Base64 and UTF-8 handling and an RC4-style decoder; 30 expression edits were proven, while receiver identity and dispatch remained unknown.
- The JSE references a PowerShell URL at eight source locations and includes XMLHTTP and WScript.Shell references, but whether those operations occurred at runtime is unconfirmed.
- The PowerShell wrapper's Base64 data was decrypted with AES-CBC and decompressed with GZip; the recovered source matched the wrapper's declared SHA-256.
- Analysis recovered a 48,128-byte artifact through Base64 and repeating-key XOR transformations, plus a separate 525,312-byte embedded PE. A successful load or invocation was not observed.
- The PE configuration contained two endpoint candidates, speed1989[.]duckdns[.]org:1926 and speed11989[.]duckdns[.]org:1926, marked ConfiguredNotObserved; no network activity was collected.
- The reports did not establish a byte-for-byte link between the JSE and PowerShell samples.
Article Details
- Topic
- Static analysis of obfuscated JSE and PowerShell samples, including embedded payloads and configured endpoint recovery.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | speed11989[.]duckdns[.]org | Configured endpoint candidate recovered from the embedded PE configuration, on port 1926; network activity was not observed. |
| DOMAIN | speed1989[.]duckdns[.]org | Configured endpoint candidate recovered from the embedded PE configuration, on port 1926; network activity was not observed. |
| SHA256 | d95545c0e33718b54ab4390fea8df29b837dcbda4c5dfa16ae920fb7113e647c | SHA-256 of the PowerShell sample analyzed in the invoice-themed malware case. |
| SHA256 | f112741ad67f4b361360ec6ad605e767f4a1a1b1a85f3dc0f72994af4d119386 | SHA-256 of the JSE sample analyzed in the invoice-themed malware case. |
| URL | hxxp[:]//77[.]73[.]20[.]112/host/secured_stub[.]ps1 | URL identified in the JSE report as an IOC and next lead in the analyzed script chain. |