
CYFIRMA Reports Invoice-Themed Phishing Targeting Finance and Procurement
Summary
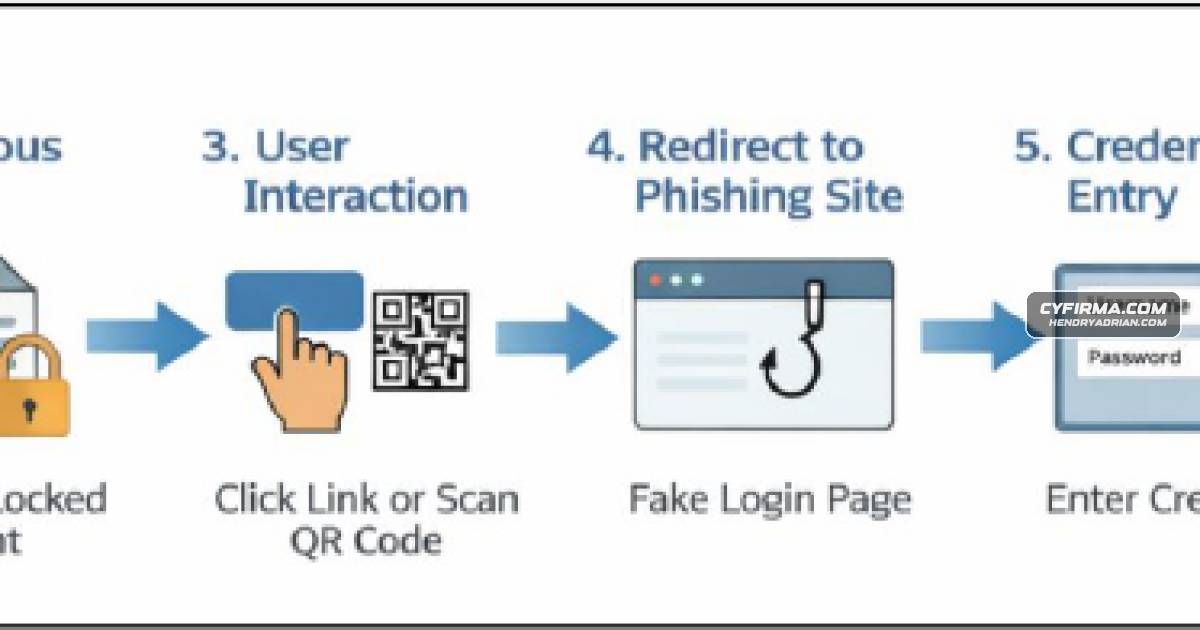
CYFIRMA reports an ongoing campaign using invoice and payment emails with obfuscated PDFs, links and QR codes to redirect finance and procurement staff to credential-harvesting pages; kits reuse front ends while rotating backend infrastructure.
Key points
- CYFIRMA reports that the campaign uses invoice, payment, and procurement-themed email lures aimed at finance and procurement staff.
- Malicious PDFs use blurred or restricted content and embedded links or QR codes to prompt user interaction and redirect to fraudulent login pages.
- The report says multiple phishing kits share similar front-end templates but vary their backend infrastructure and redirection logic.
- CYFIRMA associates increased activity with financial year-end workflows, including reconciliations, vendor payments, and audits.
- The reported objective is credential harvesting; the article describes potential risks including unauthorized access and financial fraud.
- Recommended defenses include attachment sandboxing, phishing-resistant MFA, conditional access, web filtering, targeted training, and monitoring for credential exposure.
Article Details
- Event Type
- Ongoing invoice- and payment-themed phishing campaign using malicious PDFs and QR codes to redirect finance and procurement staff to credential-harvesting sites.
- Impact
- The campaign seeks to steal credentials, potentially enabling unauthorized access, business email compromise, and financial fraud.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| URL | hxxps[:]//login[.]example | Listed as a phishing URL that redirects users to a credential-harvesting site mimicking a login portal. |
| URL | hxxps[:]//pay[.]example | Listed as a phishing URL used in the campaign's credential-harvesting redirection. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationPDF content is blurred, restricted, or partially concealed to prompt interaction and hinder inspection.T1036 · MasqueradingBusiness-themed emails and login pages are crafted to appear legitimate.T1056.003 · Web Portal CaptureFraudulent web login portals capture credentials entered by users.T1204.002 · Malicious FileUser interaction with PDF links, buttons, or QR codes triggers redirection to phishing pages.T1566.001 · Spearphishing AttachmentThe campaign delivers malicious PDF attachments through business-themed phishing emails.T1566.002 · Spearphishing LinkLinks embedded in PDFs redirect users to fraudulent login pages.