
Payload Claims HOPPECKE Singapore Was Targeted
Summary
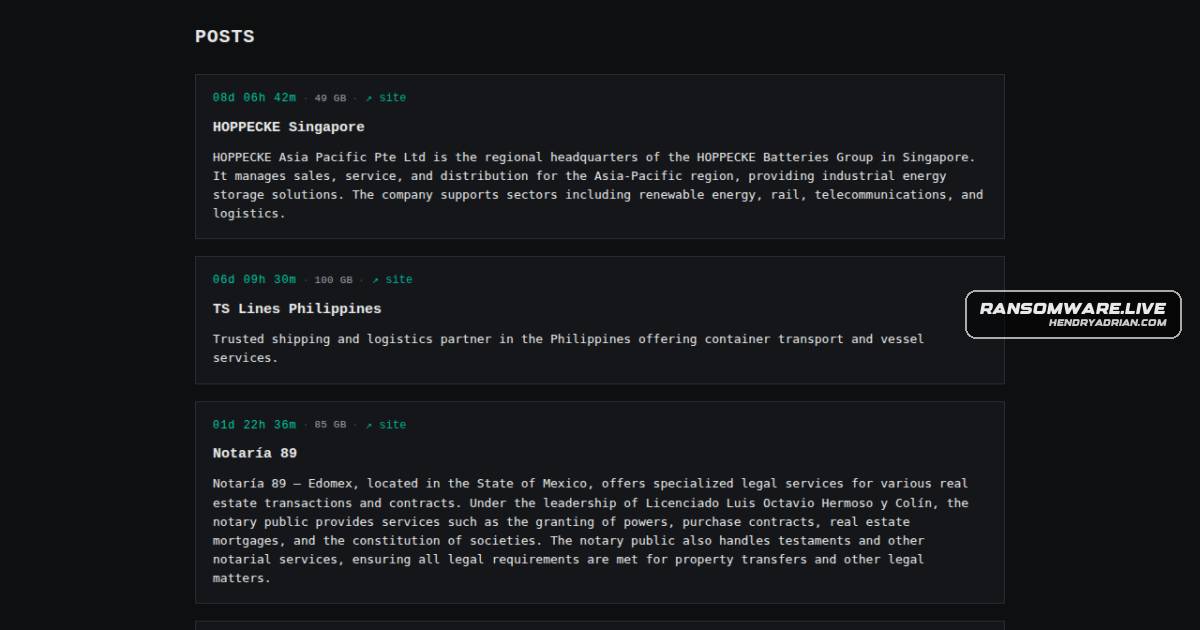
A ransomware.live monitoring record attributes a claim about HOPPECKE Singapore to Payload. The claim alleges encryption or operational disruption, but the article says it cannot confirm the information.
Key points
- The monitoring record names HOPPECKE Singapore as the claimed victim and Payload as the actor.
- The claim is attributed to a Payload leak-site post and monitored by ransomware.live.
- The post alleges encryption or disruption but provides no independent confirmation.
- The article identifies HOPPECKE Singapore as the HOPPECKE Batteries Group’s Asia-Pacific regional headquarters. It does not report confirmed operational impact.
Article Details
- Victim
- HOPPECKE Singapore
- Encryption Status
- Unconfirmed; the post alleges encryption or disruption but does not verify it.
- Exfiltration Status
- Unknown
- Leak Status
- A ransomware-group claim is listed; the source says it cannot confirm the information.