
FBI Warns Iranian-Linked Hackers Are Using Telegram for Malware C2
Summary
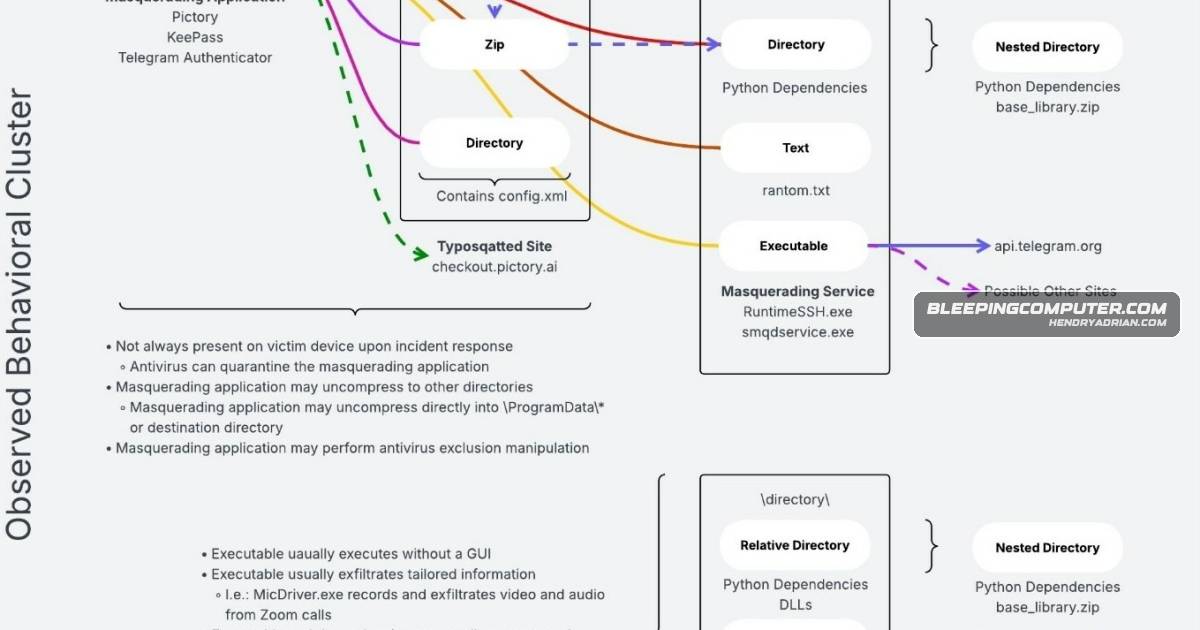
The FBI says Iranian-linked groups use Telegram as C2 for Windows malware delivered through social engineering to target journalists and dissidents and steal screenshots and files. The warning follows seizure of four group-linked domains.
Key points
- The FBI says Telegram is being used as command-and-control infrastructure in malware campaigns targeting journalists, Iranian dissidents, and other opponents.
- Social engineering is used to infect Windows devices; the malware can exfiltrate screenshots and files.
- The FBI links the activity to Handala and Homeland Justice and notes the involvement of Karma Below.
- Authorities seized four domains reportedly used by the groups for attacks and to leak stolen data.
- The article says Handala used compromised administrator accounts and Microsoft Intune to factory-reset about 80,000 devices in the Stryker incident.
Article Details
- Event Type
- FBI flash alert warning that Iranian-linked actors are using Telegram as command-and-control infrastructure for Windows malware campaigns.
- Impact
- The malware can collect and exfiltrate screenshots and files, resulting in intelligence collection, data leaks, and reputational harm, according to the FBI. In a separate attack attributed to Handala, approximately 80,000 Stryker-managed devices were factory-reset using Microsoft Intune after administrator accounts were compromised.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | handala-hack[.]to | Domain seized by the FBI that the article says was used by Handala and Homeland Justice to host leaks and coordinate attacks. |
| DOMAIN | handala-redwanted[.]to | Domain seized by the FBI that the article says was used by Handala and Homeland Justice to host leaks and coordinate attacks. |
| DOMAIN | justicehomeland[.]org | Domain seized by the FBI that the article says was used by Homeland Justice to host leaks and coordinate attacks. |
| DOMAIN | karmabelow80[.]org | Domain seized by the FBI that the article says was used by Karma Below to host leaks and coordinate attacks. |
Threat Actors
HamsaThe article identifies this as another name for Handala, which the FBI linked to malware campaigns using Telegram C2.HandalaThe FBI linked malware campaigns using Telegram C2 to this Iranian-linked hacktivist group. The article says Handala is also known as Handala Hack Team, Hatef, and Hamsa.Handala Hack TeamThe article identifies this as another name for Handala, which the FBI linked to malware campaigns using Telegram C2.HatefThe article identifies this as another name for Handala, which the FBI linked to malware campaigns using Telegram C2.Homeland JusticeThe FBI linked this Iranian state-sponsored threat group, described as tied to Iran’s IRGC, to attacks and leak-site activity.Karma BelowThe article identifies Karma Below as a threat actor that used a seized domain during attacks and to leak stolen data.
Vendors
Products
Microsoft Intunelike Karma Below, noting seizure of leak domains and citing the Handala attack on Stryker that used Microsoft Intune to wipe devices.Microsoft Windowsand Security (MOIS) and the IRGC are using Telegram as command-and-control infrastructure to deliver Windows malware against journalists, dissidents, and other opponents.TelegramIranian-linked hackers tied to the Ministry of Intelligence and Security (MOIS) and the IRGC are using Telegram as command-and-control infrastructure to deliver Windows malware against journalists, dissidents, and
Countries
Iranas Handala Hack Team, Hatef, Hamsa) and the Iranian state-sponsored Homeland Justice threat group tied to Iran’s Islamic Revolutionary Guard Corps (IRGC).United StatesThe U.S. Federal Bureau of Investigation (FBI) warned network defenders that Iranian hackers linked to the country’s Ministry of Intelligence and Security (MOIS) are using Telegram in malware attacks.