
Reports Allege Crunchyroll Breach Exposed Nearly 100GB of User Data
Summary
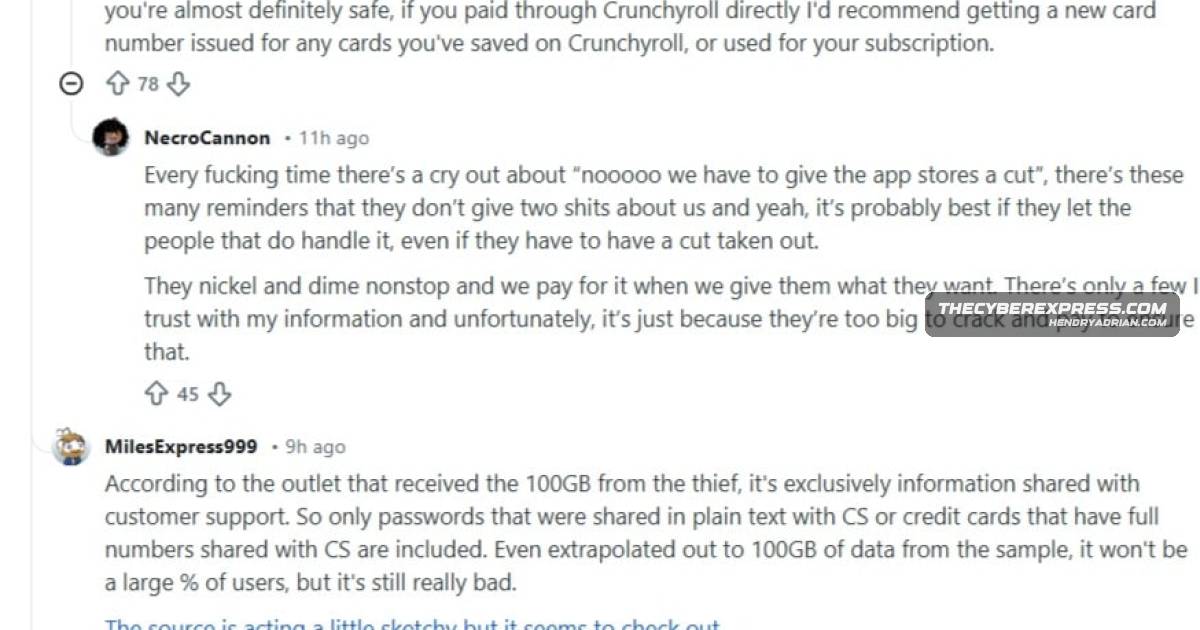
Reports allege attackers accessed Crunchyroll through a third-party vendor and exfiltrated nearly 100GB of user data. Crunchyroll says it is investigating; the breach’s scope and claims remain unconfirmed.
Key points
- Reports say the alleged breach may date to March 12, 2026, and involved nearly 100GB of data; this has not been independently confirmed in the article.
- The reported access route was a third-party vendor employee’s system, where malware was allegedly executed, followed by access to Crunchyroll’s internal environment and a ticketing system.
- The allegedly exposed data may include email and IP addresses, passwords shared in support tickets, and partial or possibly full payment-card details.
- Crunchyroll said it was aware of the claims and was investigating with cybersecurity experts; it had not confirmed the full scope.
- The article notes potential phishing and credential-stuffing risks if the reported data exposure is substantiated.
- It advises users to change passwords, avoid reusing them, monitor financial statements and be cautious of phishing.
Article Details
- Victim Organization
- Crunchyroll
- Incident Type
- Alleged data breach involving access through a third-party vendor endpoint, followed by reported access to Crunchyroll's internal systems and ticketing system and alleged data exfiltration.
- Incident Date
- 2026-03-12
- Data Types Exposed
- Email addresses
- IP addresses
- Passwords
- Credit card information, reportedly often incomplete and possibly including full card numbers in a small subset of records
- Customer analytics and support data
- Affected Data Size
- Nearly 100GB, according to reports; unconfirmed by Crunchyroll.
- Operational Impact
- Reports allege access to internal systems and a ticketing system, with customer data extracted. No service disruption is reported, and Crunchyroll has not confirmed the scope.
- Claim Status
- alleged