
Cofense Identifies Xiaomi-Themed Phishing Campaign That Captures Account Credentials
Summary
Cofense PDC identified a phishing campaign targeting Xiaomi users with impersonation emails that lead to a counterfeit Mi Account page designed to capture submitted credentials.
Key points
- Cofense PDC reported a phishing campaign targeting Xiaomi users with emails impersonating HR, IT, or account services.
- The emails claim a new certification needs review and use a masked link and 24-hour urgency to prompt clicks.
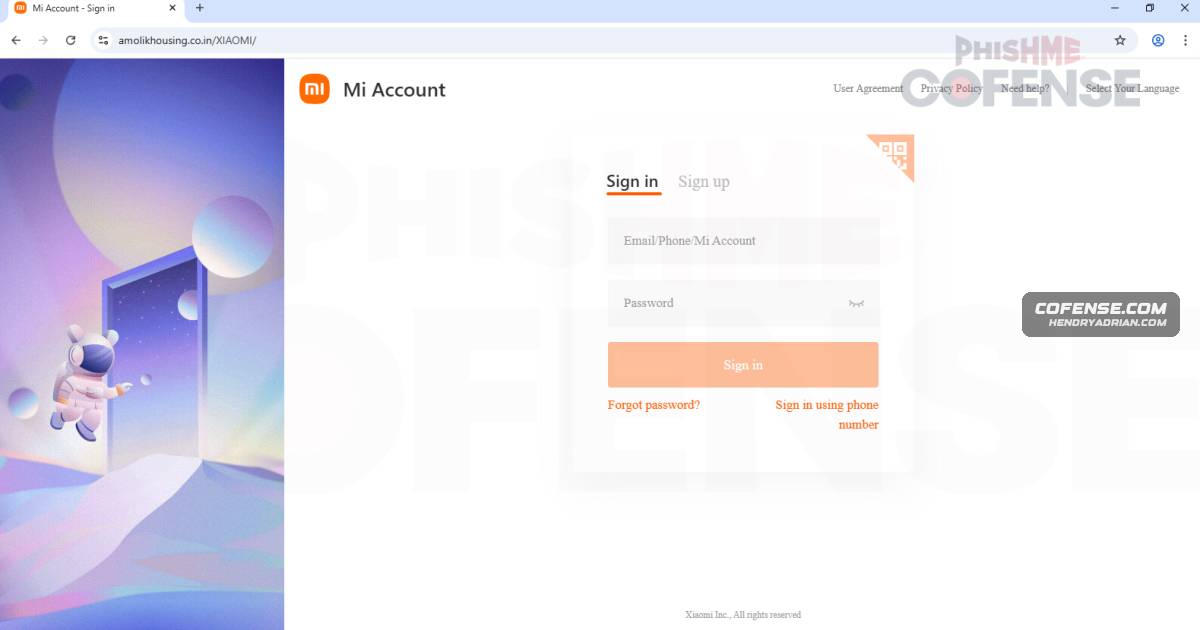
- The counterfeit Mi Account page at hxxps://www[.]amolikhousing[.]co[.]in/XIAOMI/ imitates Xiaomi's login portal and captures credentials entered by users.
- The report lists backing@ocode[.]or[.]tz as an observed sender and 43.225.54.162 as an associated IP address.
- Cofense says the campaign relies on brand impersonation and user trust rather than malware or complex exploits.
Article Details
- Event Type
- Phishing campaign impersonating Xiaomi HR/IT and directing users to a counterfeit Mi Account login page.
- Impact
- Credentials entered on the phishing page are captured and could enable unauthorized access to sensitive data and internal systems. The article does not confirm that accounts were accessed or data was compromised.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | amolikhousing[.]co[.]in | Domain identified as hosting the counterfeit Xiaomi portal. |
backing@ocode[.]or[.]tz | Observed sender address used to deliver the phishing email. | |
| IPV4 | 43[.]225[.]54[.]162 | IP address associated with the phishing page. |
| URL | hxxps[:]//www[.]amolikhousing[.]co[.]in/XIAOMI/ | Phishing URL hosting the counterfeit Xiaomi login page used to capture credentials. |
MITRE ATT&CK
T1036 · MasqueradingThe email and phishing page imitated Xiaomi branding and corporate communications.T1204.002 · Malicious FileThe email used urgency to encourage recipients to click the malicious link.T1566 · PhishingThe campaign used impersonation emails to deliver a malicious link and lure recipients.T1566.002 · Spearphishing LinkThe email contained a masked link that redirected recipients to the counterfeit login page.