
Worldleaks Claims Ransomware Attack on Germany’s CIM
Summary
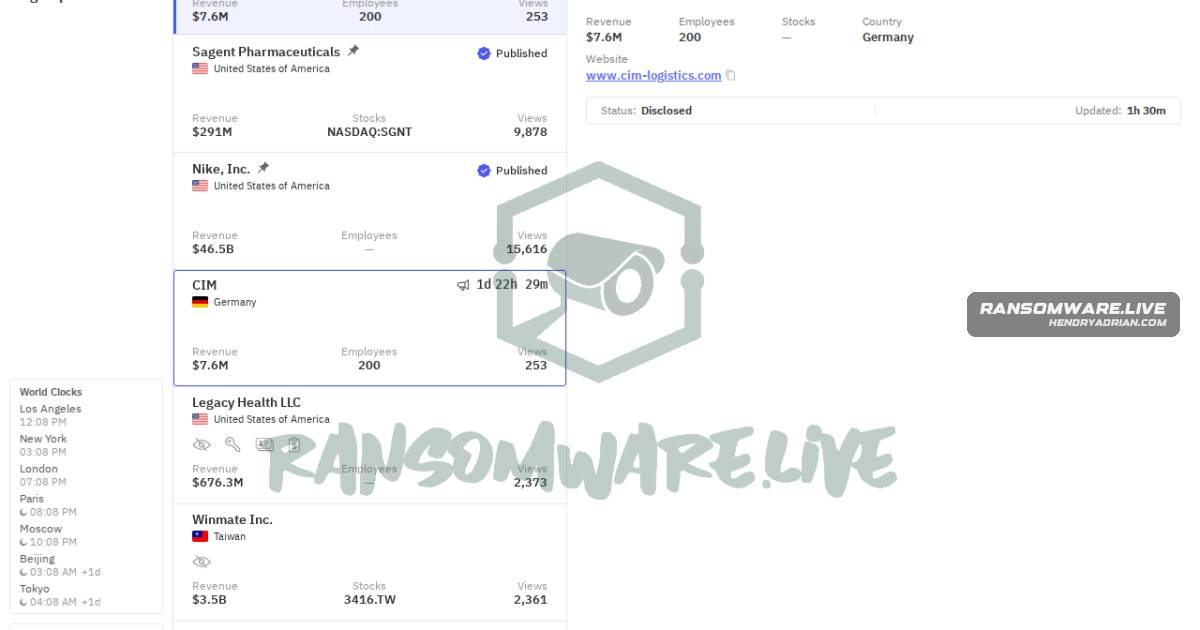
Worldleaks claims it breached CIM, a Germany-based real estate and infrastructure investment firm, and used ransomware to encrypt systems and exfiltrate data. The article says the claim is unconfirmed.
Key points
- The article attributes the breach claim to ransomware actor Worldleaks.
- Worldleaks claims it encrypted CIM systems and exfiltrated data.
- CIM is described as a Germany-based real estate and infrastructure investment firm.
- The monitoring post says the claim is based on public group claims and has not been confirmed.
Article Details
- Victim
- CIM
- Claim Date
- 2026-03-27
- Encryption Status
- Worldleaks claims ransomware was deployed to encrypt systems; not independently confirmed.
- Encrypted Size
- Not disclosed
- Exfiltration Status
- Worldleaks claims data was exfiltrated; not independently confirmed.
- Exfiltrated Data
- Not disclosed
- Exfiltrated Size
- Not disclosed
- Ransom Demand
- Not disclosed
- Leak Status
- A Worldleaks claim was listed; publication or authenticity of stolen data is not confirmed.
Threat Actors
Countries
Industries
Infrastructure investmentWorldleaks claims to have breached CIM, a Germany-based real estate and infrastructure investment firm, deploying ransomware to encrypt systems and exfiltrate data.real estateWorldleaks claims to have breached CIM, a Germany-based real estate and infrastructure investment firm, deploying ransomware to encrypt systems and exfiltrate data.