
TA446 Uses Leaked DarkSword iOS Exploit Kit in Spear-Phishing Campaign
Summary
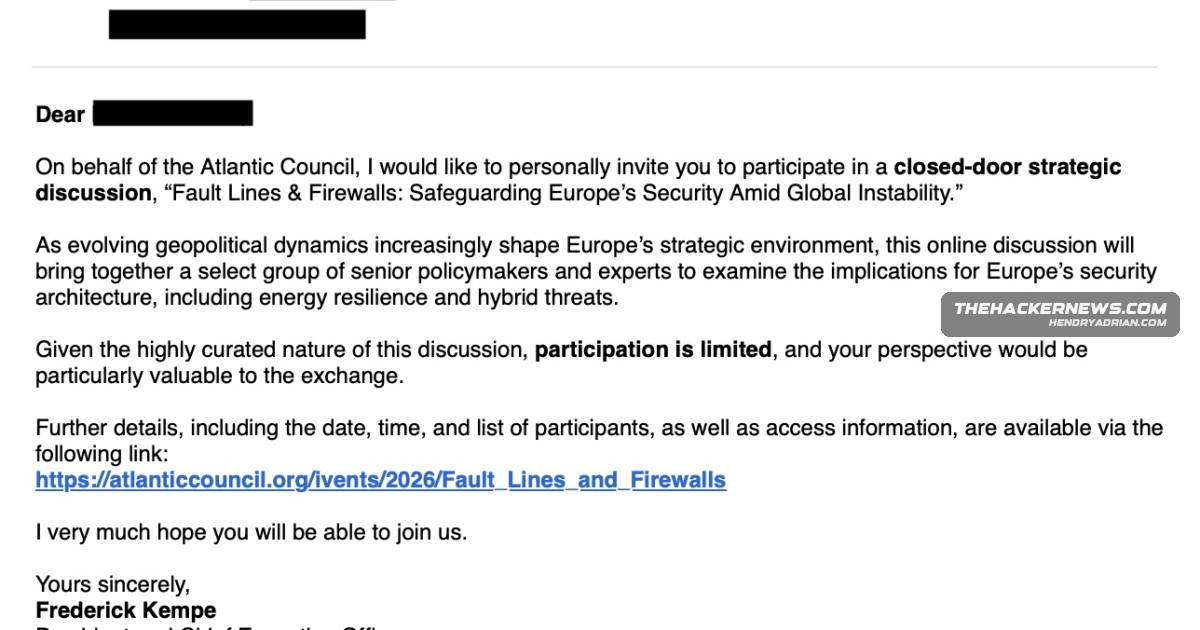
Proofpoint says Russia-linked TA446 used leaked DarkSword in spoofed Atlantic Council emails targeting iOS devices, delivering GHOSTBLADE and MAYBEROBOT. Apple warned users of older iOS and iPadOS versions as DarkSword code appeared on GitHub.
Key points
- Proofpoint attributed the campaign with high confidence to Russia-linked TA446; spoofed Atlantic Council emails were sent from compromised accounts on March 26, 2026.
- The emails targeted iPhone and iPad users, including Leonid Volkov, and reportedly reached government, think tank, higher education, financial, and legal organizations.
- The campaign used DarkSword to deliver the GHOSTBLADE dataminer; MAYBEROBOT was also deployed via password-protected ZIP files.
- A DarkSword loader referenced escofiringbijou[.]com. A urlscan[.]io result showed exploit-kit components including a redirector, loader, remote-code-execution and PAC-bypass components; no sandbox escapes were observed.
- Proofpoint's automated analysis redirected to a benign decoy PDF, likely because server-side filtering served the exploit kit only to iPhone browsers.
- Apple sent Lock Screen warnings to users of older iOS and iPadOS versions, while a new DarkSword version appeared on GitHub.
Article Details
- Event Type
- Targeted spear-phishing campaign attributed with high confidence to TA446, using the leaked DarkSword iOS exploit kit to target iPhones and iPads and deliver malware.
- Impact
- The campaign delivered the GHOSTBLADE dataminer and reportedly deployed the MAYBEROBOT backdoor via password-protected ZIP files. Proofpoint said the targeting included government, think tank, higher education, financial, and legal entities; credential harvesting and intelligence collection were suspected objectives. Apple issued Lock Screen warnings to users of older iOS and iPadOS versions. Researchers warned that the DarkSword leak could broaden access to advanced iOS exploits.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | escofiringbijou[.]com | Second-stage domain attributed to TA446 and referenced by a DarkSword loader uploaded to VirusTotal. |
MITRE ATT&CK
People
Justin AlbrechtLookout principal researcher who commented on the implications of the leaked DarkSword kit and the risk of its use by less-skilled threat actors.Leonid VolkovA recipient of the campaign emails; the article identifies him as a Russian opposition politician and political director of the Anti-Corruption Foundation.
Threat Actors
COLD RELICNamed as a moniker used by the broader cybersecurity community for the group identified in the article as TA446.Star BlizzardThe campaign was attributed with high confidence to TA446, described as Russia-linked and state-sponsored; the article assesses the group as affiliated with Russia’s FSB.
Malware
GHOSTBLADEThe attacks spoofed the Atlantic Council, delivered the GHOSTBLADE dataminer and MAYBEROBOT backdoor, and prompted Apple to send Lock Screen warnings as DarkSword code leaked on GitHub.MAYBEROBOTThe attacks spoofed the Atlantic Council, delivered the GHOSTBLADE dataminer and MAYBEROBOT backdoor, and prompted Apple to send Lock Screen warnings as DarkSword code leaked on GitHub.
Vendors
Products
iOSProofpoint disclosed a targeted email campaign by Russia-linked TA446 that used the leaked DarkSword iOS exploit kit to target iPhones and iPads.iPadOSApple has begun sending Lock Screen notifications to iPhones and iPads running older versions of iOS and iPadOS to alert users of web-based attacks and urging them to install the update to block the threat.iPhoneto a benign decoy PDF document, likely because of server-side filtering put in place to only lead iPhone browsers to the exploit kit.
Tools
Countries
Industries
financialcampaign was “much wider than usual” and that it included government, think tank, higher education, financial, and legal entities.Governmentthat the targeting observed in the email campaign was “much wider than usual” and that it included government, think tank, higher education, financial, and legal entities.Higher Educationin the email campaign was “much wider than usual” and that it included government, think tank, higher education, financial, and legal entities.Legalwas “much wider than usual” and that it included government, think tank, higher education, financial, and legal entities.Think tanktargeting observed in the email campaign was “much wider than usual” and that it included government, think tank, higher education, financial, and legal entities.