
Genesis Claims Ransomware Incident at Catalyst Learning Company
Summary
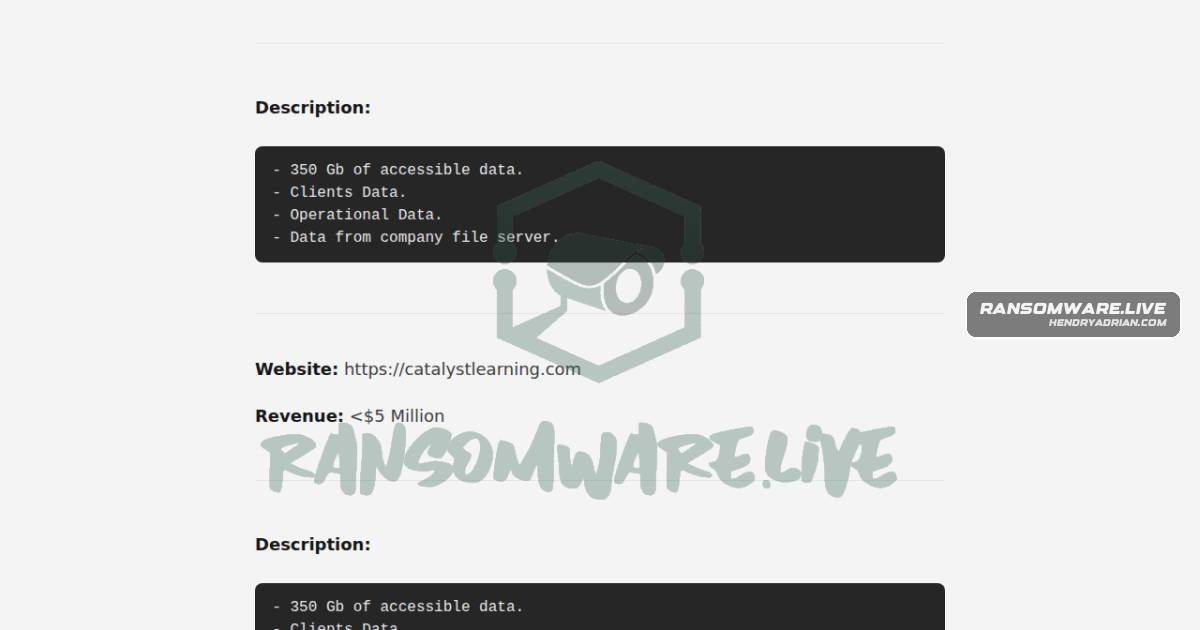
A ransomware.live-monitored entry attributes a ransomware incident claim against Catalyst Learning Company to Genesis. The entry alleges operational disruption and potential data exposure; these claims are unconfirmed.
Key points
- The record names Catalyst Learning Company in the United States as the victim and Genesis as the actor.
- It alleges operational disruption and potential data exposure, but provides no supporting incident details; these remain unconfirmed claims.
- The entry lists the claim as discovered on March 31, 2026, and published on March 31, 2026.
Article Details
- Victim
- Catalyst Learning Company
- Claim Date
- 2026-03-31
- Encryption Status
- Unknown; encryption is not reported.
- Exfiltration Status
- Unknown; exfiltration is not confirmed.
- Exfiltrated Data
- Potential data exposure is mentioned, but no specific data or confirmed exfiltration is reported.
- Ransom Demand
- Unknown; no ransom demand is reported.
- Leak Status
- No data leak or publication is reported. Genesis claims responsibility, but the source says the claim is unconfirmed.