
Genesis Claims Ransomware Attack on MC-Rx
Summary
Ransomware.live reports that the genesis group claims it targeted U.S.-based MC-Rx, alleging file encryption, possible data exfiltration, and extortion. The post says the claims are unconfirmed.
Key points
- The post identifies MC-Rx, a U.S.-based organization, as the claimed victim.
- The claim is attributed to the ransomware actor genesis and linked to an actor source; the record says it was monitored by ransomware.live.
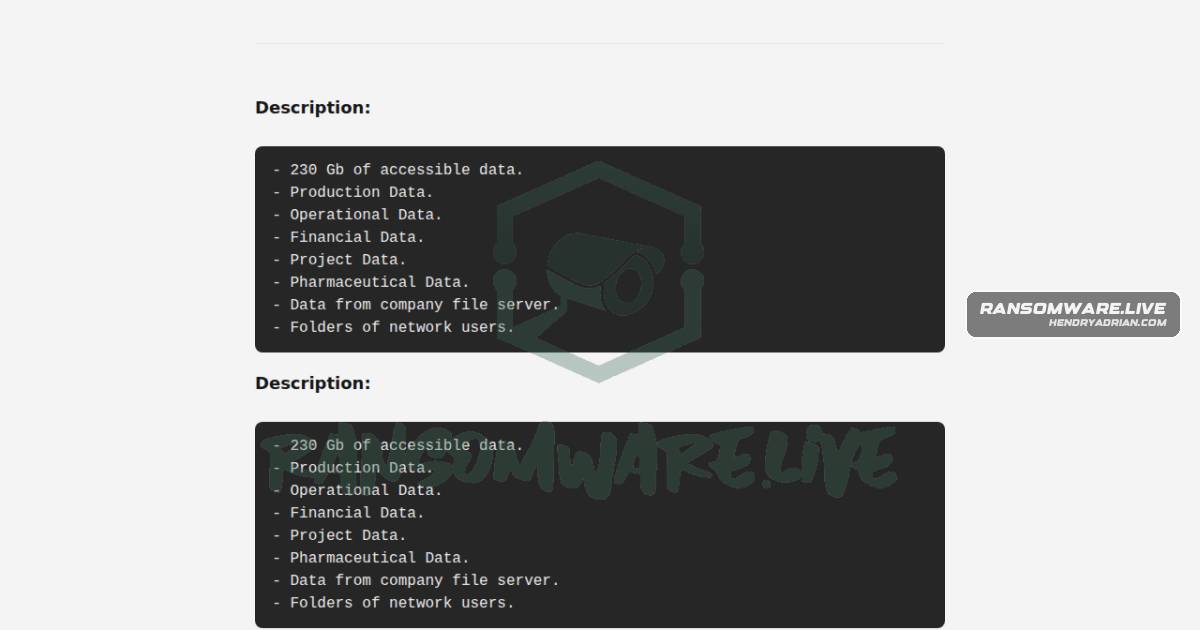
- The actor allegedly claims file encryption and possible data exfiltration, with extortion and ransom demands.
- The post says it cannot confirm the claims; it provides no independent evidence of compromise or data theft.
Article Details
- Victim
- MC-Rx
- Claim Date
- 2026-03-31
- Encryption Status
- File encryption is claimed, but the source cannot confirm the claim.
- Exfiltration Status
- Potential data exfiltration is mentioned in the claim but is unconfirmed.
- Exfiltrated Data
- No specific data types are disclosed.
- Ransom Demand
- Ransom demands are mentioned as associated with the claim; no amount or specific demand is provided.
- Leak Status
- Not disclosed