
Drift Protocol Reports $280 Million Loss After Security Council Takeover
Summary
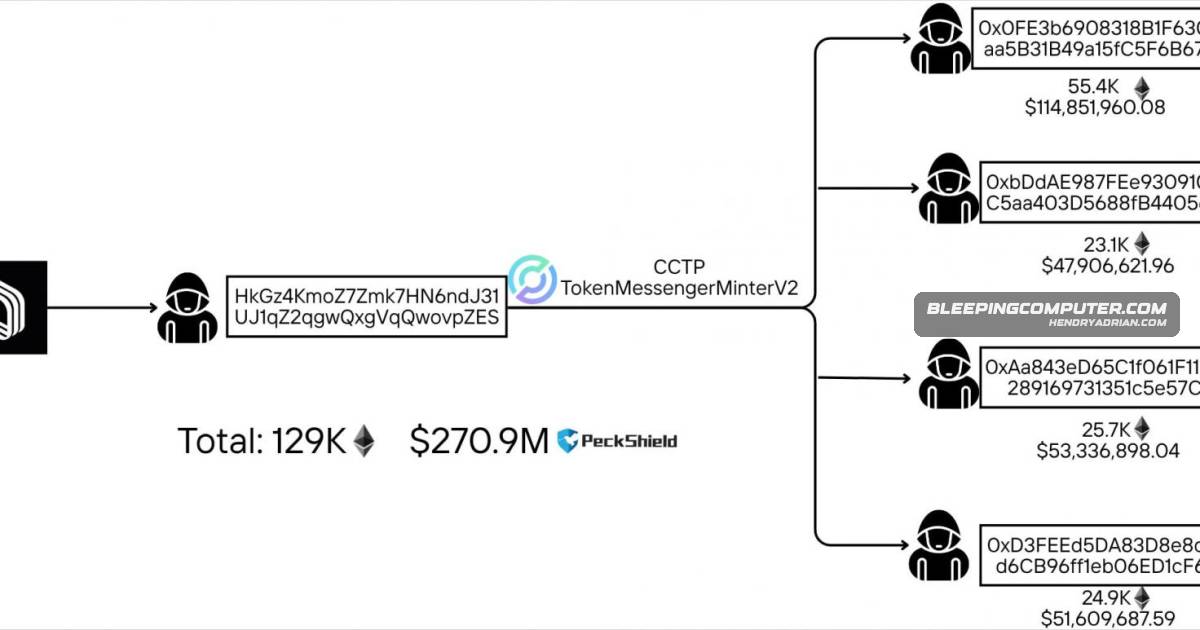
Drift Protocol reported losses of at least $280 million after an attacker seized Security Council administrative powers, added a malicious asset and removed withdrawal limits. Elliptic and TRM Labs linked the operation to DPRK tradecraft.
Key points
- The attacker reportedly obtained 2/5 Security Council multisig approvals and prepared pre-signed transactions using durable nonce accounts.
- On April 1, the attacker executed the transactions, took administrative control, added a malicious asset and removed withdrawal limits.
- Drift estimates losses at about $280 million; PeckShieldAlert estimated $285 million.
- Elliptic and TRM Labs linked the operation to North Korean tradecraft, citing on-chain indicators including Tornado Cash usage, CarbonVote timing, cross-chain bridging and rapid laundering.
- Drift said it found no smart contract flaws and that no seed phrases were compromised.
- Protocol functions are frozen; Drift said DSOL is unaffected and insurance fund assets are secured. The company is working with security firms, exchanges and law enforcement to trace and freeze funds.
Article Details
- Victim Organization
- Drift Protocol
- Incident Type
- Unauthorized takeover of Security Council administrative powers followed by theft of protocol funds
- Operational Impact
- Borrow/lend deposits, vault deposits, and trading funds were affected. Drift froze protocol functions; it said DSOL was unaffected and insurance fund assets were secured.
- Ransom Or Extortion
- Unknown
- Claim Status
- confirmed
MITRE ATT&CK
Products
Drift ProtocolDrift Protocol lost at least $280 million after a threat actor seized Security Council administrative powers in a planned, timed operation.SolanaDrift Protocol is a DeFi trading platform built on the Solana blockchain that serves as a non-custodial exchange, giving users full control of their funds as they interact with on-chain markets.