
Iran-Linked Password-Spraying Campaign Targeted Municipalities in Israel and the UAE
Summary
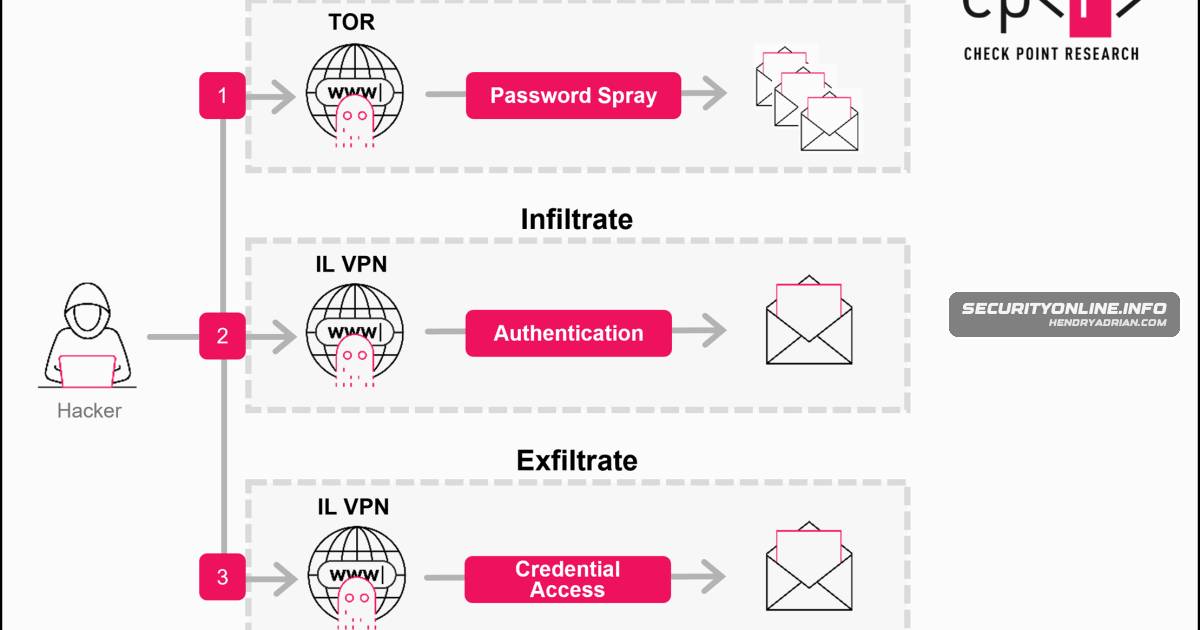
Check Point Research reports a three-wave password-spraying campaign against Microsoft 365 tenants, primarily targeting municipalities in Israel and the UAE. It assesses the activity as moderately linked to Iranian interests and Gray Sandstorm.
Key points
- Check Point Research observed campaign peaks on March 3, 13, and 23, 2026, targeting Microsoft 365 tenants.
- The campaign primarily targeted municipalities; researchers said the targeting correlated with cities struck by missiles and may have supported damage assessment.
- Attackers reportedly scanned through rotating Tor exit nodes, then used Windscribe and NordVPN endpoints geolocated in Israel to evade geo-fencing.
- The article reports more than 300 affected organizations in Israel and over 25 in the UAE, with technology, transportation, and healthcare among other targeted sectors.
- Attackers reportedly used valid credentials to access and exfiltrate municipal email.
- Check Point Research assessed the activity with moderate confidence as aligned with Iranian interests and similar to Gray Sandstorm; suggested defenses include tenant-wide MFA, conditional access, and sign-in anomaly monitoring.
Article Details
- Event Type
- Iran-linked password-spraying campaign targeting Microsoft 365 tenants
- Impact
- More than 300 organizations in Israel and over 25 in the UAE were reported impacted. Attackers used valid logins to access and exfiltrate email content. Check Point Research said municipal targeting may have supported monitoring of missile-strike responses and bombing damage assessment; this purpose was not confirmed.
MITRE ATT&CK
T1078 · Valid AccountsAttackers used valid credentials to access Microsoft 365 environments.T1110.003 · Password SprayingThe campaign used password spraying against accounts across multiple organizations.T1114.002 · Remote Email CollectionThe attackers accessed and exfiltrated email content using valid logins.
Threat Actors
Vendors
Products
Tools
NordVPNAttackers scanned via rotating Tor exit nodes, used Windscribe and NordVPN endpoints geolocated in Israel to bypass geo-fencing, and leveraged valid logins to access and exfiltrate municipal emails, a pattern CPRTorAttackers scanned via rotating Tor exit nodes, used Windscribe and NordVPN endpoints geolocated in Israel to bypass geo-fencing, and leveraged valid logins to access and exfiltrate municipal emails, a pattern CPRWindscribeAttackers scanned via rotating Tor exit nodes, used Windscribe and NordVPN endpoints geolocated in Israel to bypass geo-fencing, and leveraged valid logins to access and exfiltrate municipal emails, a pattern CPR
Countries
IranCheck Point Research tracked an Iran-linked, three-stage password-spraying campaign against Microsoft 365 tenants that peaked on March 3, 13, and 23, 2026 and primarily targeted municipalities in Israel and the UAE.IsraelCheck Point Research tracked an Iran-linked, three-stage password-spraying campaign against Microsoft 365 tenants that peaked on March 3, 13, and 23, 2026 and primarily targeted municipalities in Israel and the UAE.UAECheck Point Research tracked an Iran-linked, three-stage password-spraying campaign against Microsoft 365 tenants that peaked on March 3, 13, and 23, 2026 and primarily targeted municipalities in Israel and the UAE.