
Incransom Claims Ransomware Attack on Australian Company Mastercom
Summary
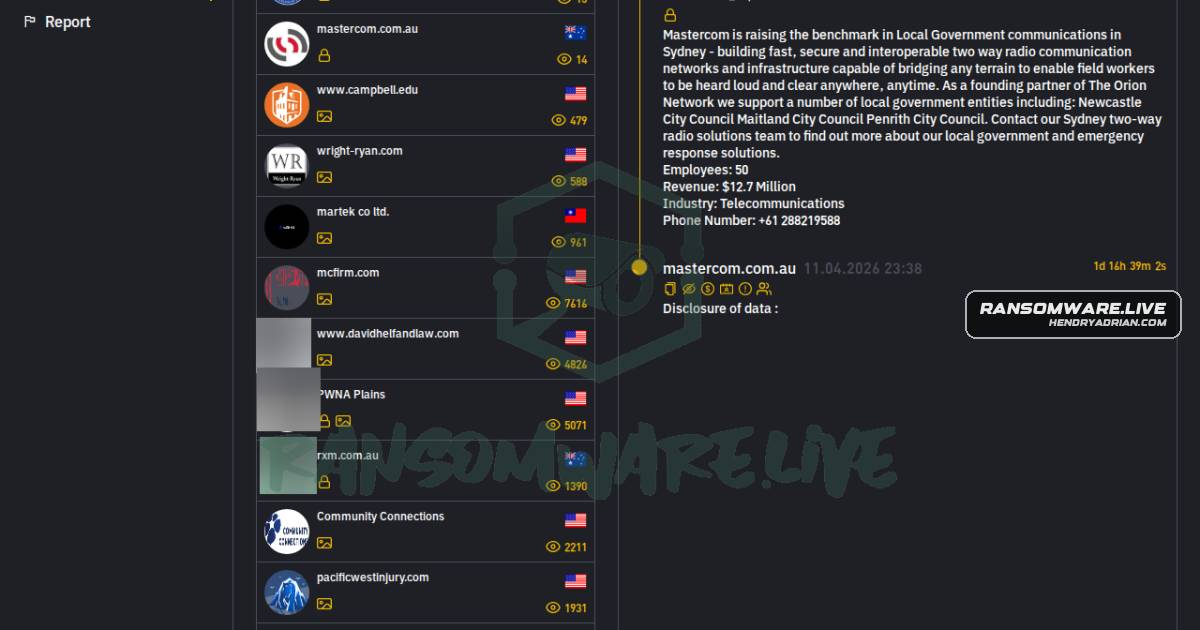
A ransomware monitoring record attributes a claim against Australian company Mastercom to incransom. It alleges an intrusion and threatened data theft or disruptive encryption; the claim is unconfirmed.
Key points
- The record names Mastercom as the victim and incransom as the ransomware actor.
- It attributes the claim to a linked actor disclosure and says it was monitored by ransomware[.]live.
- The claim alleges an intrusion and threatens data theft or disruptive encryption; the article does not confirm that either occurred.
- Mastercom is described as providing two-way radio networks and infrastructure for local governments in the Sydney area.
Article Details
- Victim
- Mastercom
- Victim Domain
- mastercom.com.au
- Claim Date
- 2026-04-11
- Encryption Status
- Unknown; the group reportedly threatened disruptive encryption, but encryption is not confirmed.
- Exfiltration Status
- Unknown; data theft was threatened, but exfiltration is not confirmed.
- Ransom Demand
- Not disclosed
- Leak Status
- The source reports a public claim by incransom; it does not confirm that data was published.