
Check Point Links SystemBC C2 to 1,570-Plus Victims and Reports The Gentlemen Activity
Summary
Check Point says a SystemBC C2 server was linked to a botnet of more than 1,570 victims and reports a The Gentlemen affiliate deployed the proxy malware; the relationship between SystemBC and the ransomware operation remains unclear.
Key points
- Check Point reports that an affiliate of The Gentlemen deployed SystemBC on a compromised host; it linked the malware's C2 server to a botnet of more than 1,570 victims.
- SystemBC creates SOCKS5 tunnels, communicates using a custom RC4-encrypted protocol, and can deliver payloads to disk or memory.
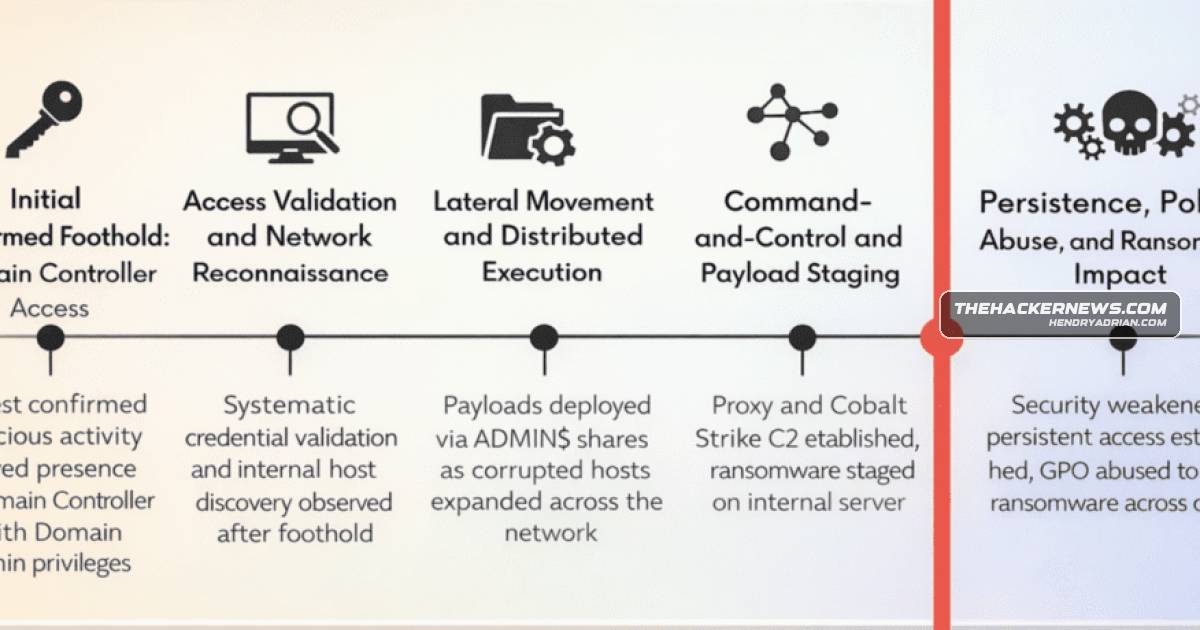
- The Gentlemen's initial access method is unclear; researchers cited possible abuse of internet-facing services or compromised credentials, followed by lateral movement and payload staging.
- Check Point says the ransomware attempts to disable Windows Defender protections on reachable hosts and uses Group Policy Objects to support domain-wide compromise.
- The Gentlemen's ESXi variant can shut down virtual machines, add persistence through crontab, and inhibit recovery before deploying ransomware.
- Rapid7 described Kyber ransomware variants targeting Windows and VMware ESXi; the ESXi variant can encrypt datastores and optionally terminate virtual machines.
- Halcyon reported that 69% of observed ransomware attack attempts were deliberately staged at night or on weekends to outpace defenders.
Article Details
- Event Type
- Check Point research linked a SystemBC command-and-control server to a botnet of more than 1,570 compromised corporate networks and reported that an affiliate of The Gentlemen ransomware operation deployed the malware.
- Impact
- The botnet represents more than 1,570 compromised networks across multiple countries. The Gentlemen has claimed more than 320 victims on its data leak site. Reported attack capabilities include cross-platform ransomware deployment, domain-wide compromise using Group Policy Objects, and disabling security protections. The precise relationship between SystemBC and The Gentlemen's operation remains unclear.
MITRE ATT&CK
T1053.003 · CronThe ESXi variant reportedly adds persistence via crontab.T1059.001 · PowerShellCheck Point described a PowerShell script pushed to reachable hosts to disable Windows Defender protections and change security settings.T1090 · ProxySystemBC establishes SOCKS5 network tunnels within victims' environments.T1105 · Ingress Tool TransferSystemBC can download and execute additional malware.T1484.001 · Group Policy ModificationThe Gentlemen's attacks abuse Group Policy Objects to facilitate domain-wide compromise.T1486 · Data Encrypted for ImpactThe ransomware is deployed to encrypt systems, including in domain-wide attacks.T1490 · Inhibit System RecoveryThe ESXi variant reportedly inhibits recovery before the ransomware binary is deployed.T1562.001 · Disable or Modify ToolsThe reported PowerShell script disables real-time monitoring and adds broad exclusions; the attacks also shut down the firewall.
People
Threat Actors
AkiraIdentified as an active ransomware group; the article describes attacks involving Akira rapidly escalating from initial access to encryption in some cases.Cl0pIdentified by ZeroFox as one of the most active groups in its Q1 2026 ransomware and digital extortion incident data.INC RansomIdentified by ZeroFox as one of the most active groups in its Q1 2026 ransomware and digital extortion incident data.QilinIdentified by ZeroFox as one of the most active groups in its Q1 2026 ransomware and digital extortion incident data.The GentlemenRansomware group whose affiliates have been observed attempting to deploy SystemBC. The group has claimed more than 320 victims, and an affiliate reportedly deployed SystemBC on a compromised host.
Malware
KyberRansomware trends show faster dwell times, specialization (e.g., Kyber, Akira), and increasing targeting of ESXi, OT, and SMB environments.SystemBCResearch shows affiliates of The Gentlemen ransomwareâasâaâservice deployed the SystemBC proxy, with its C2 linked to a botnet of over 1,570 compromised corporate networks worldwide.
Products
BSDthe group is versatile as it’s sophisticated, exhibiting capabilities to target Windows, Linux, NAS, and BSD systems with a Go-based locker as well as employing legitimate drivers and custom malicious tools toLinuxThe operation demonstrates rapid growth and versatile tooling—targeting Windows, Linux, NAS, and ESXi—while using tactics like GPO abuse and Defender disabling to enable fast, domainâwide encryptionMicrosoft Hyper-V“The Windows variant, written in Rust, includes a self-described ‘experimental’ feature for targeting Hyper-V.”Microsoft WindowsThe operation demonstrates rapid growth and versatile tooling—targeting Windows, Linux, NAS, and ESXi—while using tactics like GPO abuse and Defender disabling to enable fast, domainâwide encryptionVMware ESXirelatively new ransomware family called Kyber that surfaced in September 2025, targeting Windows and VMware ESXi infrastructures using encryptors developed in Rust and C++, respectively.Windows Defender“During lateral movement, the ransomware makes an attempt to blind Windows Defender on each reachable remote host by pushing a PowerShell script that disables real-time monitoring, adds broad exclusions for the drive,
Tools
Countries
Australiamalware commandeering hundreds of victims across the globe, including the U.S., the U.K., Germany, Australia, and Romania.Germanyto the proxy malware commandeering hundreds of victims across the globe, including the U.S., the U.K., Germany, Australia, and Romania.Romaniahundreds of victims across the globe, including the U.S., the U.K., Germany, Australia, and Romania.United Kingdomlinked to the proxy malware commandeering hundreds of victims across the globe, including the U.S., the U.K., Germany, Australia, and Romania.United StatesC2 server linked to the proxy malware commandeering hundreds of victims across the globe, including the U.S., the U.K., Germany, Australia, and Romania.
Industries
Automotivemore disciplined and a business-driven criminal enterprise, even as ransomware attacks targeting the automotive industry more than doubled in 2025, taking up 44% of all cyber incidents across the sector.Operational technologycriminal ransomware campaigns, and increased targeting of small and mid-sized organizations and operational technology (OT) environments.