
OpenAI Says AI Pipeline Generated 948 Linux Privilege-Escalation Exploits in 30 Hours
Summary
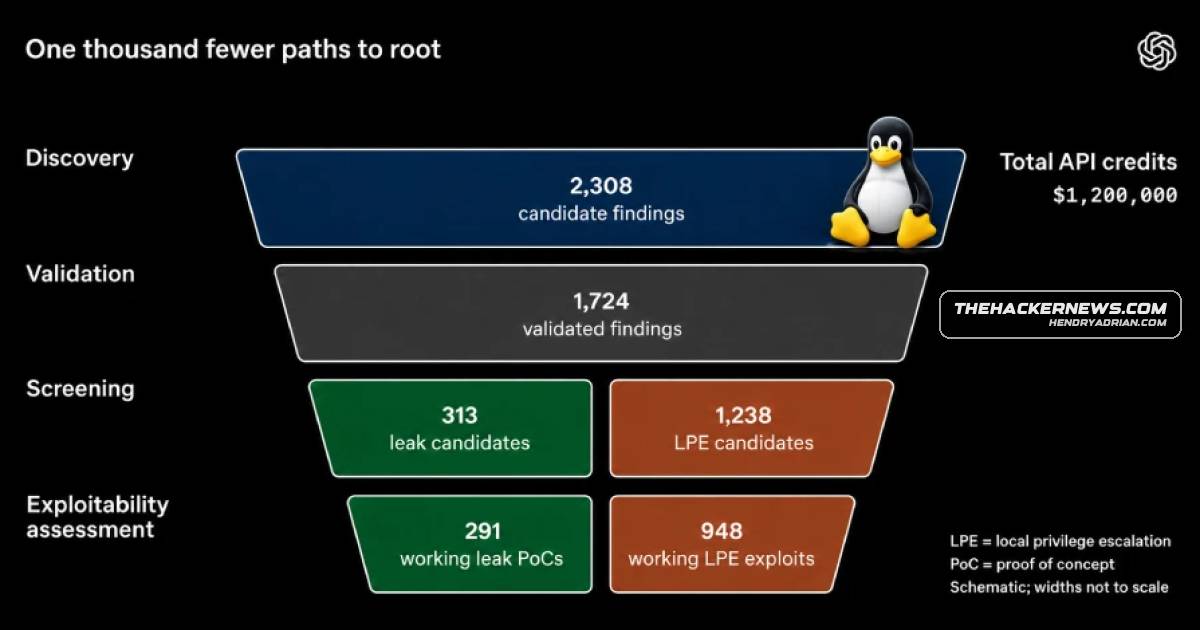
OpenAI says its AI pipeline reproduced 1,724 Linux vulnerabilities and generated 948 local privilege-escalation exploits in 30 hours, at a cost of $1.21 million. The company says automated patching must keep pace with AI-assisted discovery.
Key points
- OpenAI says the pipeline analyzed 2,308 candidate Linux kernel findings and dynamically reproduced 1,724 vulnerabilities.
- The run generated proof-of-concepts for 291 information-leak vulnerabilities and 948 working local privilege-escalation exploits for a commonly used Linux distribution.
- OpenAI reported the run took 30 hours and cost $1,213,430 in API credits, or $1,279 per LPE exploit.
- OpenAI said the agents discovered and used at least 10 novel Linux exploitation techniques; this is the company’s claim.
- The article cites Google Threat Intelligence Group figures showing monthly vulnerability disclosures more than doubled from 5,045 in January 2026 to 10,740 in August.
- The U.K. NCSC warned that AI tools can accelerate vulnerability discovery and patching, and said organizations need to adapt patching and testing processes.
Article Details
- Event Type
- OpenAI disclosed an AI-assisted pipeline for discovering Linux vulnerabilities, reproducing them, and generating local privilege escalation exploits and information-leak proof-of-concepts.
- Impact
- In a reported 30-hour run, the pipeline reproduced 1,724 vulnerabilities and generated 948 local privilege escalation exploits that could allow an unprivileged local user to gain root access, plus 291 information-leak proof-of-concepts. OpenAI reported API costs of $1,213,430. The article describes research results and potential security risk, not exploitation of systems in the wild.