
Worldleaks Claims Ransomware Attack on Equatorial Coca-Cola Bottling
Summary
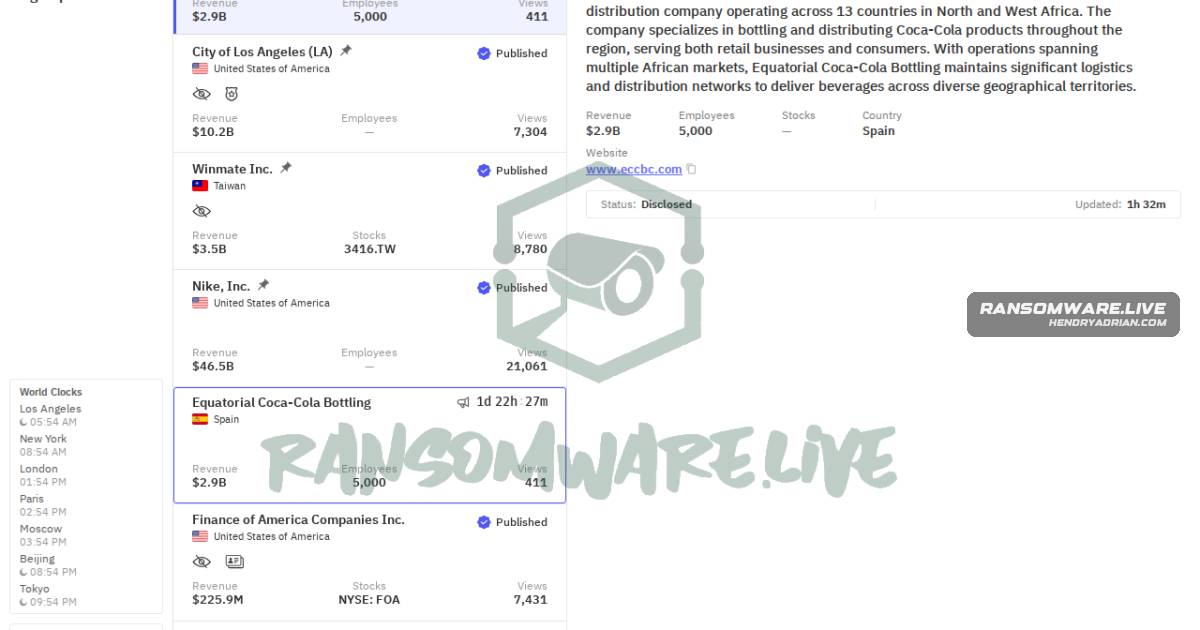
Worldleaks claims it breached Equatorial Coca-Cola Bottling, encrypted systems, and threatens to release stolen data. The post says the claims are unconfirmed.
Key points
- The named victim is Equatorial Coca-Cola Bottling.
- Worldleaks is identified as the actor; the claim is attributed to its leak-site listing.
- The group allegedly claims encryption and threatens to release stolen data; these assertions are unconfirmed.
- The post says the attack caused bottling and distribution disruption, but provides no independent confirmation.
- The record is attributed to ransomware[.]live monitoring.
Article Details
- Victim
- Equatorial Coca-Cola Bottling
- Claim Date
- 2026-04-22
- Encryption Status
- Claimed by Worldleaks; not independently confirmed by the source.
- Exfiltration Status
- Unconfirmed. The article describes potential data exfiltration and a threat to release stolen data.
- Exfiltrated Data
- Unspecified; the article says Worldleaks threatened to release stolen data but does not confirm exfiltration.
- Leak Status
- Threatened; the article does not report that data was published.